CISA added two security flaws to its Known Exploited Vulnerabilities catalog on Friday, citing evidence of active exploitation, and the two bugs are very different from each other, but both are being used in the wild right now.
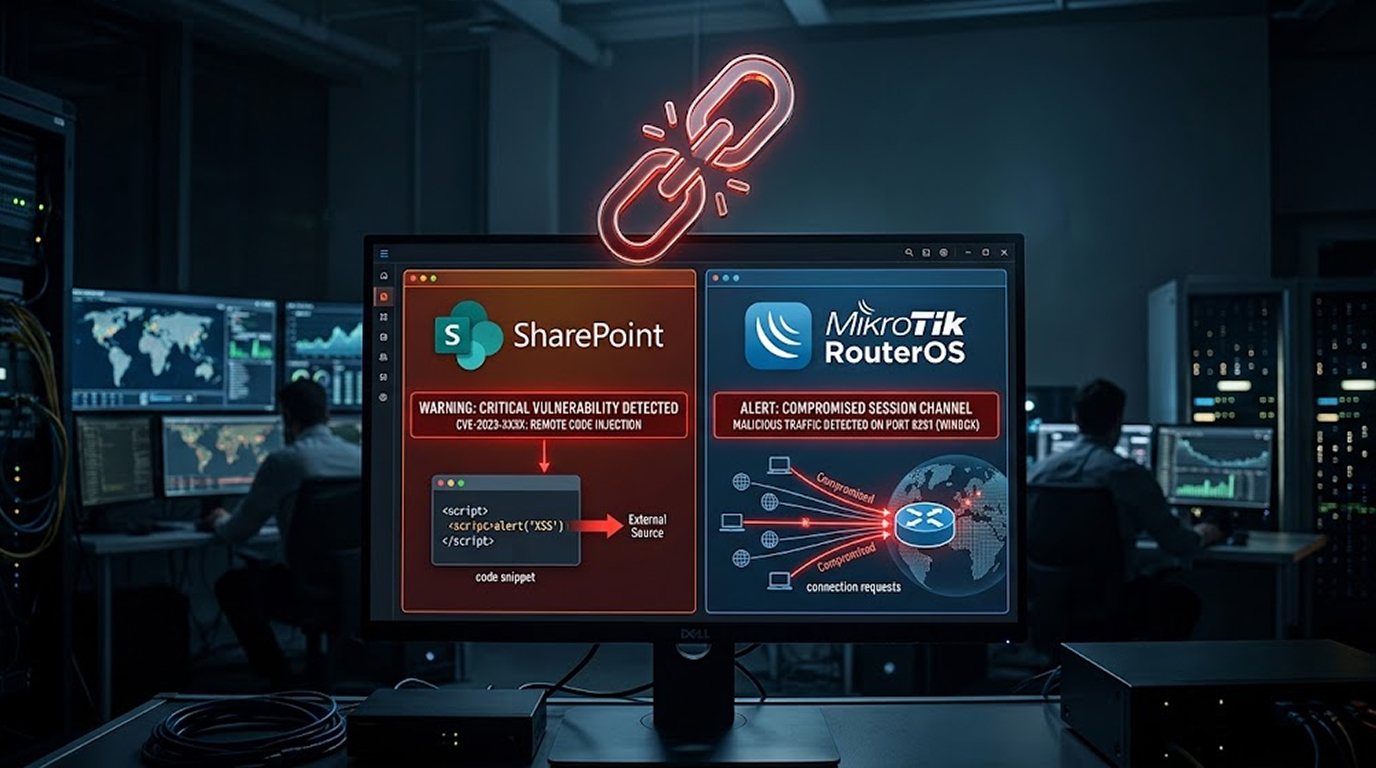
The first is CVE-2026-65660, a code injection vulnerability in Microsoft Office SharePoint with a CVSS score of 8.8, which allows an authorized attacker to execute code over a network, and the second is CVE-2026-67279, an improper enforcement of behavioral workflow vulnerability in Mikrotik RouterOS with a CVSS score of 6.9, which could allow an unauthenticated client to open a session channel and send an exec request.
As reported by The Hacker News earlier this week, CVE-2026-65660 was originally described by Microsoft as a spoofing vulnerability impacting SharePoint Server, but the tech giant has since updated the advisory to state that it could be abused to obtain remote code execution.
Quick Summary
|
CVE |
Product |
CVSS |
Impact |
|
CVE-2026-65660 |
Microsoft SharePoint |
8.8 |
Code injection, RCE |
|
CVE-2026-67279 |
MikroTik RouterOS |
6.9 |
Session channel, exec request |
The SharePoint Flaw
Microsoft updated its advisory to reflect the severity of CVE-2026-65660, noting that as of September 25, 2026, it had reliable evidence of observed attacks against exploitation of this vulnerability.
But Microsoft has not disclosed who was behind the exploitation efforts, when they started, how many organizations have been targeted, how many of them have been successful, and what attackers did once inside the vulnerable service, so the public picture is incomplete.
What we do know is that the flaw allows an authorized attacker to execute code over a network, and the fact that it was originally classified as spoofing and then upgraded to remote code execution suggests the impact was initially underestimated.
The MikroTik Flaw and the MikroTrick Chain
The second vulnerability added to the KEV catalog is CVE-2026-67279, which has been chained along with CVE-2026-86060, an argument injection flaw in the RouterOS login process, as part of an exploit codenamed MikroTrick.
The exploit chain has been used to take full administrative control of internet-exposed susceptible routers without needing a password, according to CERT Polska, and the Polish cybersecurity agency said combining the two vulnerabilities resulted in full unauthenticated access to the administrative console.
CVE-2026-67279 allowed an unauthenticated client to create a session channel, while CVE-2026-86060 allowed it to supply login with an attacker-controlled policy mask, so the two flaws work together to bypass authentication entirely.
In a separate analysis, Bishop Fox said it was able to reproduce the complete administrative takeover on vulnerable RouterOS 7.x builds, which confirms the chain works in practice and is not just theoretical.
Why the Chain Works
Security researcher Emilio Gallegos from Bishop Fox explained that MikroTrick combines two failures at different trust boundaries, with the first allowing an unauthenticated connection to reach functionality that RouterOS should expose only after login, and the second causing the login process to treat data from that connection as a trusted administrative identity.
He also said MikroTrick exposes a design risk in privileged software, where a feature intended only for trusted local callers becomes a remote attack surface when an upstream component loses track of authentication state.
That is a pattern worth remembering, because it shows how a small oversight in state management can turn a local-only feature into a remotely exploitable one.
The CISA Deadlines
CISA added CVE-2026-86060 to its KEV catalog on September 11, 2026, and now it has added CVE-2026-65660 and CVE-2026-67279 as well, so all three flaws are on the list.
Federal Civilian Executive Branch agencies have until September 28, 2026, to apply the necessary fixes, which is a short window that reflects the active exploitation.
What You Should Do
- Patch SharePoint immediately if you have not already, because Microsoft has confirmed observed attacks.
- Patch RouterOS to a fixed version, and check whether your routers have SSH or the administrative interface exposed to the internet, because the MikroTrick chain requires reachability.
- Review logs for signs of the MikroTrick chain, including the username -2 and the account ops, which were indicators from the CERT Polska analysis.
- Restrict administrative access to trusted networks, because both flaws are much harder to exploit when the target is not internet-facing.
- Monitor for unexpected code execution or new accounts on both SharePoint and RouterOS systems.
- Follow the CISA deadline if you are a federal agency, and treat it as a strong signal even if you are not.
The Bottom Line
CISA added a SharePoint code injection flaw and a MikroTik RouterOS workflow flaw to its KEV catalog, and both are being actively exploited, with the MikroTik bug forming part of the MikroTrick chain that gives unauthenticated attackers full administrative control of exposed routers, so if you run either product, patch now, check your exposure, and review your logs for signs of compromise.
Quick Reference
|
Key Point |
Detail |
|
CVE-2026-65660 |
SharePoint code injection, CVSS 8.8 |
|
CVE-2026-67279 |
MikroTik RouterOS workflow flaw, CVSS 6.9 |
|
Chain |
MikroTrick, with CVE-2026-86060 |
|
Impact |
Full unauthenticated admin access on RouterOS |
|
CISA Deadline |
September 28, 2026 |
|
Evidence |
Microsoft confirmed attacks, Bishop Fox reproduced |
What to Do
- Patch SharePoint and RouterOS
- Check for internet exposure
- Review logs for -2 and ops indicators
- Restrict admin access
- Monitor for unexpected code execution
- Follow CISA guidance
FAQ Section
What did CISA add to the KEV catalog?
CISA added CVE-2026-65660, a SharePoint code injection flaw, and CVE-2026-67279, a MikroTik RouterOS workflow flaw, both with evidence of active exploitation.
What is the MikroTrick chain?
It is an exploit chain that combines CVE-2026-67279 with CVE-2026-86060 to give unauthenticated attackers full administrative control of vulnerable RouterOS devices.
Has Microsoft confirmed attacks on SharePoint?
Yes, Microsoft said that as of September 25, 2026, it had reliable evidence of observed attacks against exploitation of CVE-2026-65660.
What is the deadline for federal agencies?
Federal Civilian Executive Branch agencies have until September 28, 2026, to apply the necessary fixes.
What should I do if I run these products?
Patch immediately, check for internet exposure, review logs for indicators like username -2 and account ops, restrict administrative access, and monitor for unexpected activity.