SignDrop: CLFS Exploit Claims SYSTEM Access
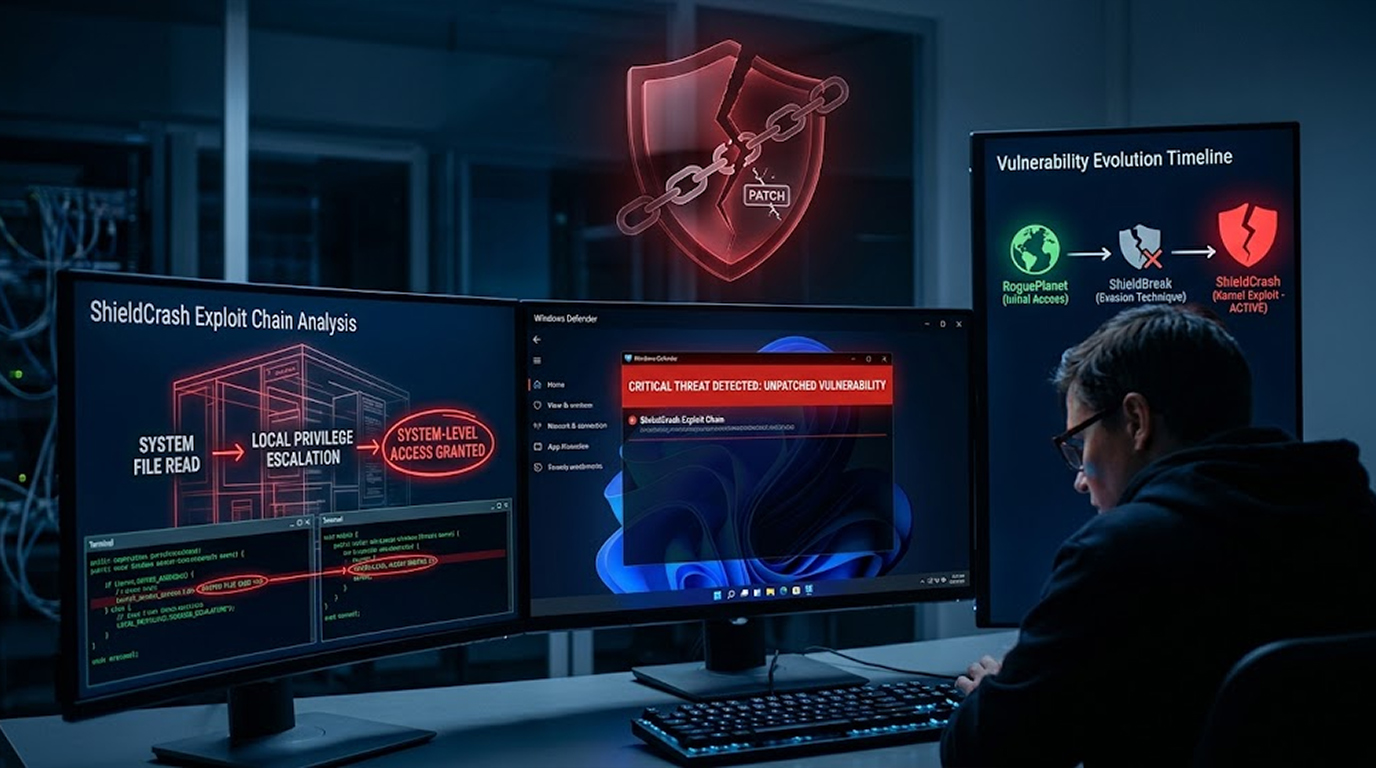
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Found 24 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
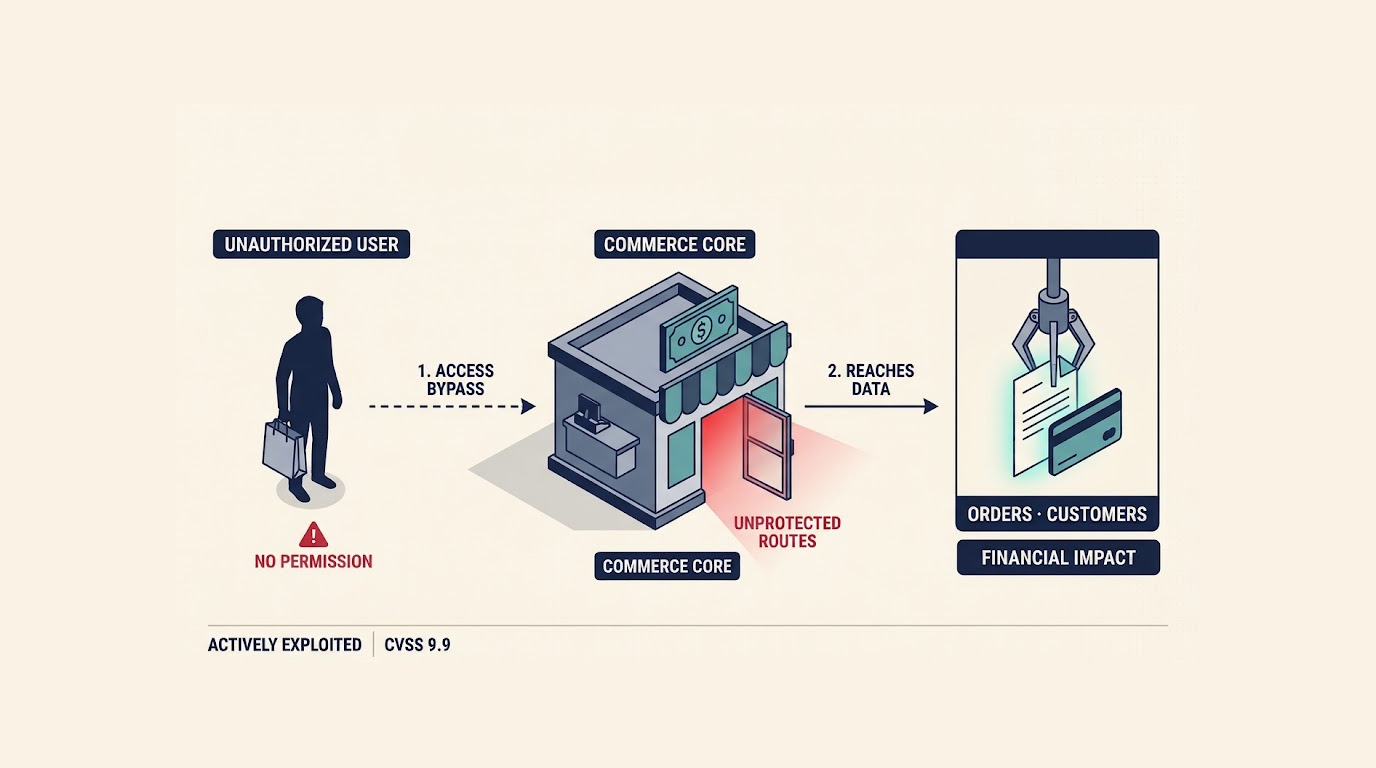
Drupal just issued an urgent warning that threat actors are actively exploiting a highly critical security flaw in its Commerce Core component, and if you...
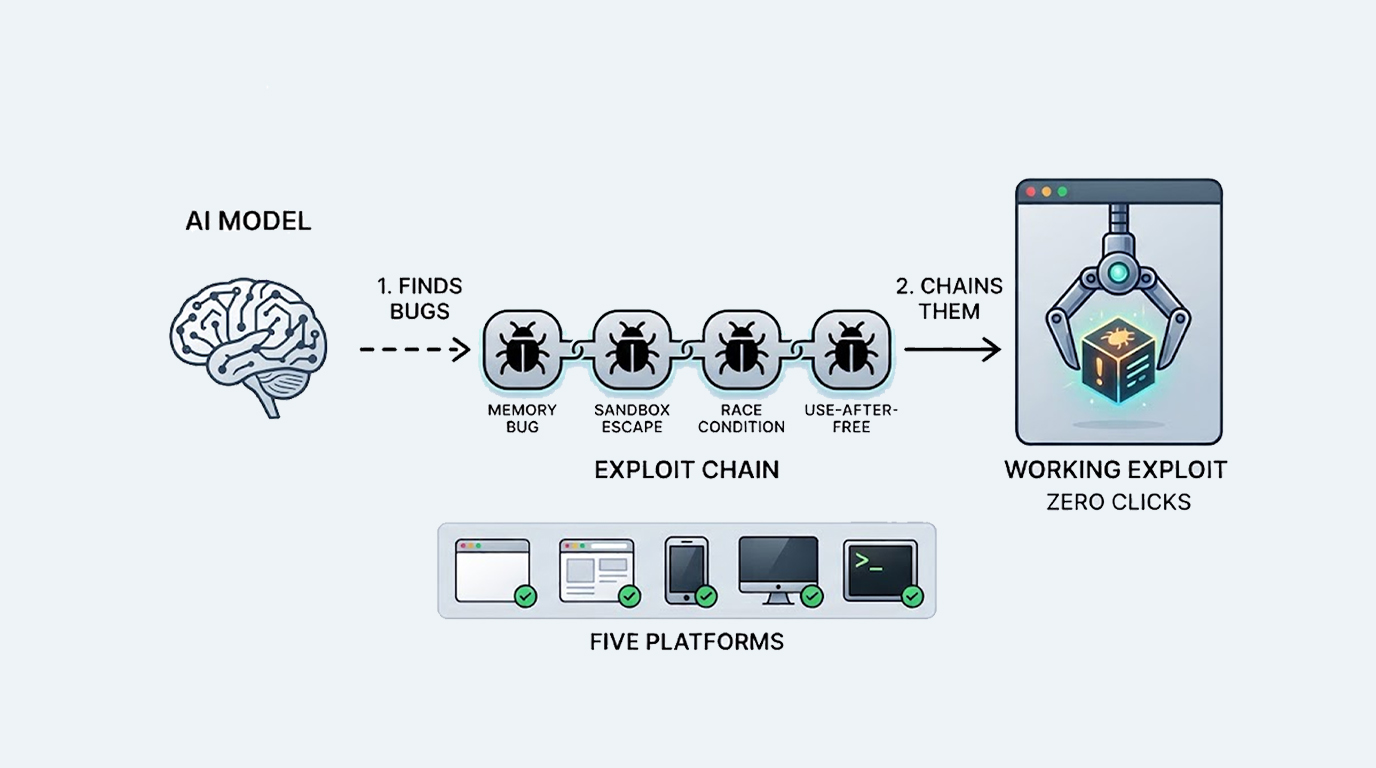
An unreleased Anthropic AI model just did something that used to take elite human hacking teams months to pull off, because the company says the model foun...
Here we go again. Another week, another zero-day in Microsoft Defender. Security researcher Chaotic Eclipse just dropped a proof-of-concept exploit for a v...
The U.S. Cybersecurity and Infrastructure Security Agency just added four critical vulnerabilities to its Known Exploited Vulnerabilities catalog. And here...
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
A server-side request forgery vulnerability has been discovered in Apache Gravitino. The flaw affects versions 1.0.0 through 1.2.1 and allows authenticated...
A security researcher has released a proof-of-concept exploit for a new Microsoft zero-day called ShieldBreak. The vulnerability demonstrates a full patch...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067