EDK II Flaw: 16-Year-Old UEFI Boot Vulnerability
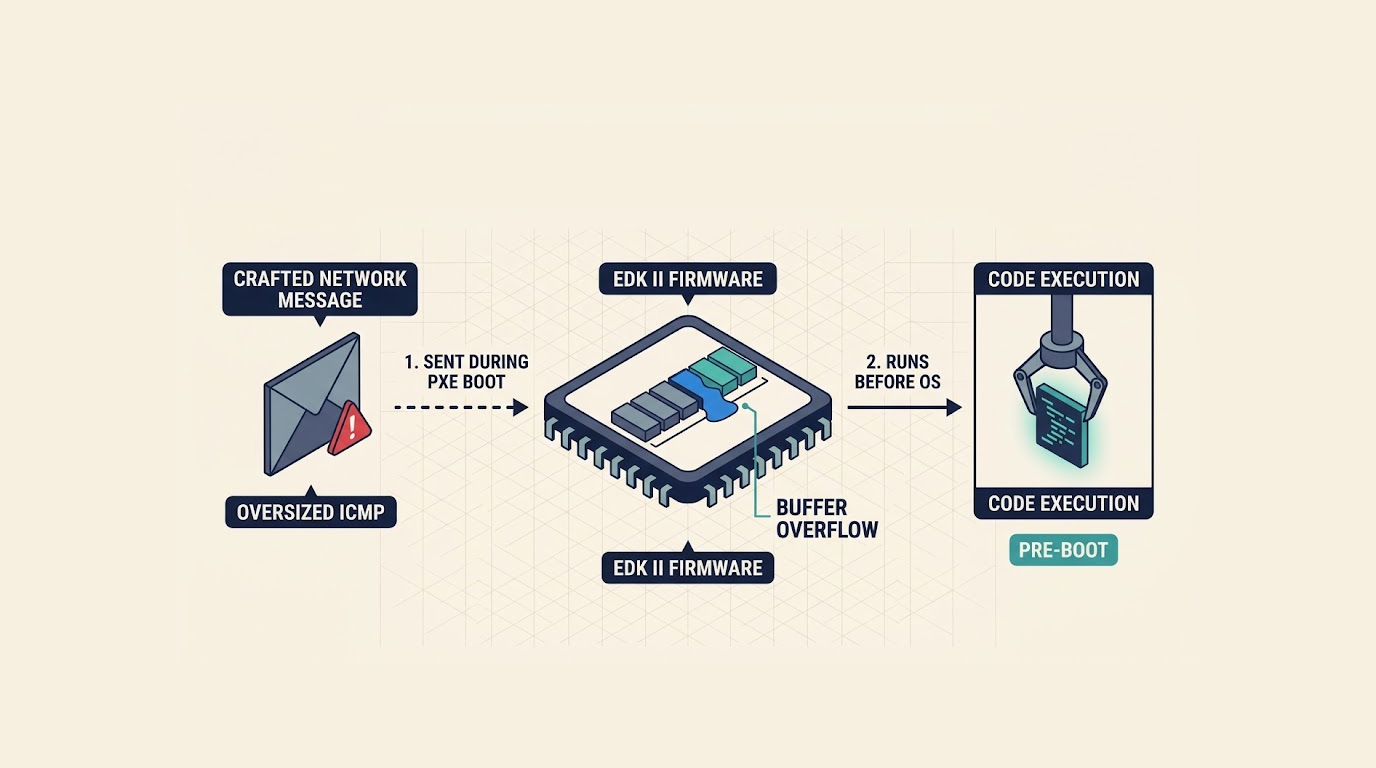
Your servers might be carrying a 16-year-old vulnerability in the firmware that boots them, because a critical buffer overflow in EDK II, the open-source c...
Found 29 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your servers might be carrying a 16-year-old vulnerability in the firmware that boots them, because a critical buffer overflow in EDK II, the open-source c...
Your Python application might be executing operating system commands just because it processed an image upload, because a critical Pillow EPS vulnerability...
Linux servers running KSMBD, the kernel's built-in SMB server, are currently exposed to two publicly reported remote code execution vulnerabilities, both c...
Your AnyDesk deployment on Linux might be accepting root-level commands from strangers, because security researchers just published a full working exploit...
There is an email sitting in a university researcher's inbox right now. It looks like a research proposal, or a conference invitation, or a document from a...
Google just pushed out a massive Chrome update. It patches 230 security vulnerabilities. One of them is a zero-day being actively exploited right now. The...
If you're running VMware Workstation or Fusion, you need to update right now. Broadcom just released patches for two security flaws. One is critical and co...
Cisco just dropped another round of security updates. This time, it's for Crosswork platforms and Secure Workload Software. The patches are part of a large...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067