Citrix NetScaler Zero-Days Under Active Exploitation
Two new zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway are being actively exploited in the wild, and as of September 26, Citrix has...
Found 11 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two new zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway are being actively exploited in the wild, and as of September 26, Citrix has...
Microsoft just released a record 206 Microsoft security patches for June 2026. That's not a typo. Two hundred and six fixes. Of these, 39 are rated Critic...
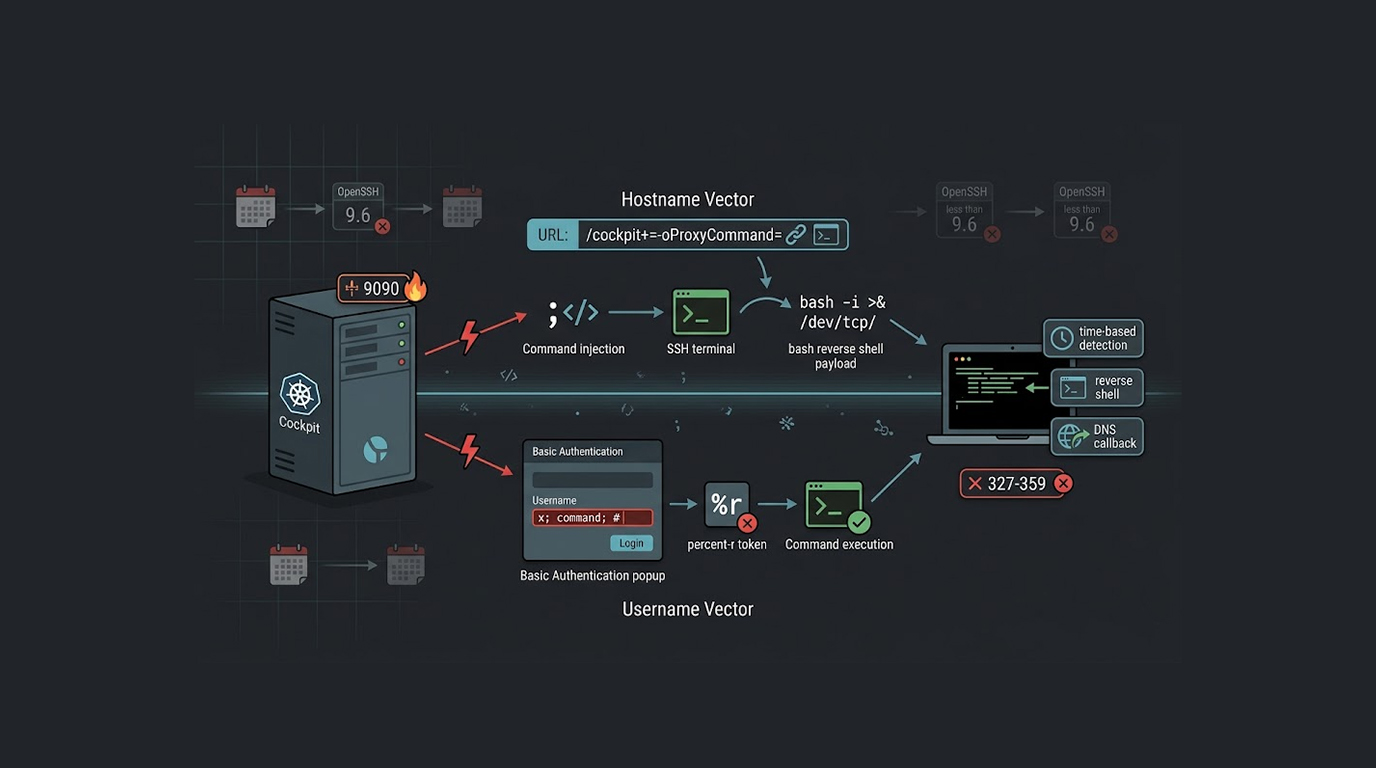
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
Most breaches we investigate don’t start with a zero-day or some elite attack technique.They start with something simple, a Windows setting left wide...
Attackers don’t waste time on fancy zero days unless they really need to. Most of the active exploitation you see today comes from old, unpatched, ea...
Let me tell you about a client I worked with last year. They had a Java-based web app running on Apache Tomcat, and everything “looked fine.” B...
Remote Code Execution (RCE) is one of the most dangerous types of cyberattacks, allowing an attacker to execute malicious code on a victim's system from a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067