GoAhead Web Server Flaw: CVE-2026-115881 Patch
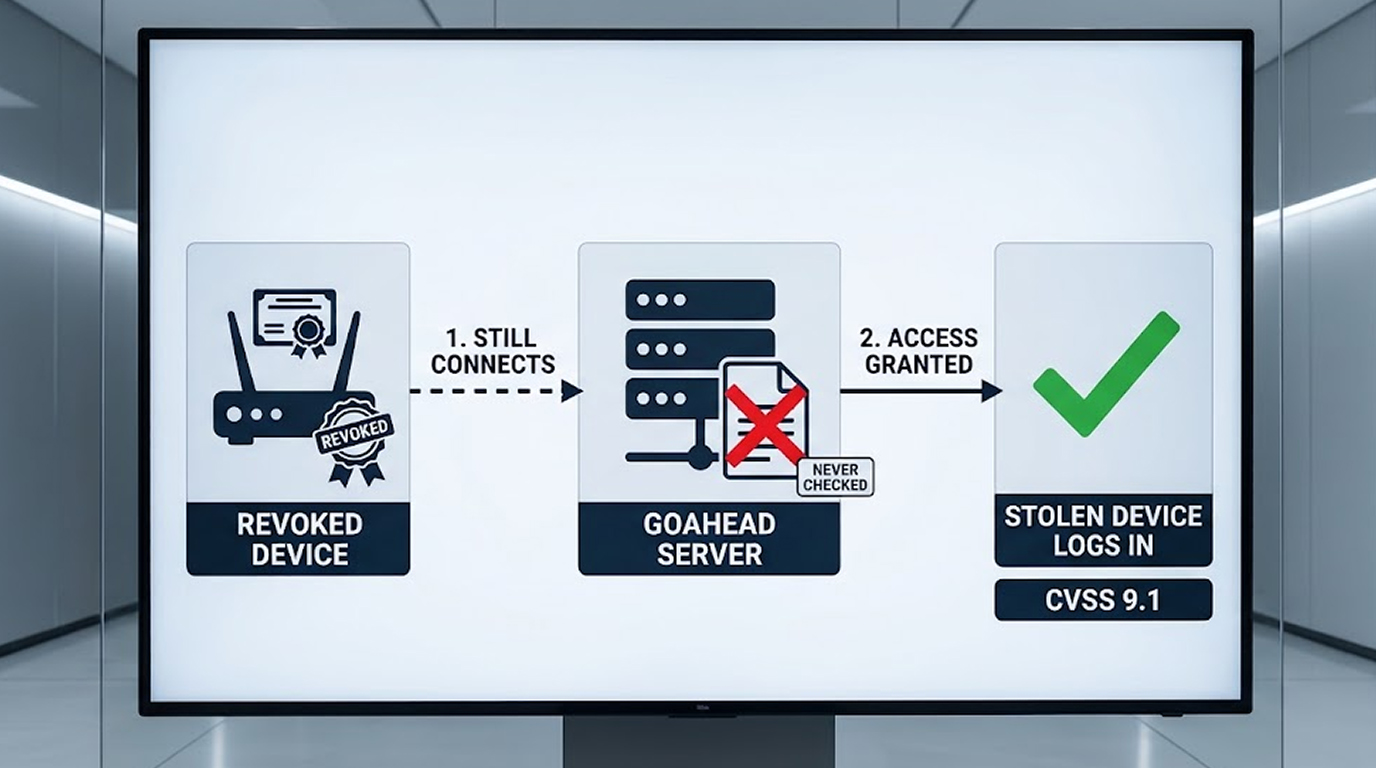
Your router, printer, or industrial controller might be accepting logins from stolen or retired devices, because a critical flaw in the GoAhead embedded we...
Found 8 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your router, printer, or industrial controller might be accepting logins from stolen or retired devices, because a critical flaw in the GoAhead embedded we...
Your Node.js server might be running code that can be crashed or compromised by a malformed request, because the project just released security updates fix...
If you're using the miniOrange SAML 2.0 Single Sign On plugin for WordPress, you need to update right now. A critical flaw is being actively exploited. Att...
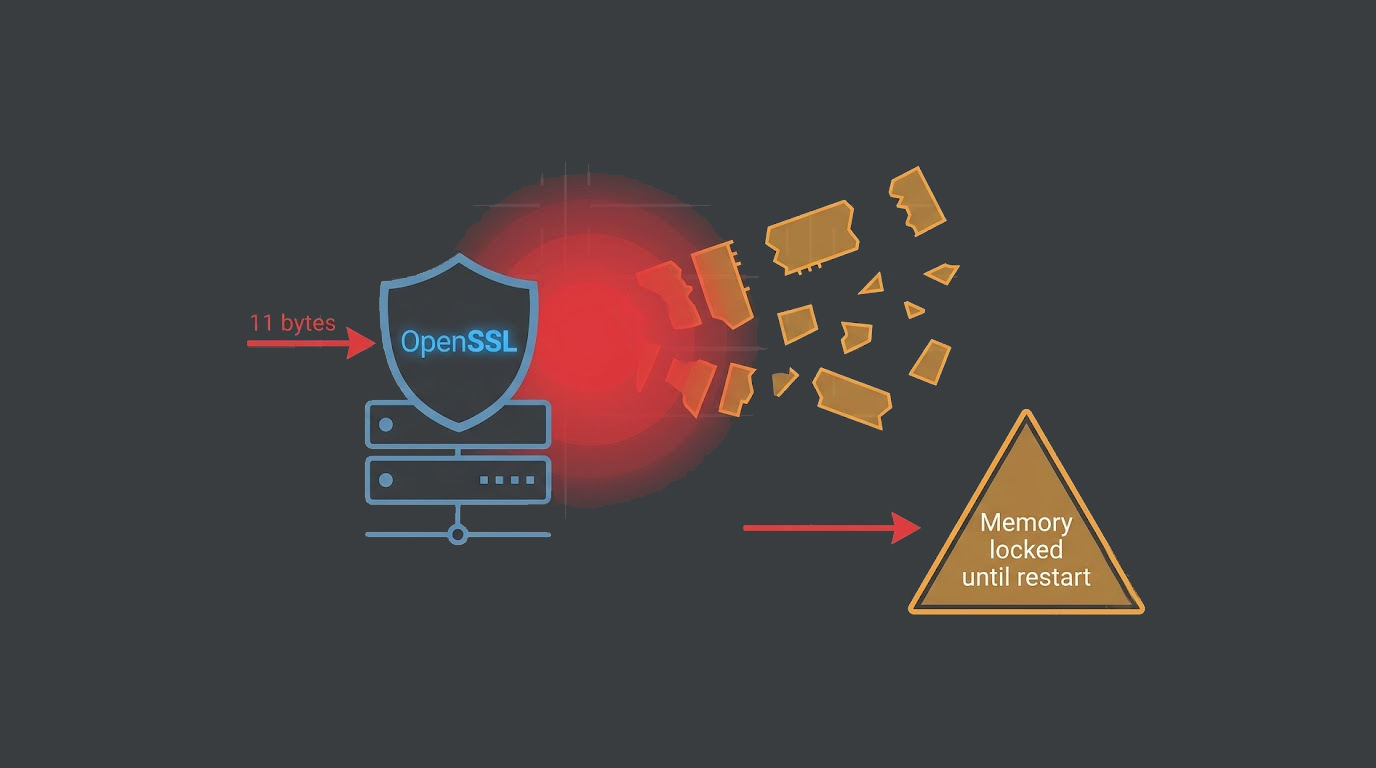
Eleven bytes. That's all it takes to make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On systems running...
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
Active Directory Certificate Services (AD CS) is everywhere in enterprise Windows environments. And everywhere means opportunity.If you have done any inter...
Free and open-source software (FOSS) powers most of the internet, mobile devices, servers, cloud infrastructure, IoT products, and even many proprietary ap...
Email spoofing is not a new threat.What has changed is how quietly it succeeds.Modern spoofing rarely depends on obvious fake addresses or poor language.It...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067