Data Theft Extortion: How UNC3753 Strikes in Hours
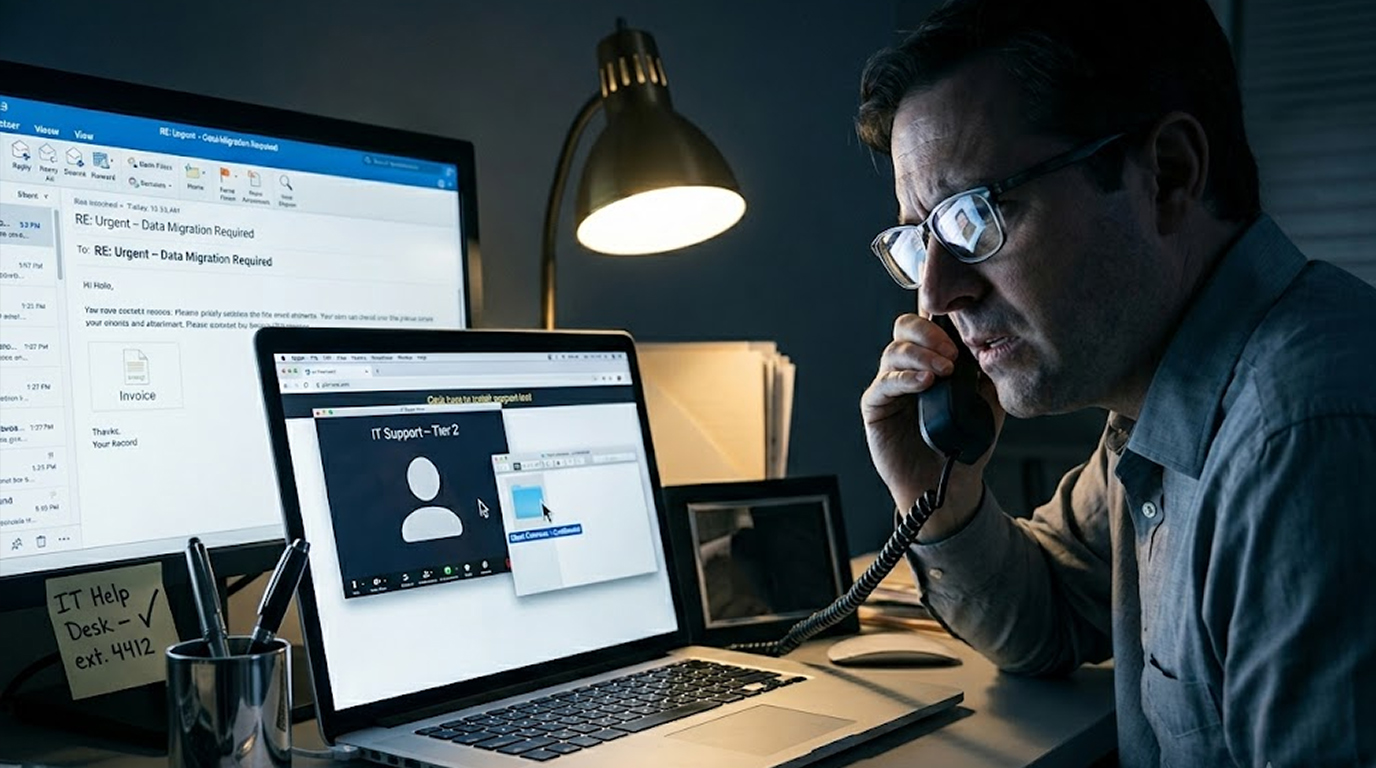
You expect phishing emails. You train your team to spot suspicious links. But what happens when the attacker calls you directly and sounds exactly like you...
Found 12 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You expect phishing emails. You train your team to spot suspicious links. But what happens when the attacker calls you directly and sounds exactly like you...
You do not have time for a 20-page threat intelligence report. You have a board meeting in an hour. Your SOC is flagging anomalies. And there is a new thre...
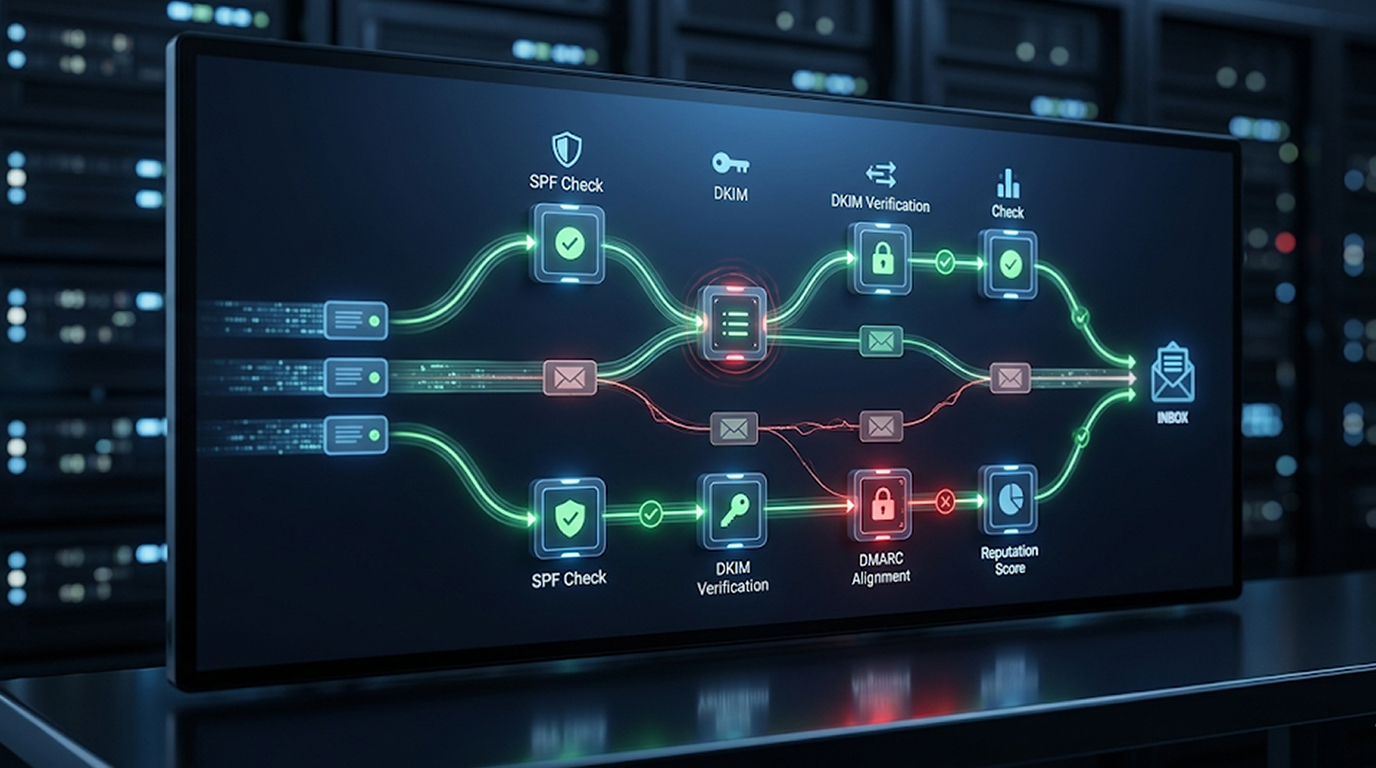
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Email is the single most abused tool in cybercrime. It carries everything: invoices, contracts, passwords, links, and sometimes the keys to your business....
Cybercriminals don’t always rely on advanced hacking techniques to compromise systems. Sometimes, they exploit the most basic human trait—curio...
Phishing remains one of the most effective cyberattack methods, tricking users into revealing sensitive information or installing malware. To combat this t...
Cybersecurity breaches continue to dominate headlines, exposing vulnerabilities in even the most secure systems. Examining real-world hacking incidents hel...
A newly discovered malware campaign, dubbed Horns&Hooves by Kaspersky, has been targeting private users, retailers, and service businesses primarily in...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067