Arista VeloCloud Vulnerability Under Active Exploitation
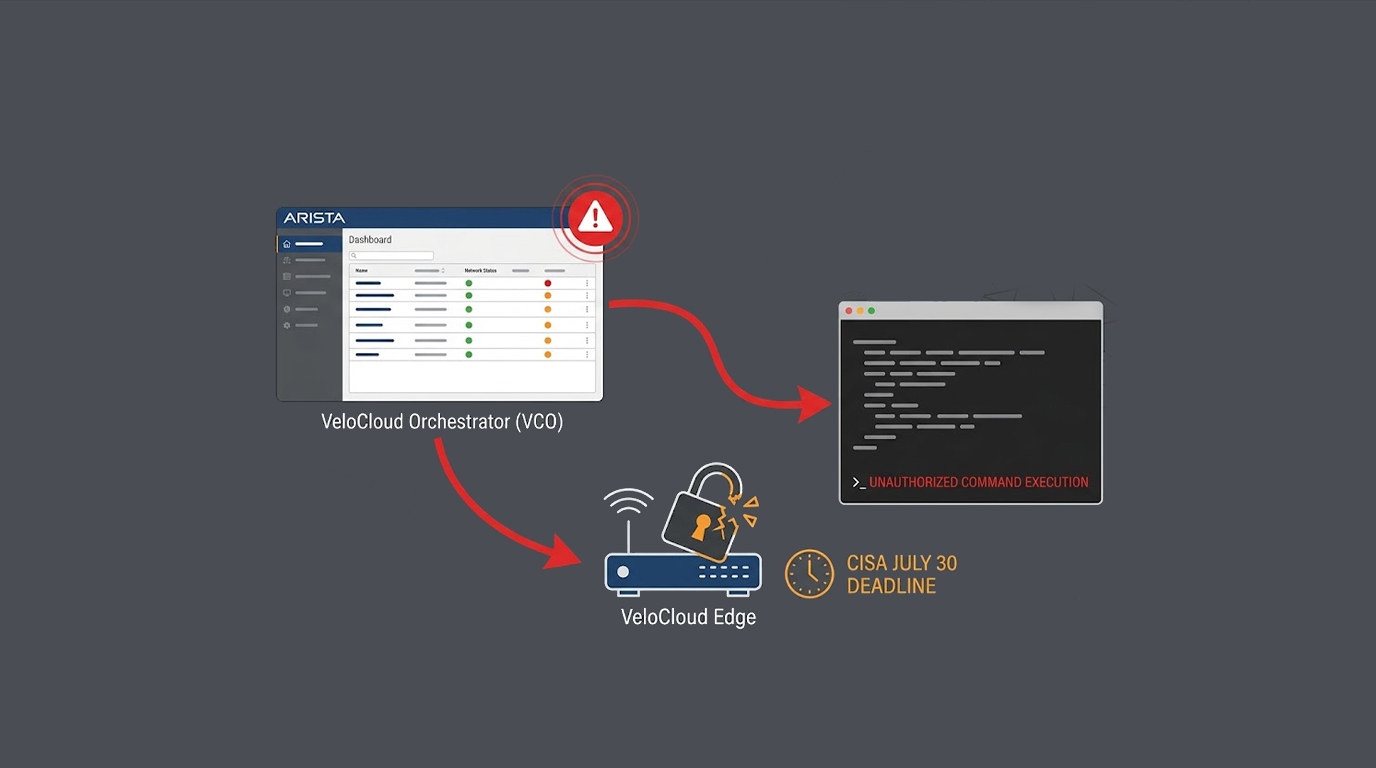
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
Found 13 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
Remember the script kiddie, that cliché of a teenage hacker sitting in their parents' basement, running pre-written code they barely understood, cli...
The trends described here are already visible in 2026. By 2027, they will be the new normal. This is not a prediction. It is a warning. You are a CISO pre...
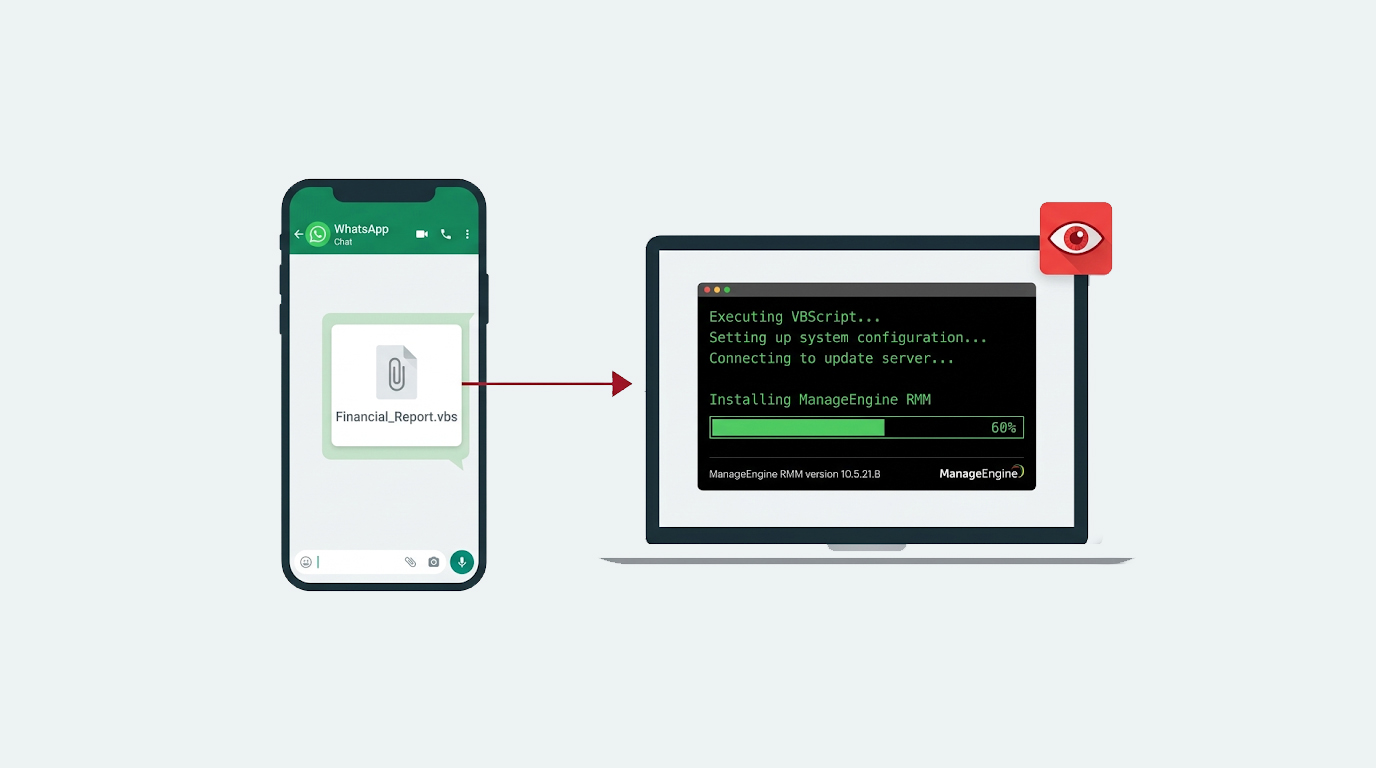
You receive a WhatsApp message from a contact you know. It includes an attachment named "Financial Reports.vbs." They don't explain what it is. They don't...
The Gentlemen ransomware-as-a-service operation is actively developing and maintaining a suite of EDR killers that it hands out to affiliates. The goal is...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
According to cybersecurity investigations into an active attack on government organisations in Southeast Asia, there was a zero-day vulnerability in TrueCo...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067