Preparing Your Web Application for AI-Driven Attacks
You have done everything right. Firewalls. WAF rules. Rate limiting. You feel pretty good about your security posture. Then an AI agent shows up. It does...
Found 17 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have done everything right. Firewalls. WAF rules. Rate limiting. You feel pretty good about your security posture. Then an AI agent shows up. It does...
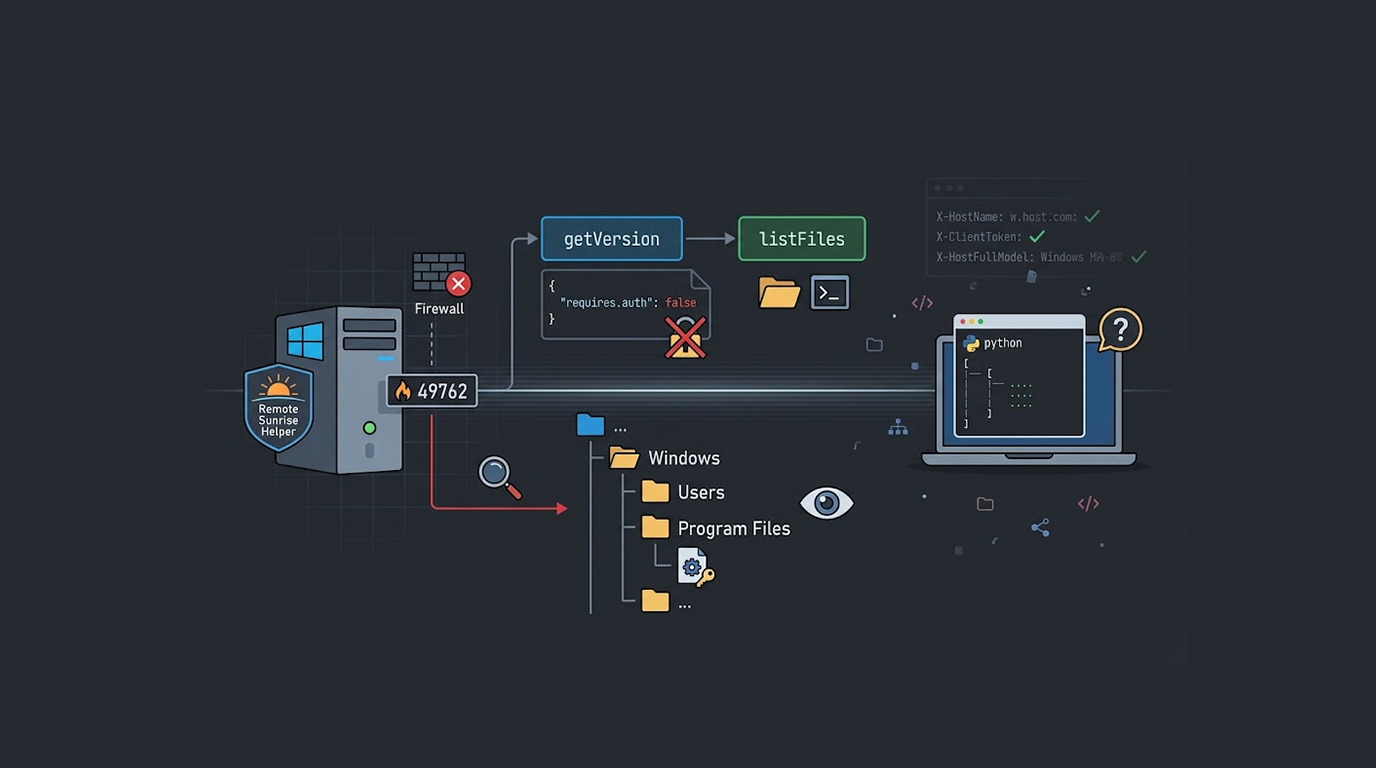
An issue with Remote Sunrise Helper, made by RS Ltd for Windows, allows unauthorized users access to view all files and folders on the device and has since...
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
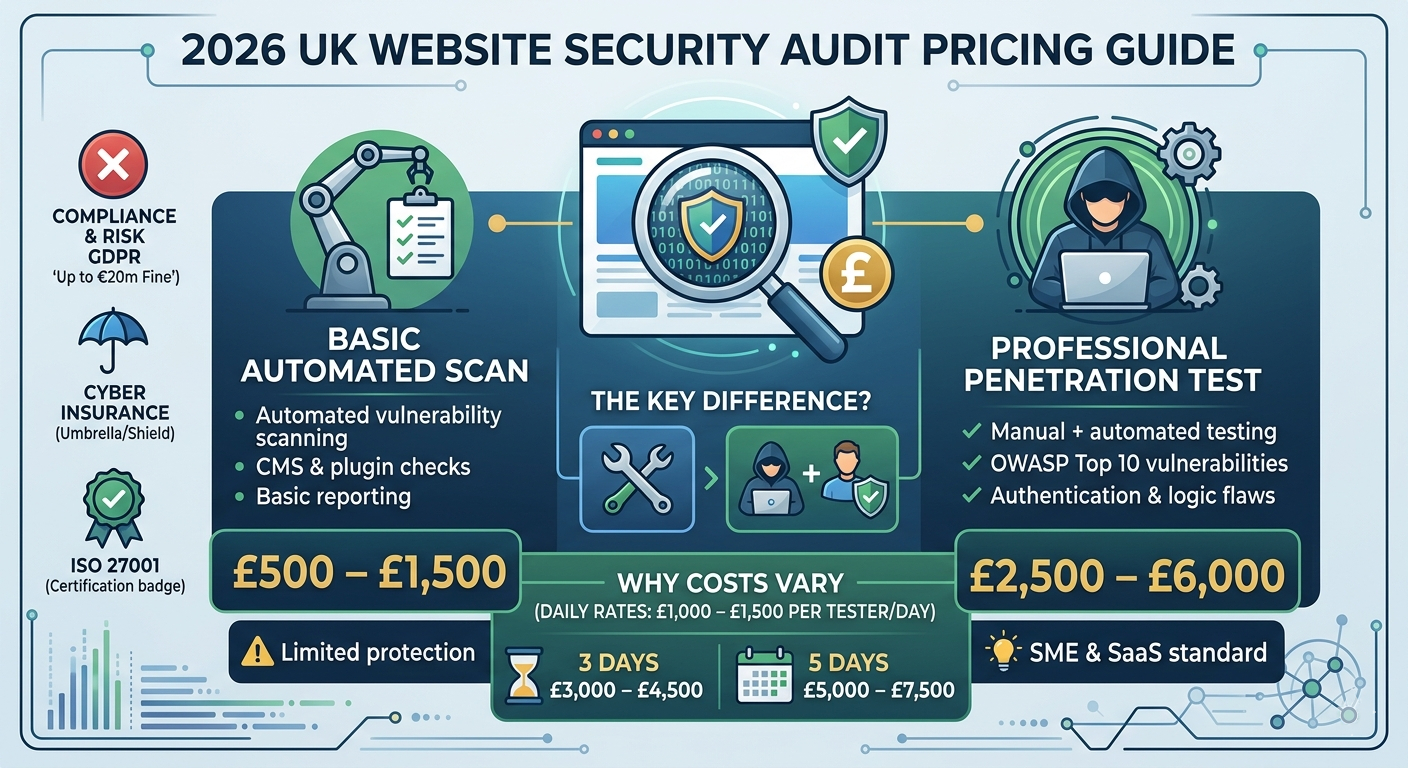
If you're researching website security audit cost in the UK, you’ve probably noticed something confusing: Some providers charge £500… o...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
The mobile app wasn’t hacked.The API was trusted too much.That trust exposed user data—quietly, consistently, and at scale.This is one of the m...
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
High severity vulnerabilities in 2026 are rarely exotic.Most incidents still come from:1. Simple trust assumptions2. Unsafe defaults3. Overexposed internal...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067