Xen Flaws: Guest VMs Can Read Dom0 Memory
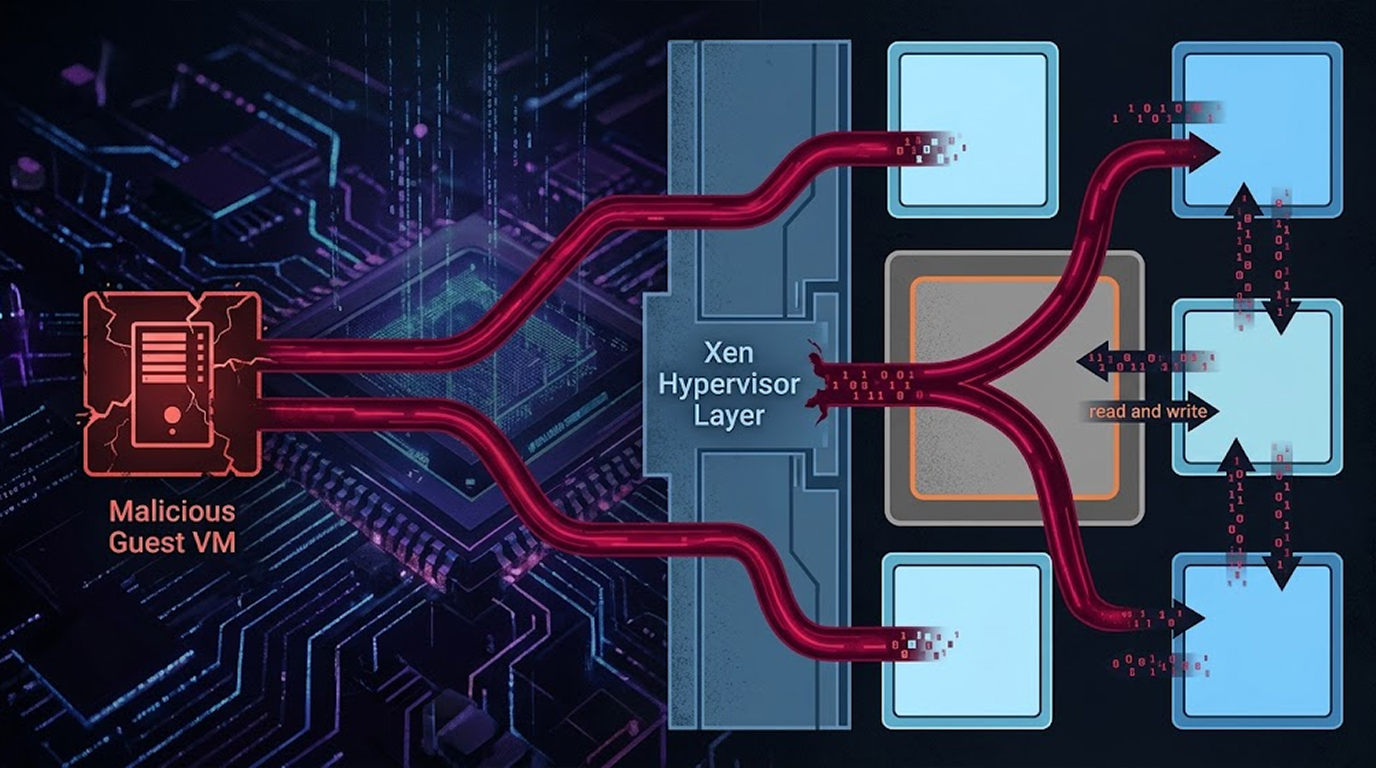
Two flaws in the Xen hypervisor allow a malicious guest virtual machine to read and write the memory of other VMs on the same host. That includes dom0, the...
Found 52 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two flaws in the Xen hypervisor allow a malicious guest virtual machine to read and write the memory of other VMs on the same host. That includes dom0, the...
Most explanations of AI vulnerability discovery stop at the vague sentence that the model reads your code and spots weaknesses, which is unhelpful if you'r...
An AI agent working on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, and Prime...
You download a pre-trained model from a public repository, it works great in testing, and you are ready to push it to production, but here is the thing, th...
Your company is deploying AI faster than your security team can track it, models are spinning up in cloud environments, agents are connecting to internal s...
You know the drill. Traditional penetration testing takes forever. It costs a fortune. And it happens once or twice a year, if you are lucky. Static scann...
Most security teams are drowning in work. There are applications to test, compliance deadlines to hit, and a never-ending stream of vulnerabilities to chas...
Your open source AI security roadmap for 2027 starts right here. This is your playbook for keeping artificial intelligence systems safe in a world where cy...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067