Telegram Desktop Flaw Hid JavaScript in HTML Exports
Here's a weird one. A flaw in Telegram Desktop let a bot slip JavaScript into your chat exports. If you saved a chat as an HTML file and opened it in a bro...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
Here's a weird one. A flaw in Telegram Desktop let a bot slip JavaScript into your chat exports. If you saved a chat as an HTML file and opened it in a browser, that script could run. It could steal e...
Read Full ArticleHere's a weird one. A flaw in Telegram Desktop let a bot slip JavaScript into your chat exports. If you saved a chat as an HTML file and opened it in a bro...
You have probably heard the warning, do not unpickle untrusted data, and you probably nodded along because it makes sense, pickle is dangerous, we know thi...
A Twitch browser extension has been quietly sending user login tokens to proxy servers run by a Russian bot service. Nearly 31,000 people are affected acro...
You download a pre-trained model from a public repository, it works great in testing, and you are ready to push it to production, but here is the thing, th...
You get an email from your CEO, it looks completely normal, the tone is right, the signature is right, and it references a real project you have been worki...
Microsoft just published details on two separate campaigns that are causing real problems for organizations. One is a financial fraud operation that sent o...
Your company is deploying AI faster than your security team can track it, models are spinning up in cloud environments, agents are connecting to internal s...
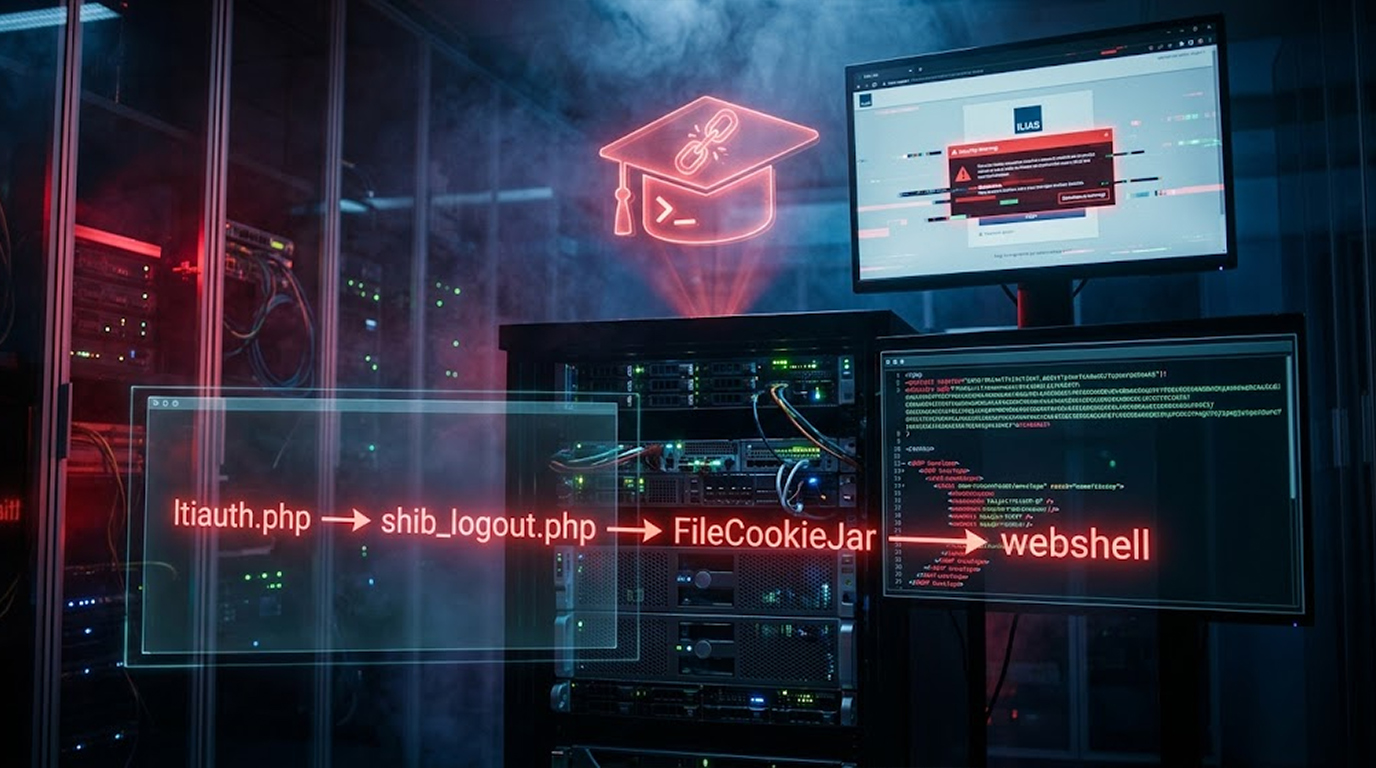
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067