Personalized Ad Injection: When Ads Know You
There's a version of malvertising that's easy to catch, which is the one where a poisoned ad creative reaches everyone who loads the page, and a scanner so...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There's a version of malvertising that's easy to catch, which is the one where a poisoned ad creative reaches everyone who loads the page, and a scanner so...
A 5.5 medium-severity vulnerability just landed in CISA's Known Exploited Vulnerabilities catalog, and the reason is a lesson every security team should in...
If you've read a headline claiming that roughly half of AI-generated code fails security testing, the number itself is less interesting than what it descri...
Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes. The incident prompted the WordPress plugins...
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
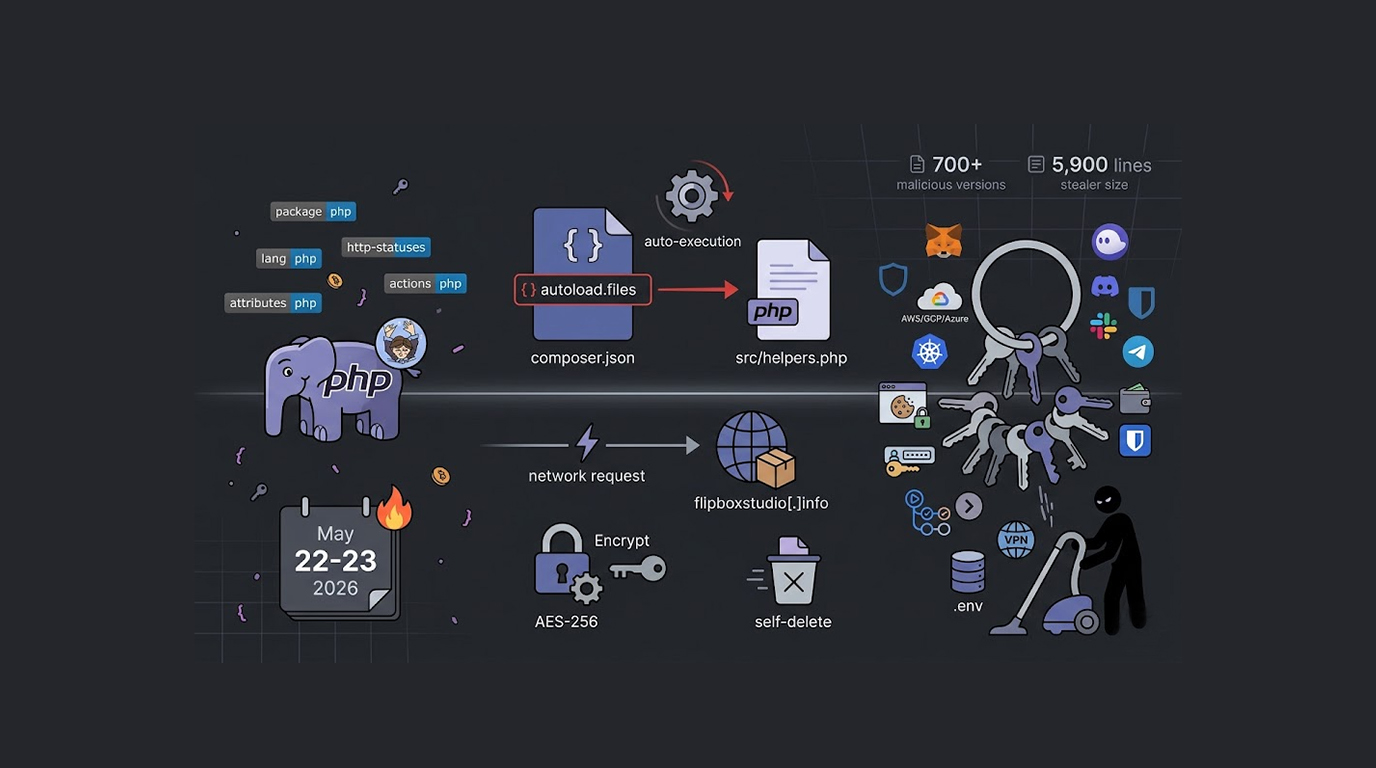
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
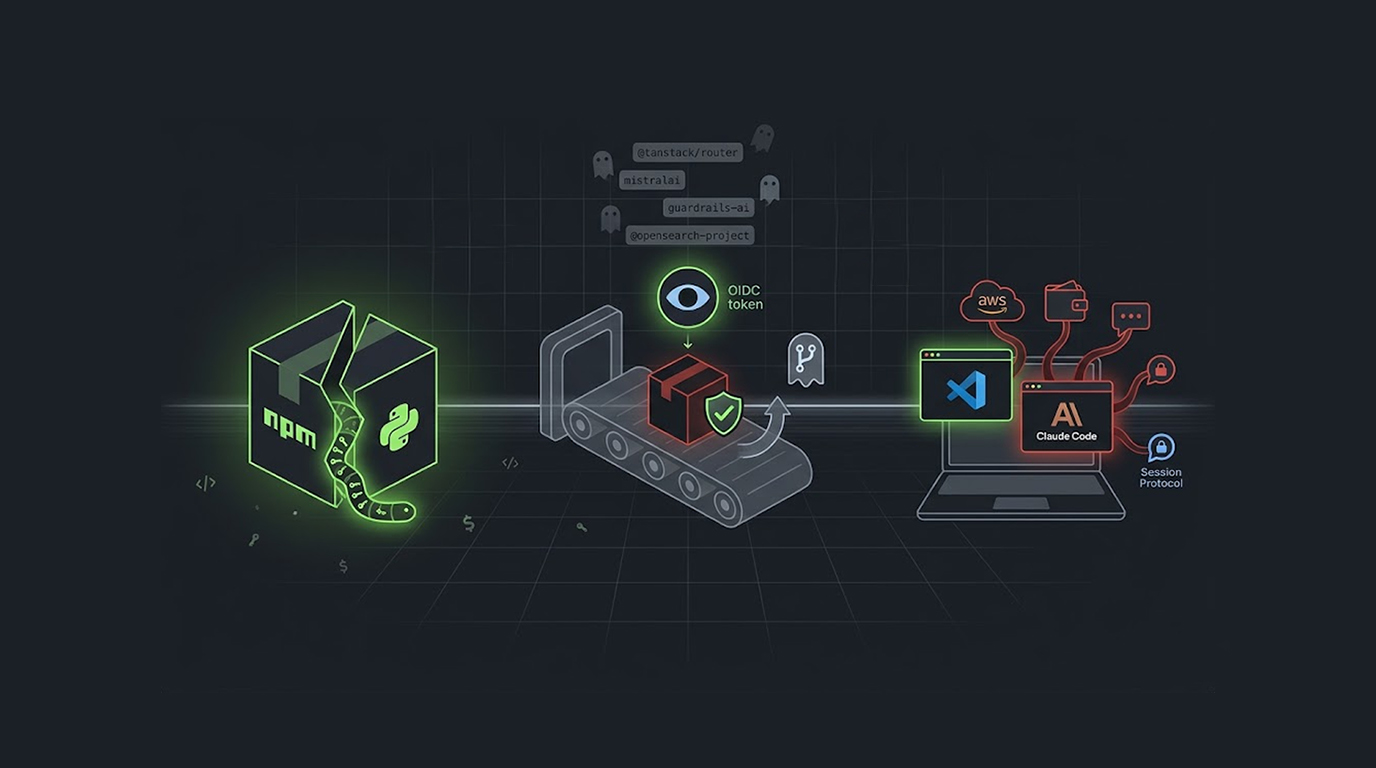
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
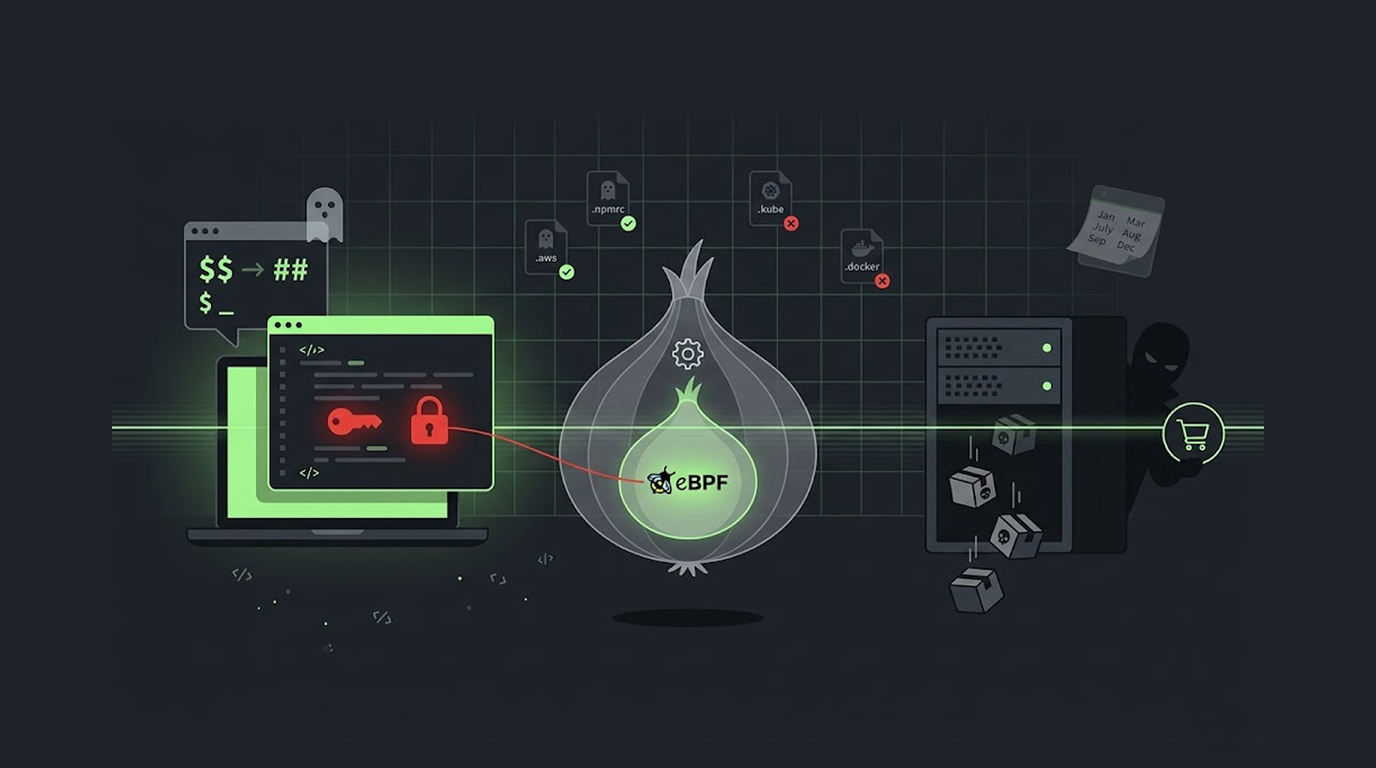
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067