AnyDesk Linux RCE: AnyPwn Exploit Patch Guide
Your AnyDesk deployment on Linux might be accepting root-level commands from strangers, because security researchers just published a full working exploit...
Found 16 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your AnyDesk deployment on Linux might be accepting root-level commands from strangers, because security researchers just published a full working exploit...
Microsoft has warned about phishing campaigns that distribute an installer for MSP360 Remote Monitoring and Management software, and the lures are the usua...
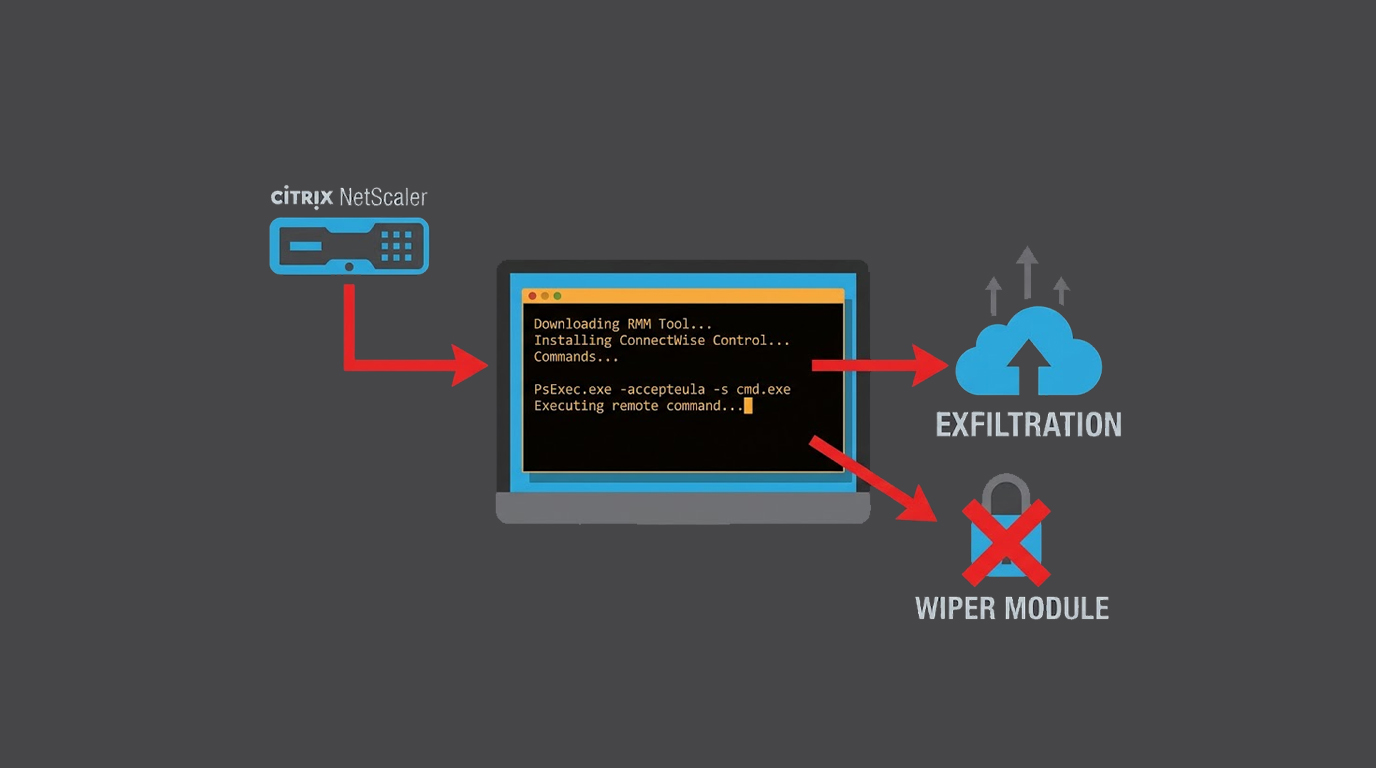
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
You receive an email from a company you work with. Your payroll provider, your cloud storage vendor, your marketing agency, your IT support company. "We h...
You wanted to recover a forgotten password. You searched online, found a "free password cracker," and downloaded it. The software did not work, maybe it cr...
Getting attackers out of a system or network feels like a win. But in many real cases, they come back. Why? Because they leave hidden ways in before you ev...
Fake crack files are one of the most common malware delivery methods today.They don’t target experts.They target normal people trying to save time or...
Most ransomware attacks do not begin with malware.They begin with trust being misused.Attackers succeed because:1. They use tools already present in enviro...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067