Optimizely Injection: 178 Sites Served Malicious Code
The trust model behind third-party experimentation tools is simple. You put a script tag on your page, the vendor serves the code, and you trust the vendor...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The trust model behind third-party experimentation tools is simple. You put a script tag on your page, the vendor serves the code, and you trust the vendor...
Google just took down the command servers for a botnet spanning more than 1.3 million Android devices, and the finding behind it is worse than a breach. Go...
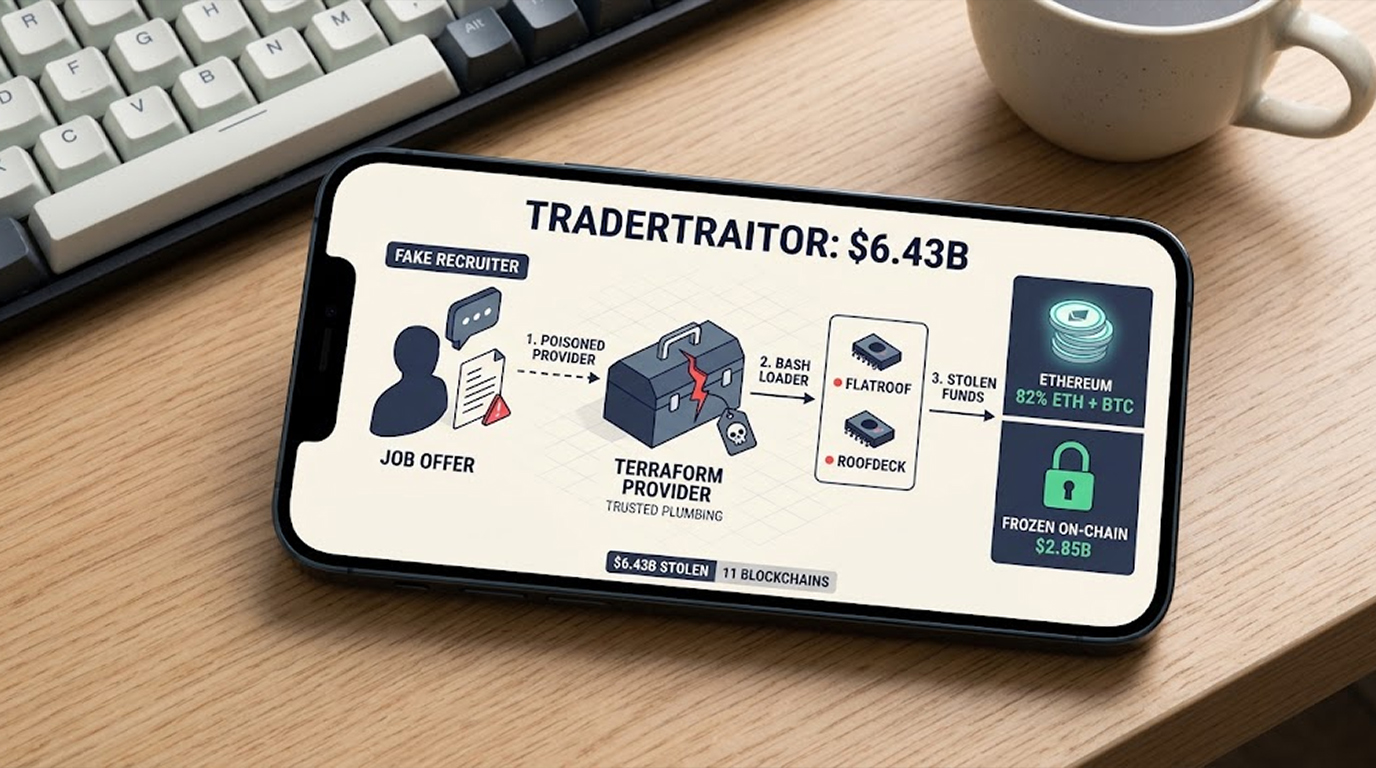
Six billion dollars. That is the number the FBI put on a single hacking operation this week, and it belongs to TraderTraitor, a North Korean crew that also...
Prediction market Polymarket just got hit by a classic supply chain attack, and it is a brutal reminder that even a secure smart contract can be undone by...
Most malware you read about wants files, which means documents, credentials, or customer records, and the damage gets measured in what was copied and how m...
You're sitting in a coffee shop, or on a train, or in a lecture hall, and your phone buzzes with a popup saying someone nearby wants to share a file with y...
Your AI gateway might have handed over cloud credentials to an attacker this week, because LiteLLM just disclosed a severe compromise that pushed a malicio...
Website Malware Removal: The Complete Guide Website malware removal is the process of identifying malicious code on a compromised website, removing infect...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067