Siemens IoT2050 Flaw: CVSS 10.0 Under Attack
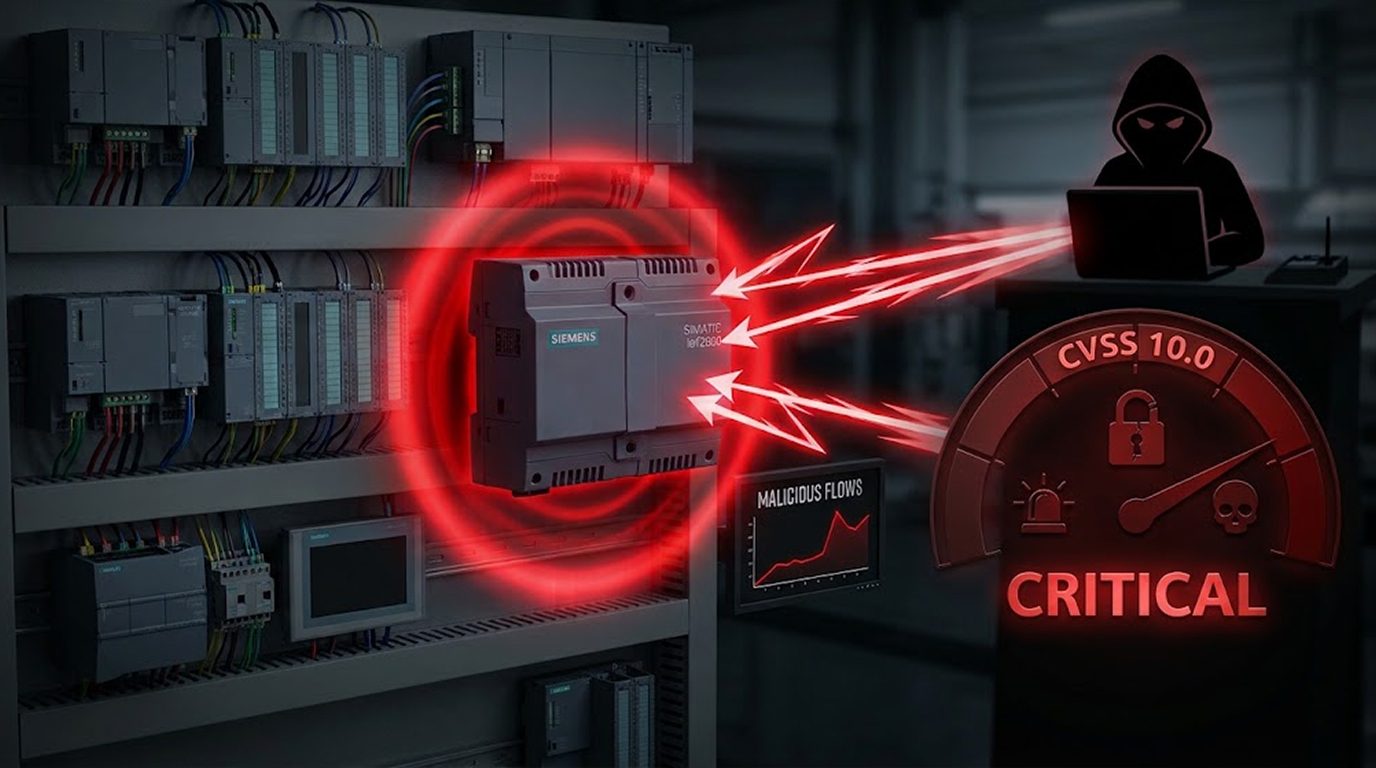
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
Found 8 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
One of the most stealthy ways that attackers have been able to leak sensitive information out of a network is by conducting “DNS exfiltration.”...
Sponge-style malware, the quiet, patient threats that slowly soak up credentials, documents, browser data, and session tokens is already a serious problem...
In recent months, Cisco Talos has identified a new modular malware framework referred to as VoidLink. The framework was discovered to have been utilized an...
DNS is the internet’s address book. When your browser wants example.com it does not magically know where to go. It asks DNS. That “ask” i...
When I teach a class or walk into a red-team briefing, someone always asks the same thing - “so, what exactly is a payload?” It’s one of...
Have you ever wondered how Windows sometimes blocks a sneaky PowerShell one-liner or a weird macro before anything bad happens? That’s often AMSI doi...
A reverse shell is a technique used to get remote command-line access to a computer, but the important twist is who starts the connection. In a normal &ldq...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067