PHP2Shell Flaw: Critical PHP RCE Patch Now
Your server might be running a language runtime that can be exploited by anyone who sends the right request, because PHP just released emergency updates fo...
Found 17 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your server might be running a language runtime that can be exploited by anyone who sends the right request, because PHP just released emergency updates fo...
Most security teams are drowning in work. There are applications to test, compliance deadlines to hit, and a never-ending stream of vulnerabilities to chas...
You are a security engineer. You have spent months building defenses. Firewalls, intrusion detection, zero-trust architecture. You feel confident. Now ima...
Entra ID researcher Dirk-jan Mollema has uncovered a technique that allows malware already running on a compromised Windows machine to silently use a victi...
Is your business truly safe from a cyberattack? Many managers and entrepreneurs are somewhat ignorant toward digital resources, so many of them feel that...
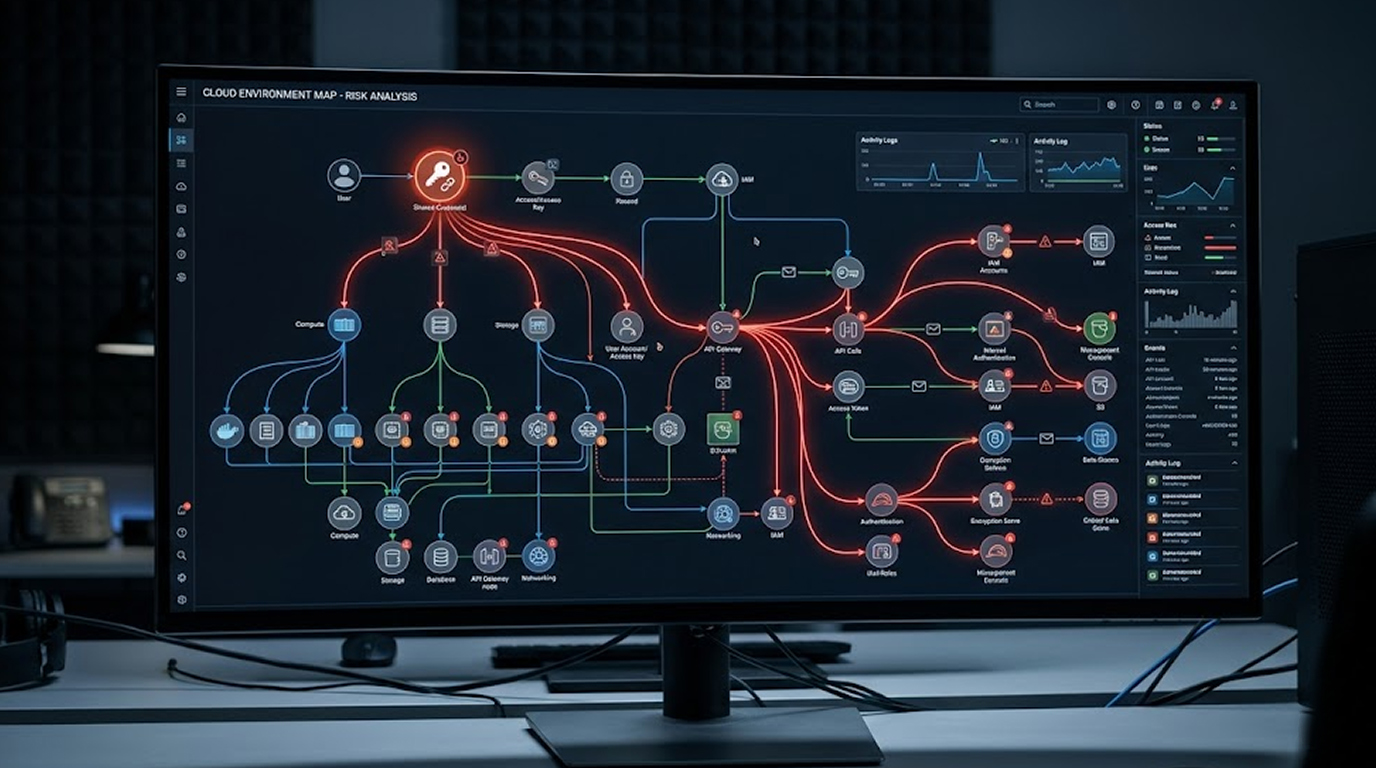
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
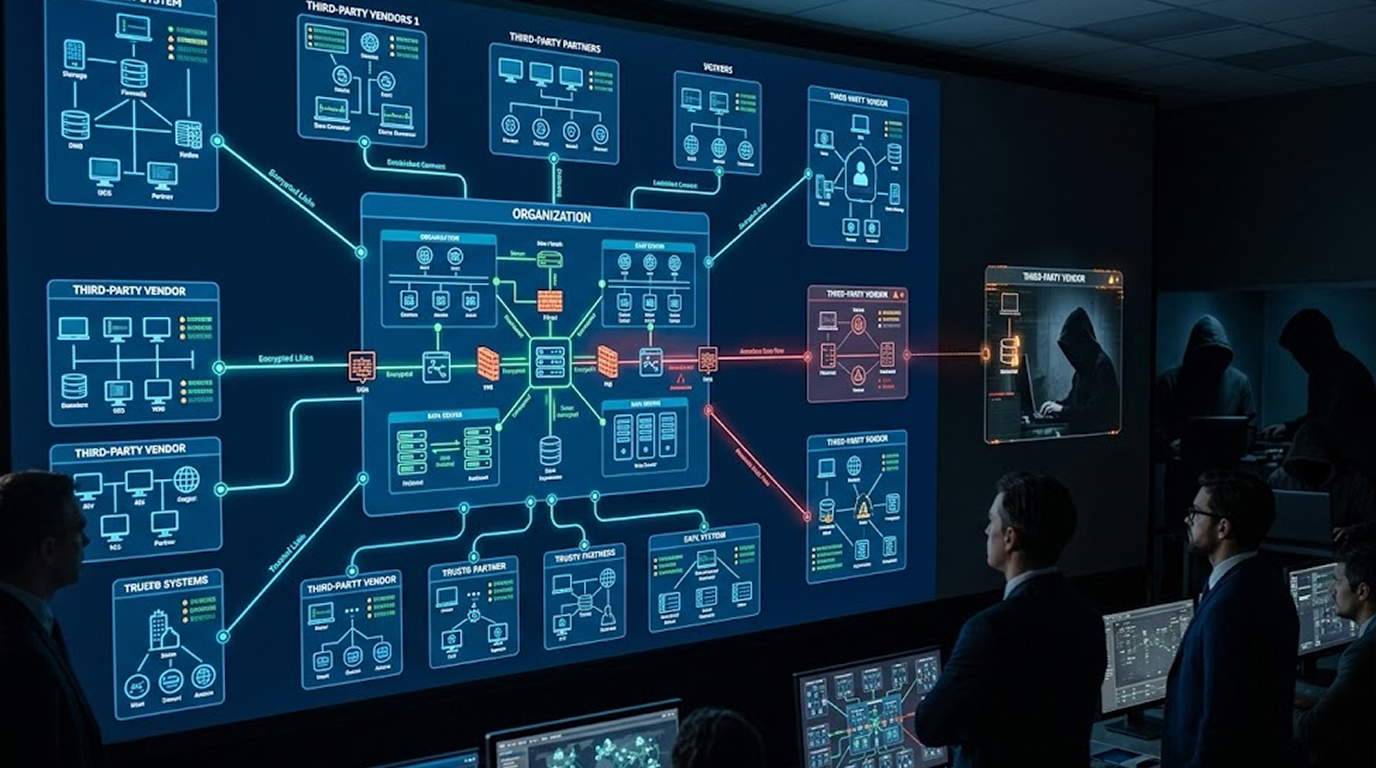
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067