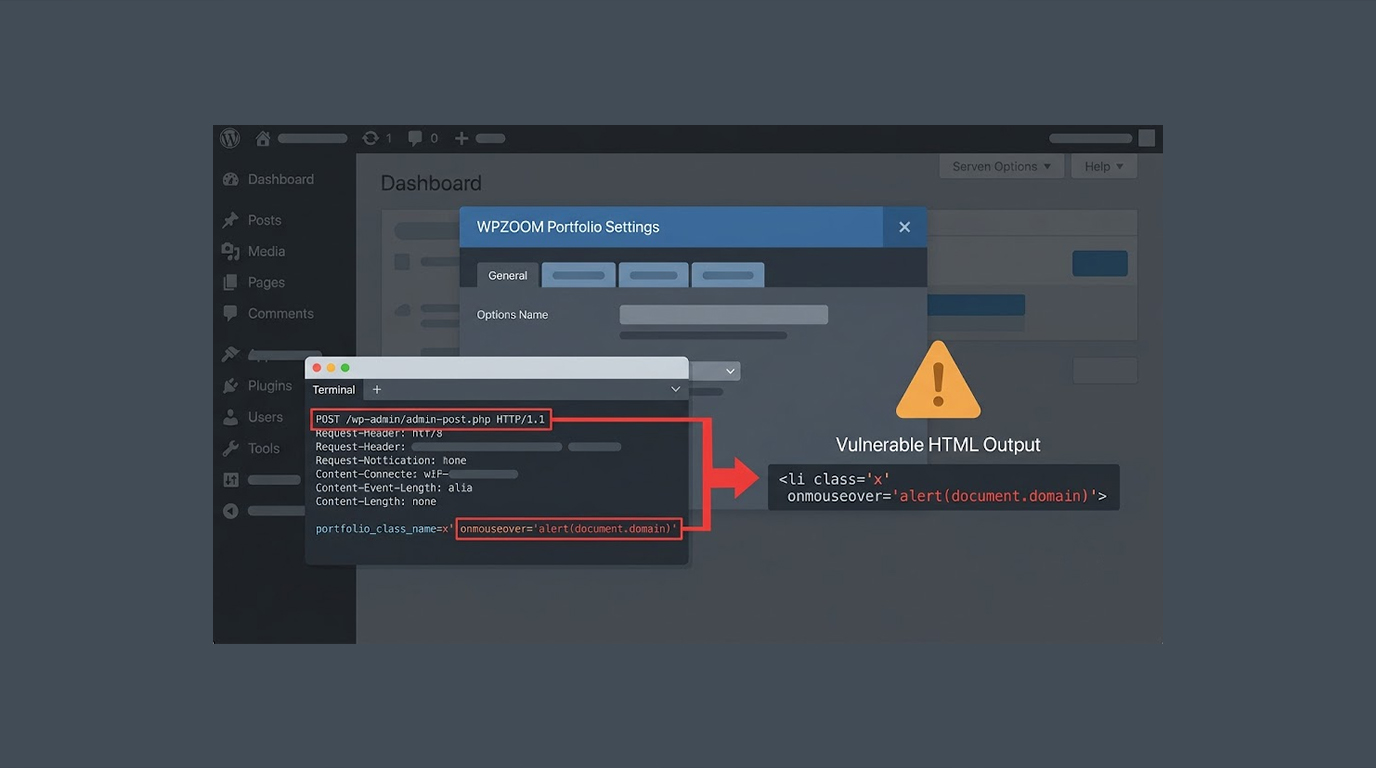
WPZOOM Portfolio XSS Vulnerability Allows Script Injection
A cross-site scripting (XSS) vulnerability exists within the WPZOOM Portfolio plug-in versions 1.4.21 or earlier. This vulnerability enables the att...
Found 4 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cross-site scripting (XSS) vulnerability exists within the WPZOOM Portfolio plug-in versions 1.4.21 or earlier. This vulnerability enables the att...
Immediate action is necessary if you use the Gravity SMTP plugin for sending emails through WordPress, as there is currently a vulnerability being exploite...
A serious authorization flaw has been discovered by security researchers in Chained Quiz WordPress plugin that allows attackers to change others’ qui...
WordPress website owners are urged to act swiftly following the disclosure of two critical vulnerabilities in widely used plugins: Really Simple Security a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067