A serious authorization flaw has been discovered by security researchers in Chained Quiz WordPress plugin that allows attackers to change others’ quiz attempts without authentication. This issue, which has been assigned CNIE-2025-10493, affects all previous versions of Chained Quiz prior to version 1.3.3; it is caused by the incorrect storing of a quiz attempt identification number in client-side cookies.
How the vulnerability works
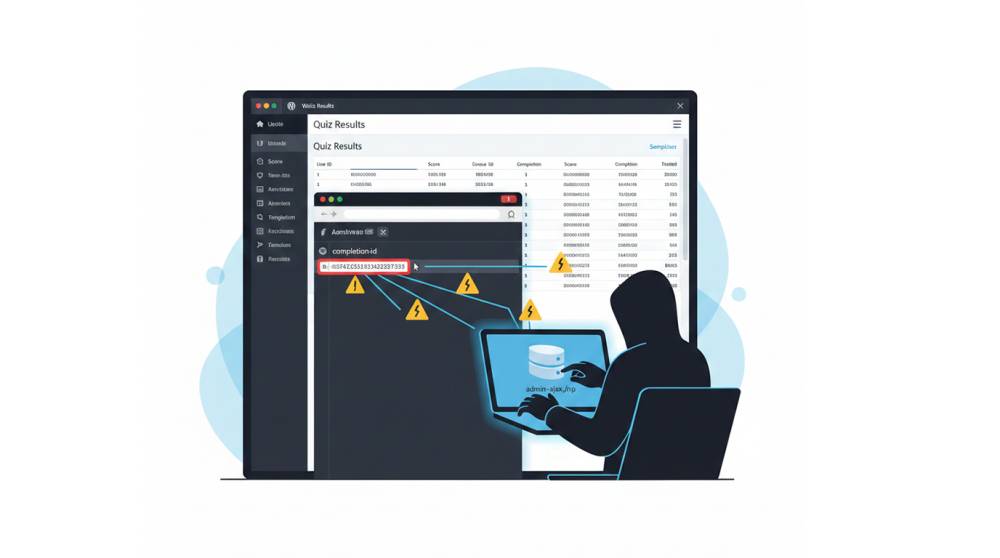
When a user finishes taking a quiz, the plugin generates an ID called a completion_id for that particular attempt. After this ID is generated, it is then written into a browser cookie following this format:
chained_completion_id<quiz_id>
The cookie value is the only way for the plugin to determine which attempt to update when submitting answers to a quiz. Additionally, there is no way for the server to confirm that the completion_id corresponds to the submitting user or whether that user is actually logged in.
Since these completion_ids are sequential integers and predictable, attackers can generate a valid completion_id by using brute-force methods.
Impersonating someone else with an exploited version of the program:
1. After anyone completes their own quiz and is able to see how submitted answers are processed,
2. They can capture a copy of their submitted answer(s) via admin-ajax.php,
3. Alter the cookie (or chained_completion_id) referenced by their answer submission to indicate that it belonged to another user,
4. Re-submit the altered answer(s)/score back to the server.
As a result, the server will unconditionally accept the altered answer(s) and update the user's score from the unmodified record without performing any authentication checks or session validation. As such, there is no ownership validation as well. Under the default settings of the plugin, authentication checks, ownership validations and session verifications will not be performed.
Significance of This Vulnerability
The attackers have the ability to:
1. Change the answers submitted by other users on their quizzes
2. Change the computed quiz scores and points
3. Change and corrupt the final results of the quiz created
4. To compromise all quizzes, assessments, rankings or certifications.
This vulnerability within any type of educational or compliance based training system affects the trustworthiness and accuracy of the systems as well as impacts downstream integrations reliant upon the completion of quizzes to determine learning standards and outcomes.
Component Impacted
Admin-ajax.php handles all quiz submissions and results.
Security Classification
CWE-639 - Authorization bypass via a User-controlled key
CWE-285 - Authorization violated.
Responsible Disclosure
Karuppiah Sabari Kumar (0xSabre) discovered and reported the issue. All users of this plugin should update once a patched version is released, or disable the plugin until a fix is available.
Source: Exploit DB