SignDrop: CLFS Exploit Claims SYSTEM Access
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Found 20 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
No zero-day. No malware-laced attachment. No exploit chain worth a conference talk. Microsoft just published an investigation into two intrusions where th...
Here we go again. Another week, another zero-day in Microsoft Defender. Security researcher Chaotic Eclipse just dropped a proof-of-concept exploit for a v...
A security researcher has released a proof-of-concept exploit for a new Microsoft zero-day called ShieldBreak. The vulnerability demonstrates a full patch...
Attackers broke into an organization's Oracle database through a SQL injection flaw in a public-facing web application. Then they installed a post-exploita...
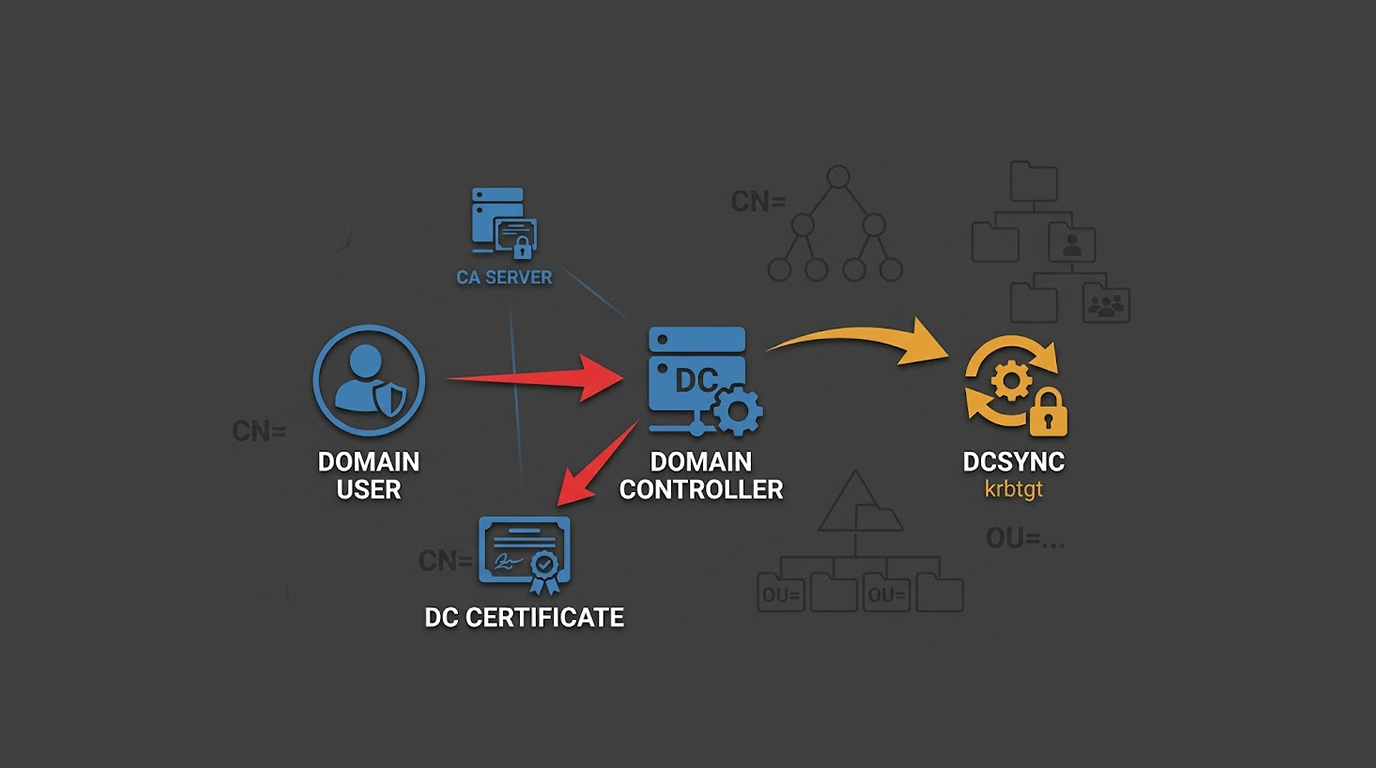
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
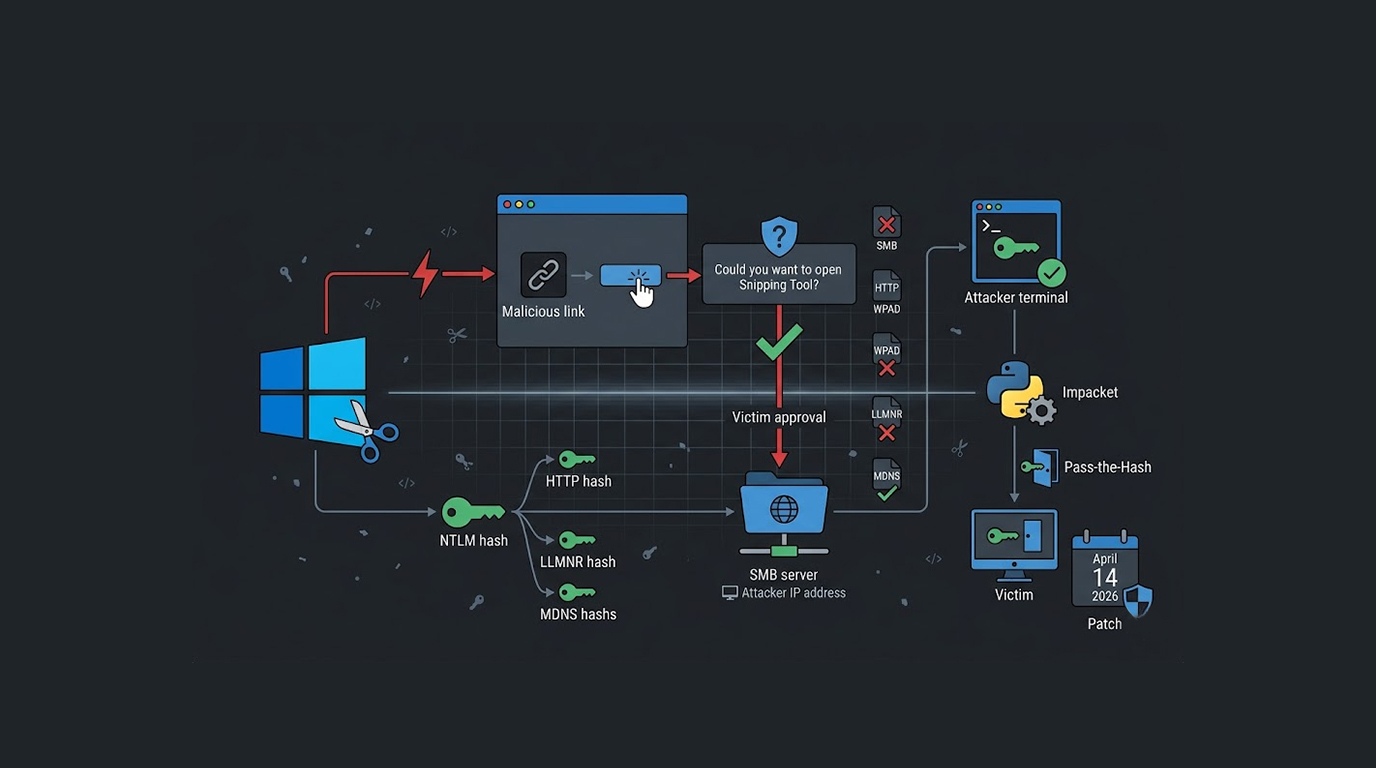
A single click on a malicious link, a quick approval of the "Open Snipping Tool" prompt, and your Windows password hash is on its way to an attacker. The...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067