Linux Kernel proc readdir Use After Free Leads to Root
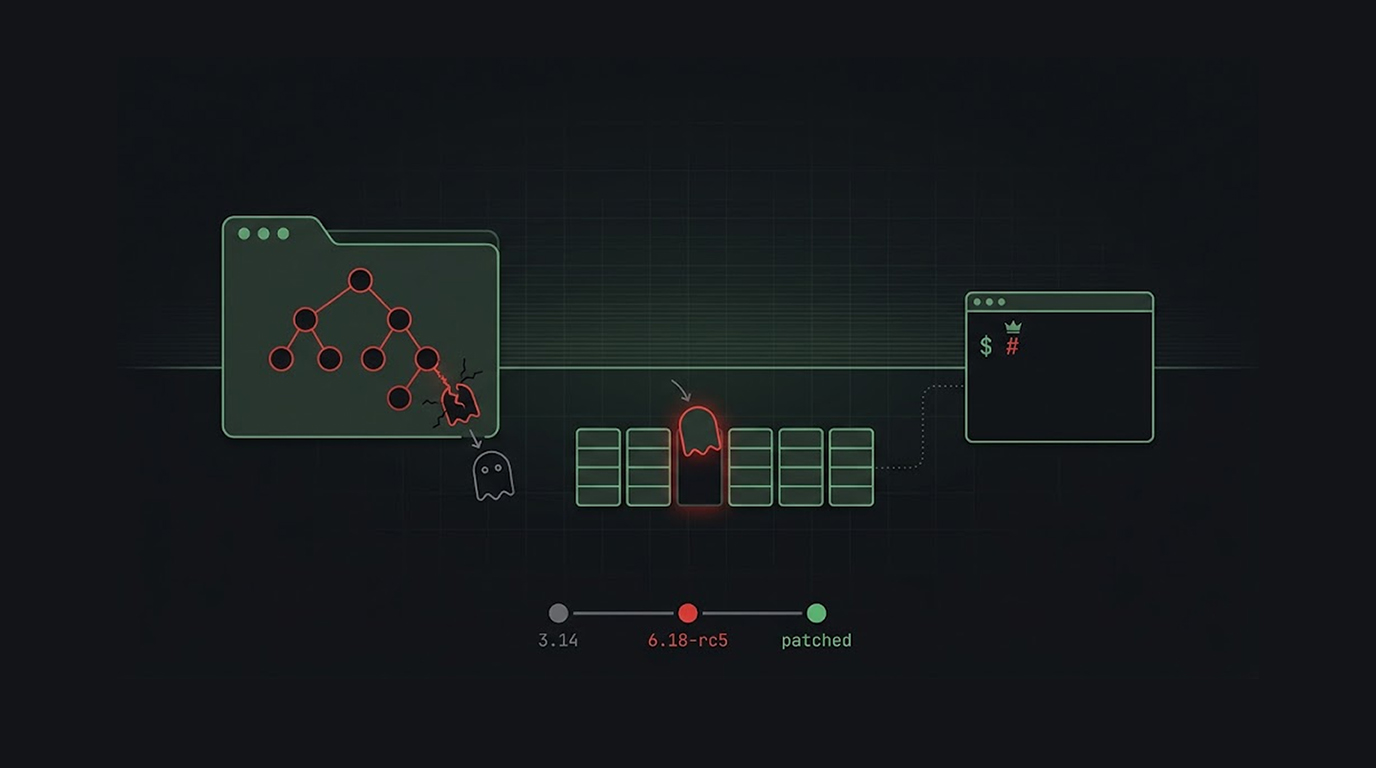
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
Found 141 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
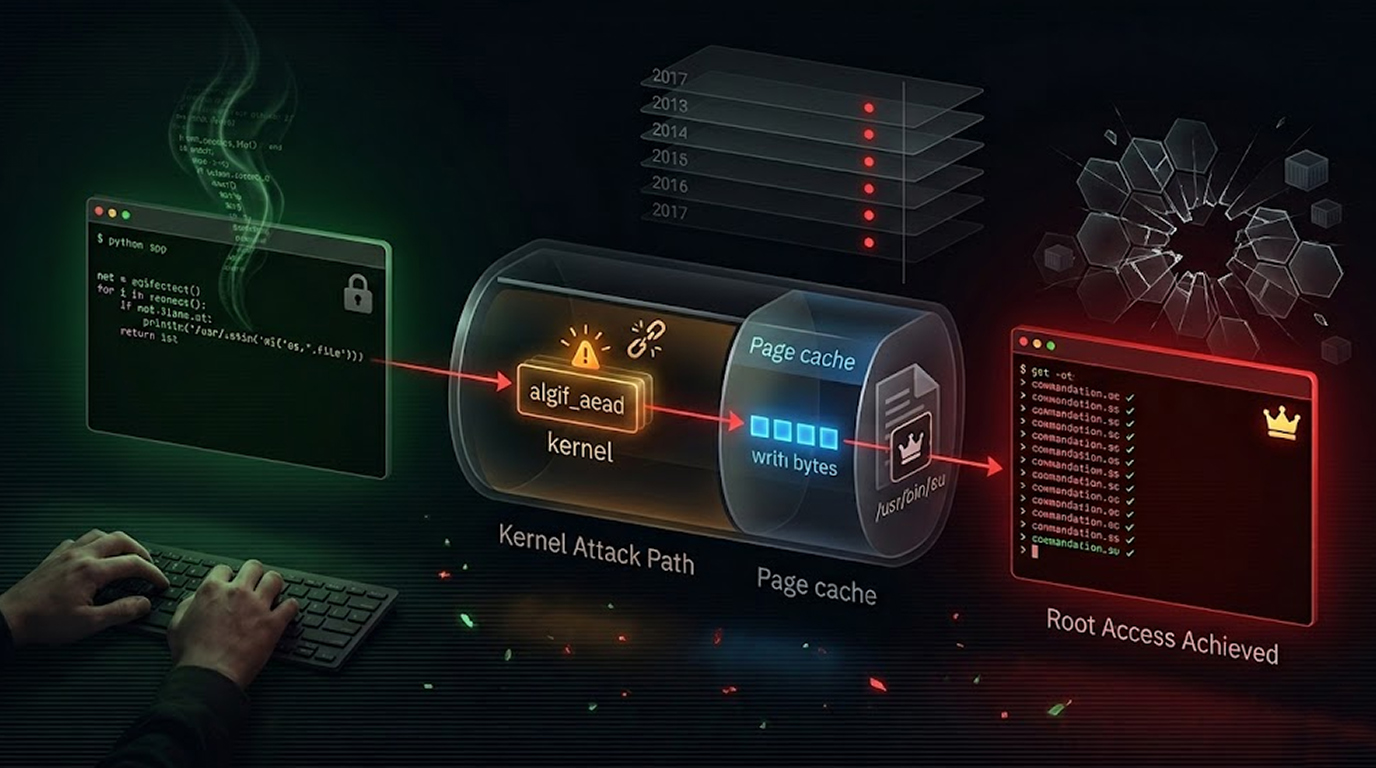
A single 732-byte Python script. Four controlled bytes. And root access on virtually every Linux machine shipped since 2017. That is the reality of Copy F...
A well-known privilege escalation vulnerability has been detected by a researcher in a long-used antivirus application. This flaw can allow any local user...
You imagine a hacker. Dark room. Glowing screens. Fingers flying across a keyboard. Exploits. Zero-days. Firewalls crumbling.That is Hollywood. The realit...
You run a vulnerability scan. You fix the critical findings. You feel safe.Then a real attacker breaks in through a phishing email your security team never...
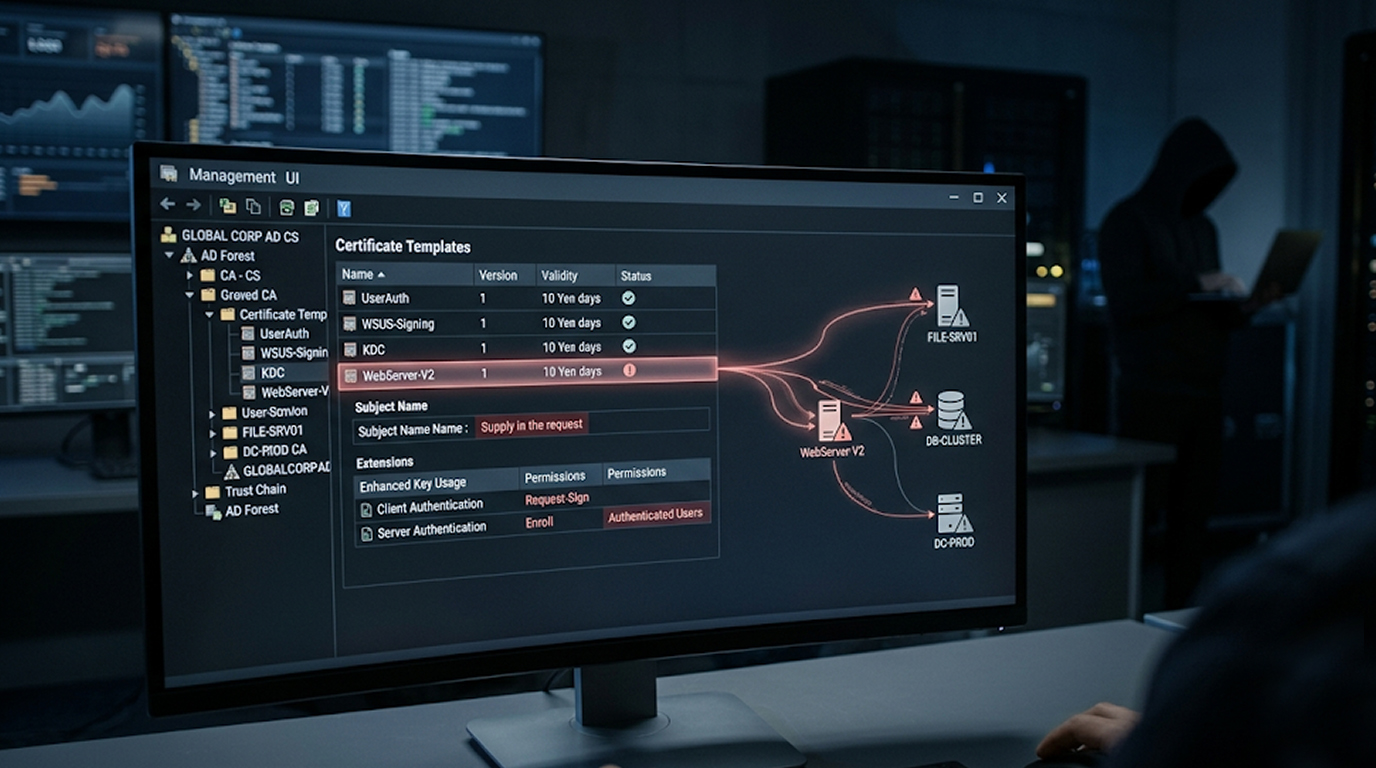
Active Directory Certificate Services (AD CS) is everywhere in enterprise Windows environments. And everywhere means opportunity.If you have done any inter...
A significant change in offensive security occurred in 2026 catalyzed by the use of AI-assisted exploit creation. There has been an evolution in how the ne...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067