100 Windows CMD Commands Every User Should Know (Complete 2026 Guide with Examples)
The Windows Command Prompt (CMD) is one of the most powerful tools built into every version of Windows — yet most users barely scratch the...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The Windows Command Prompt (CMD) is one of the most powerful tools built into every version of Windows — yet most users barely scratch the...
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
The U.S. Cybersecurity and Infrastructure Security Agency just added a new vulnerability to its Known Exploited Vulnerabilities catalog. Federal agencies n...
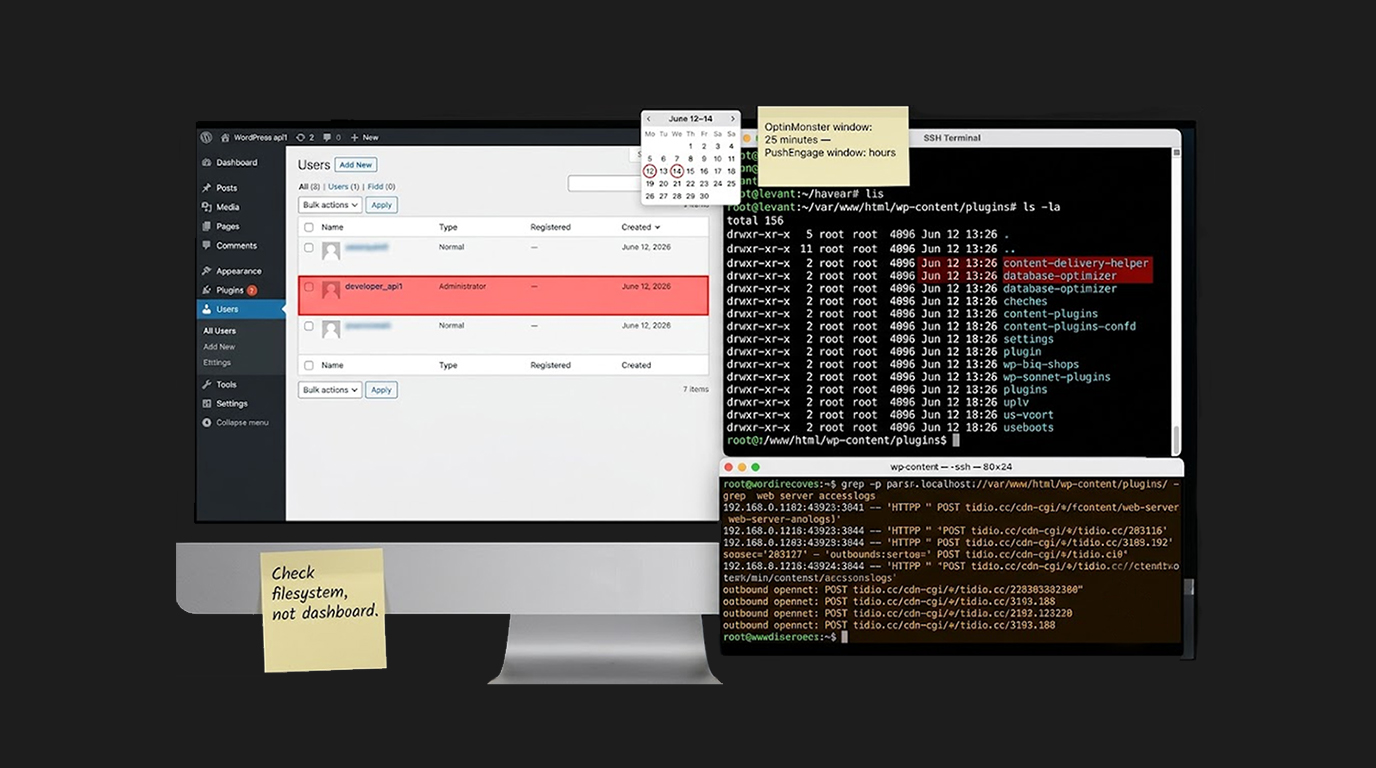
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
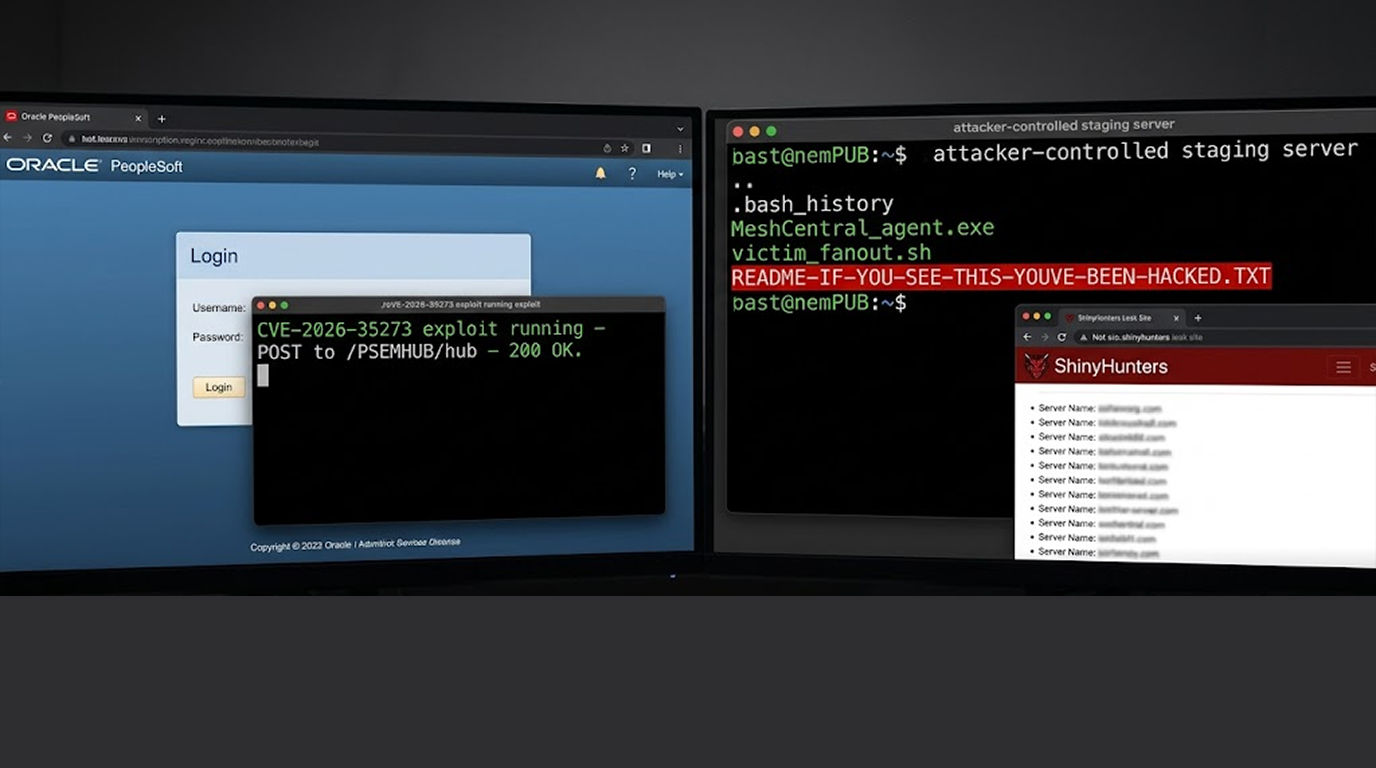
The ShinyHunters extortion crew pulled off something unusual. They exploited an unpatched vulnerability in Oracle PeopleSoft to break into enterprise syste...
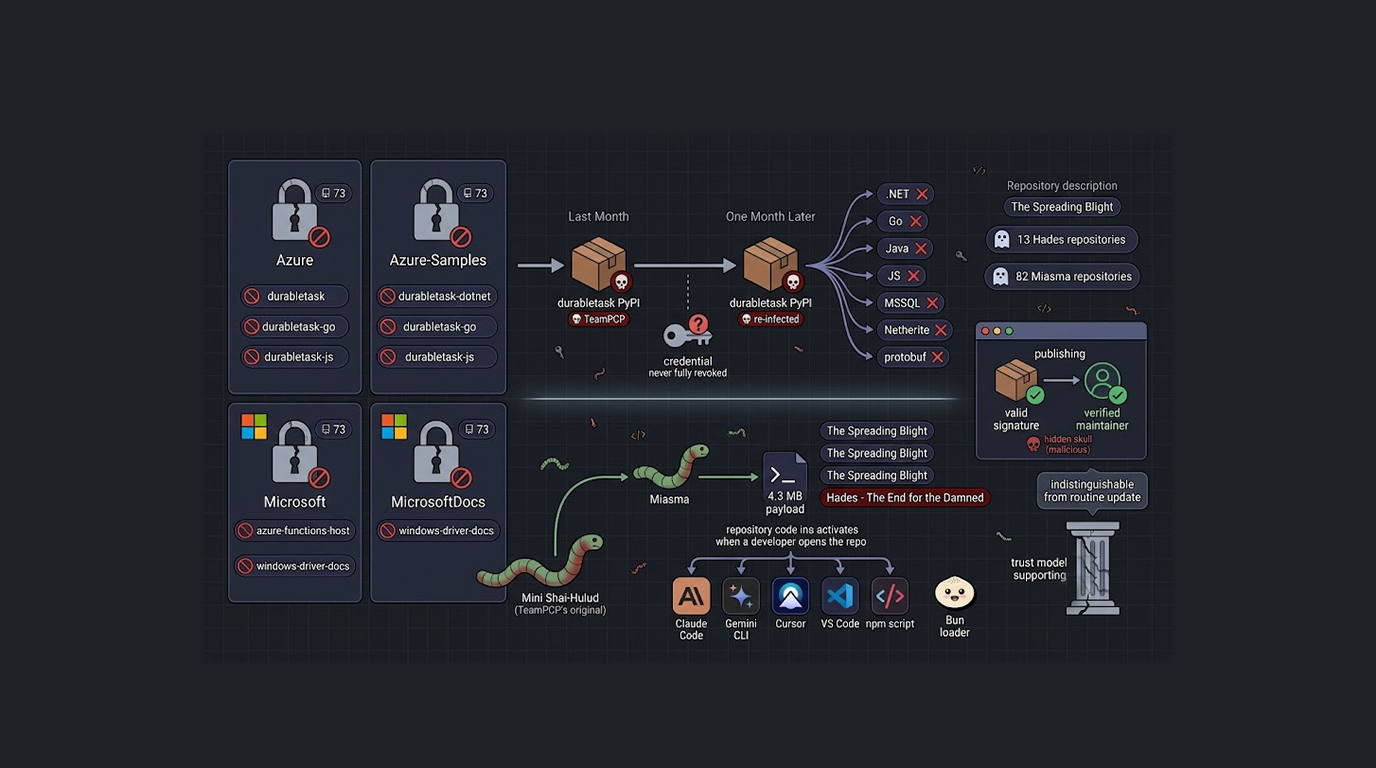
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067