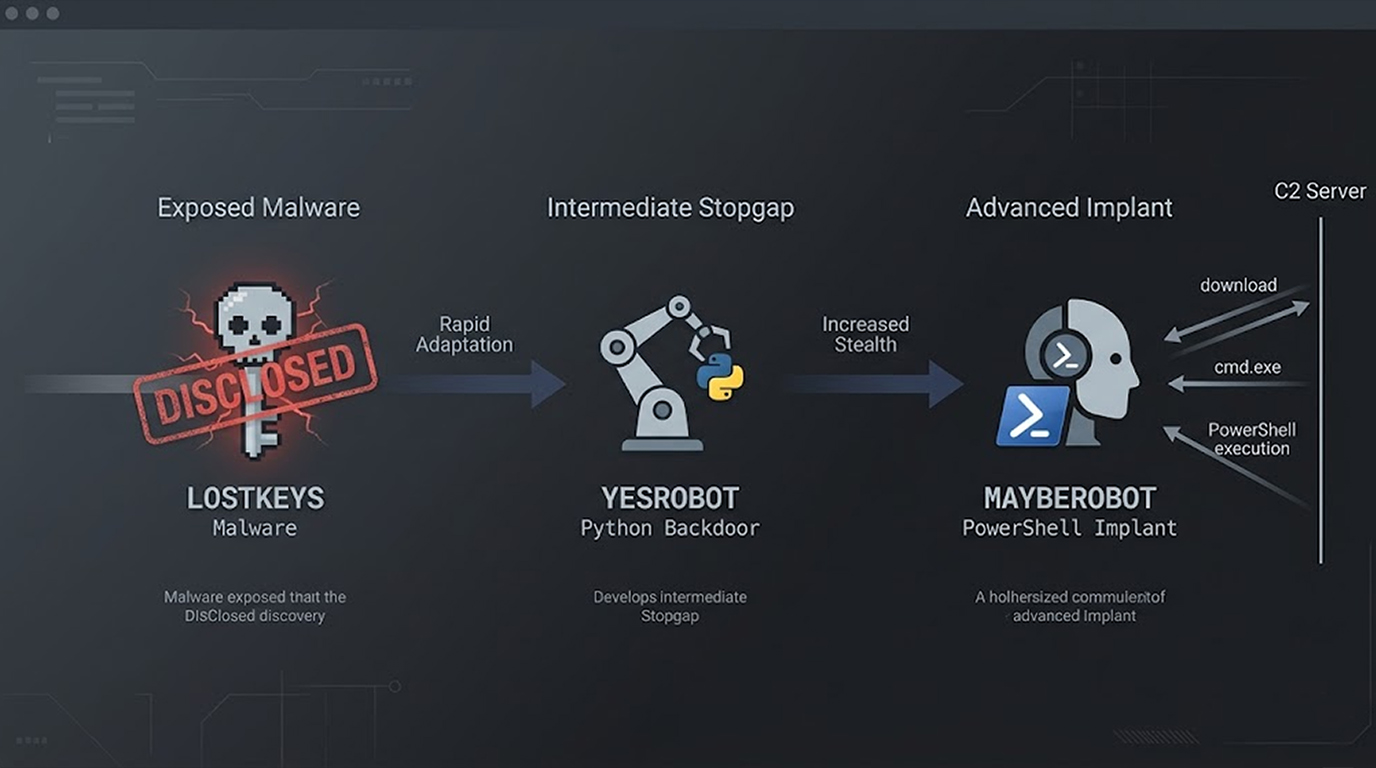
MAYBEROBOT: COLDRIVER’s Replacement for LostKeys
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
Found 108 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
During this tax season, Microsoft is alerting both individuals and companies about increased numbers of highly sophisticated phishing attacks that are aime...
Microsoft's threat teams have uncovered a slick credential-theft operation that's been running since mid-January 2026, where attackers trick people searchi...
In late 2024 / early 2025, the first-known publicly documented piece of Android malware to explicitly use generative AI in a production environment (as opp...
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
There's a new commercially available spyware platform for sale and advertised through Telegram called ZeroDayRAT. It comes with everything someone might ne...
In cyber security, string analysis refers to the process of retrieving human-readable text from a binary file, sample of malware or from network traffic an...
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067