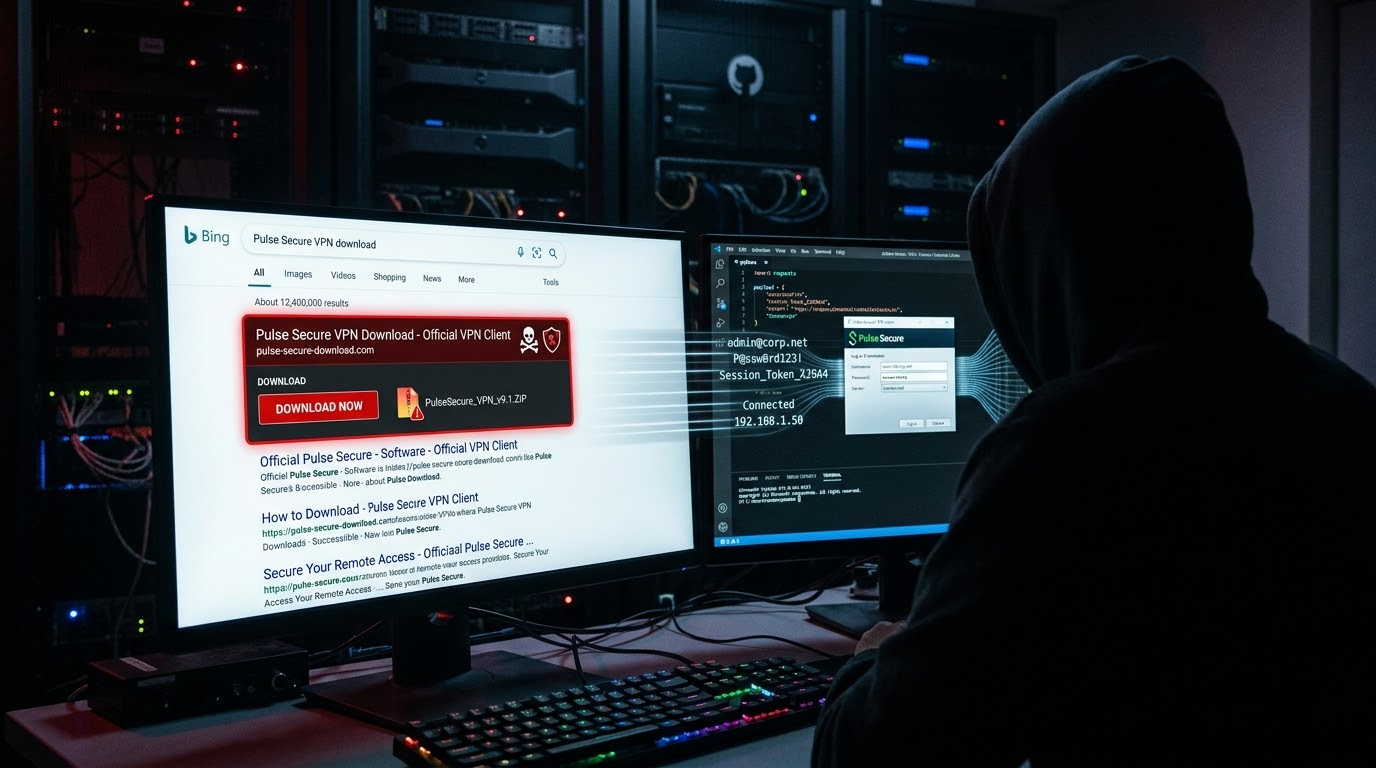
Storm-2561 Uses SEO Poisoning for Fake VPN Credential Theft
Microsoft's threat teams have uncovered a slick credential-theft operation that's been running since mid-January 2026, where attackers trick people searchi...
Found 173 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Microsoft's threat teams have uncovered a slick credential-theft operation that's been running since mid-January 2026, where attackers trick people searchi...
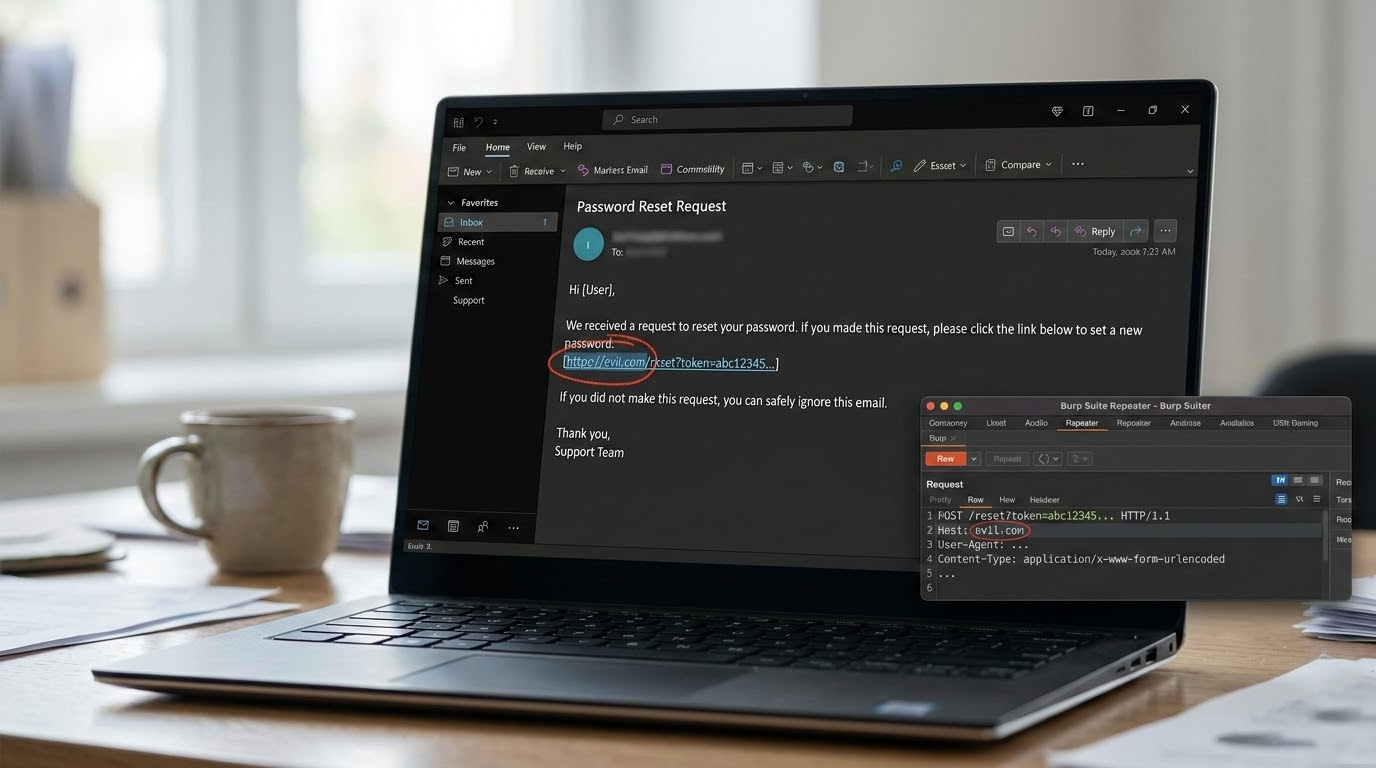
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
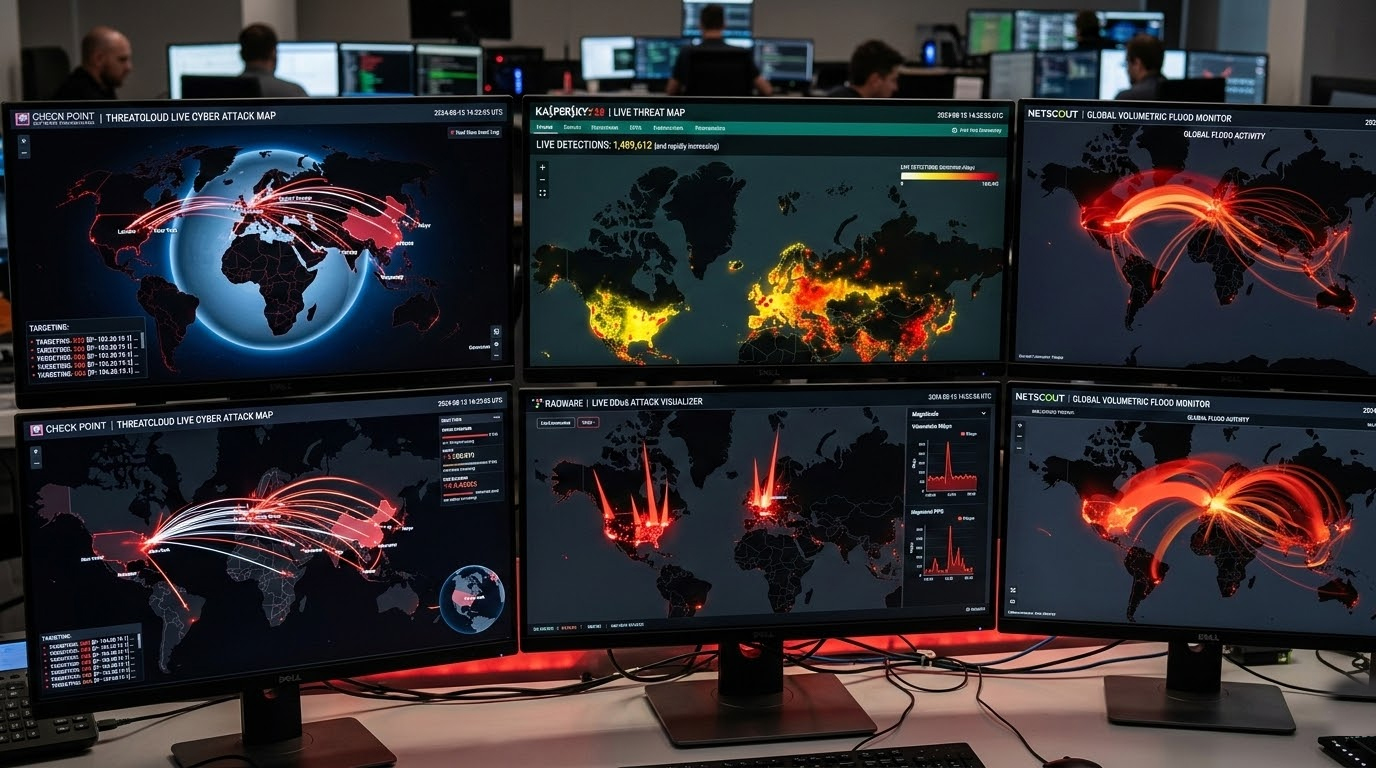
At this moment in March of 2026, hundreds of thousands of cyber attacks happen around the world every hour including instances of malware detection, phishi...
All three techniques are still responsible for a huge portion of account takeovers in 2026, but the balance has shifted noticeably over the last two years....
The message “Error 404: Page Not Found” is something we all see daily on websites. But when an entire business or critical parts of it suddenly...
4xx Status Codes indicate there is an issue with your request; in this case, there is an issue with what the client (Chrome/Safari/etc) is doing, rather th...
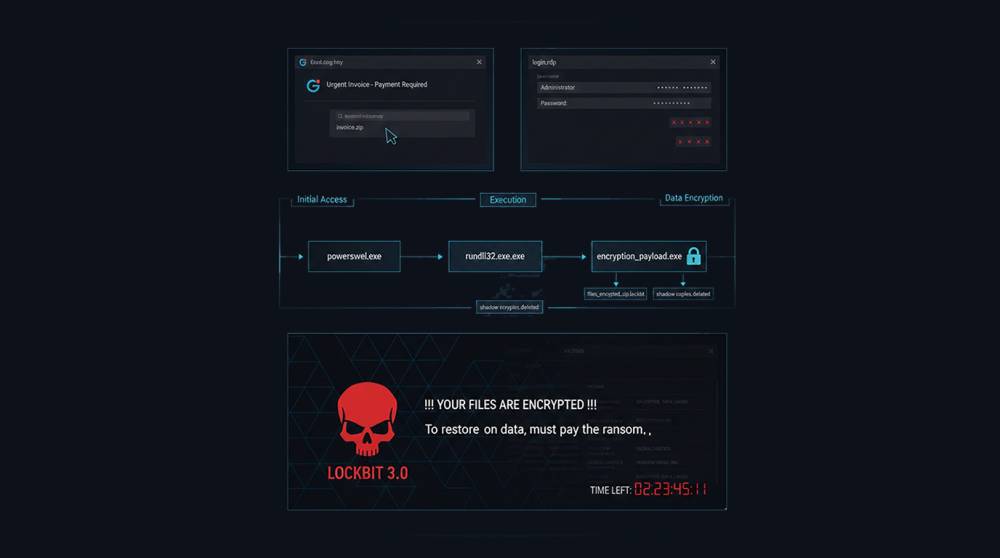
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
Kaspersky has shed light on a persistent phishing campaign tied to the threat actor Bloody Wolf (tracked by Kaspersky as Stan Ghouls), which has been quiet...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067