Cross‑Site Scripting (XSS) Explained Simply
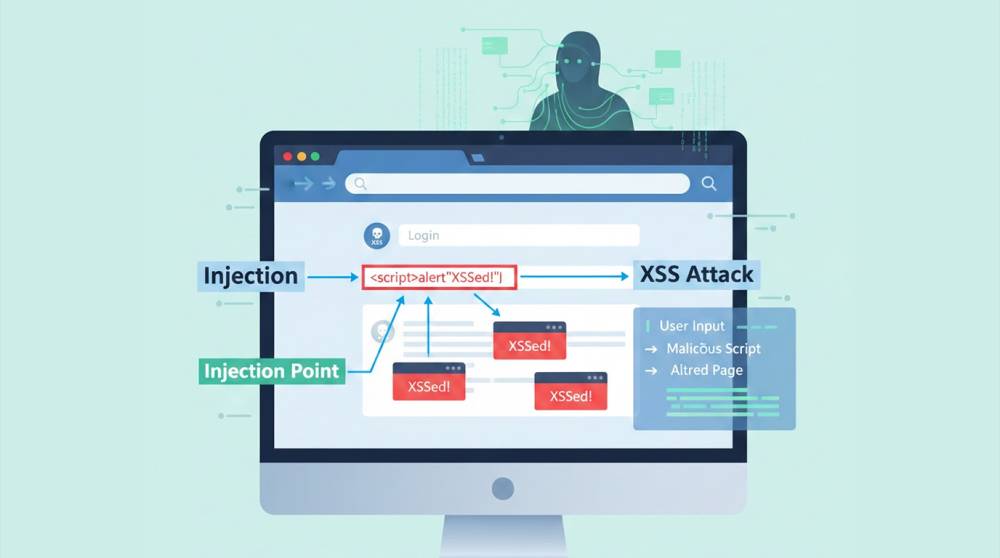
Cross Site Scripting, usually called XSS, happens when a website shows user input without properly checking it first.In simple terms:the website trusts dat...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cross Site Scripting, usually called XSS, happens when a website shows user input without properly checking it first.In simple terms:the website trusts dat...
Companies today rely heavily on web applications for conducting their business. From online banking sites to ecommerce stores, web applications serve three...
Palo Alto Networks has released security updates to fix a critical vulnerability in GlobalProtect Gateway and Portal that could lead to a denial-of-service...
Since October 2022, the Lumen Technologies threat intelligence group, Black Lotus Labs, has effectively taken down approximately 550 Command-and-Control (C...
XAMPP’s convenience makes it the easiest to recognize.The problems occur when:1. XAMPP is left running on web-accessible machines.2. There is an atte...
Most damage from a hack doesn’t happen instantly.It happens because people don’t realize what’s happening, or they freeze.The first 10 mi...
Researchers specializing in cybersecurity have discovered a new malware campaign known as SHADOW#REACTOR, in which a group of malware designers builds what...
The Cybersecurity and Infrastructure Security Agency (CISA) of the United States has now added the 'CVE-2025-8110' Path Traversal vulnerability in Gogs (a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067