What Is OpenVAS (Greenbone) and Why It Matters
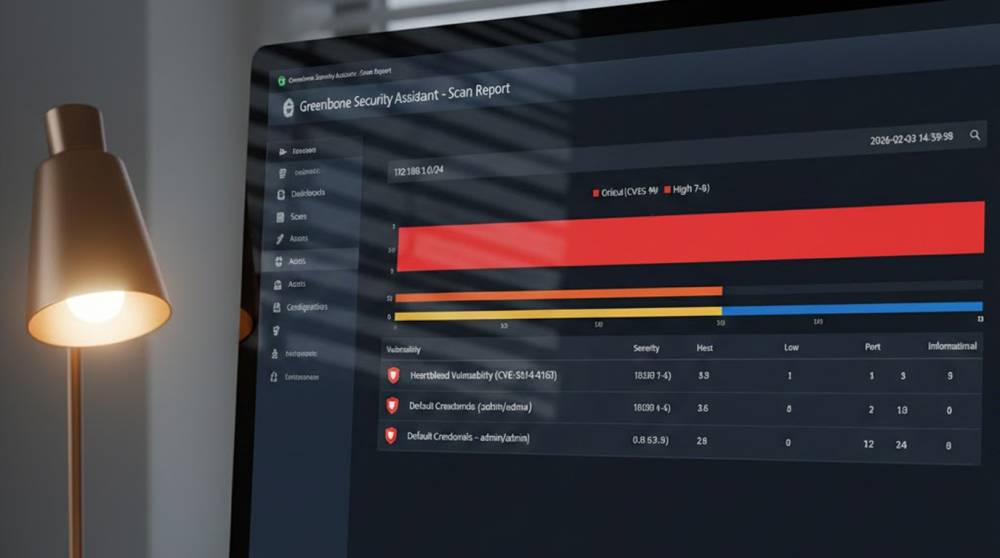
OpenVAS (Open Vulnerability Assessment System) is one of the most widely used free and open-source vulnerability scanners available today. It is the commu...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
OpenVAS (Open Vulnerability Assessment System) is one of the most widely used free and open-source vulnerability scanners available today. It is the commu...
According to Cybersecurity firm Socket, a sneaky supply chain compromise on the Open VSX Registry (the open-source alternative to Microsoft's VS Code exten...
The term "Garage APTs" (Advanced Persistent Threats/small teams) in cyber security defines entities that are small, but now can implement APT level operati...
In the midst of Iran's ongoing economic protests sparked late last year by skyrocketing inflation, food shortages, and a plunging currency a new cyber camp...
Commix (short for Command Injection eXploiter) is one of the most powerful open-source tools specifically built to automate detection and exploitation of O...
SQL injection (SQLi) is still among the top Web App Vulnerabilities due to both its high cost and long-standing existence over 20 years. SQLi continues to...
SmarterTools has resolved two high-priority security holes found in its SmarterMail program for sending and receiving emails (or just mailing), including o...
The following are 7 tools that are regularly used and regarded highly as a substitution for sqlmap or an additional tool to sqlmap during live pentesting,...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067