Vendor Got Hacked? Yes, Hackers Can Reach Your Data
You receive an email from a company you work with. Your payroll provider, your cloud storage vendor, your marketing agency, your IT support company. "We h...
Found 109 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You receive an email from a company you work with. Your payroll provider, your cloud storage vendor, your marketing agency, your IT support company. "We h...
The Vietnam-aligned threat actor known as OceanLotus has spent more than a decade targeting foreign entities, especially China. But something changed recen...
The cyber threat landscape does not stand still. Neither can your defenses.Every year brings new ways to attack, new technologies to exploit and new risks....
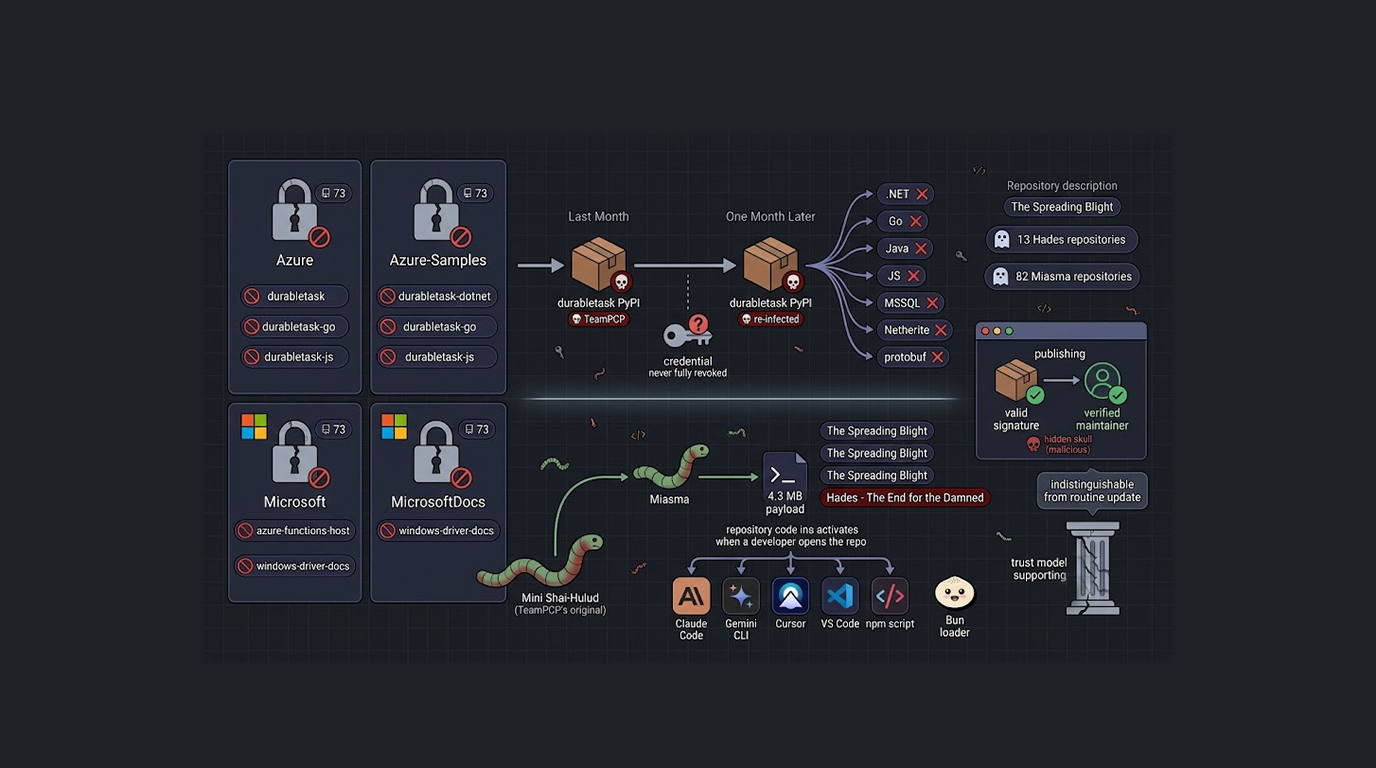
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
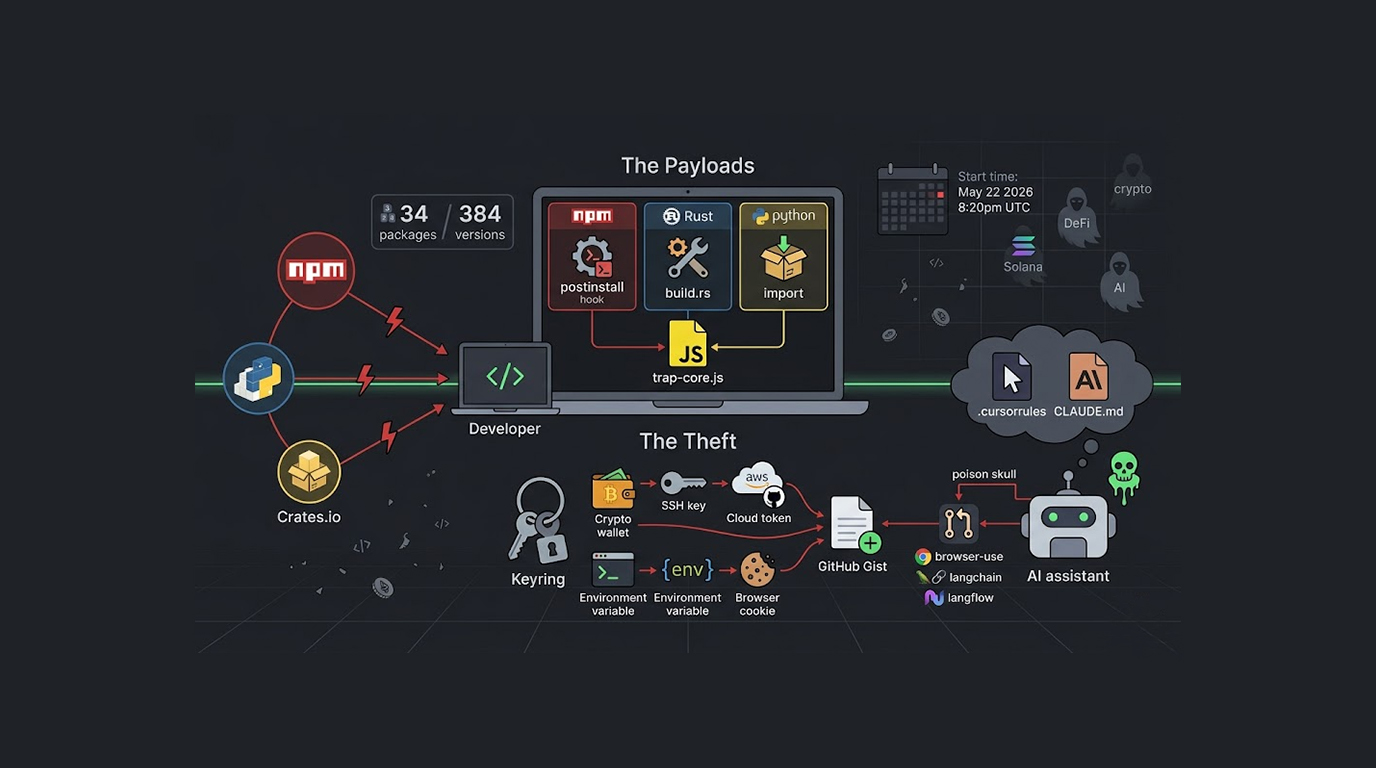
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
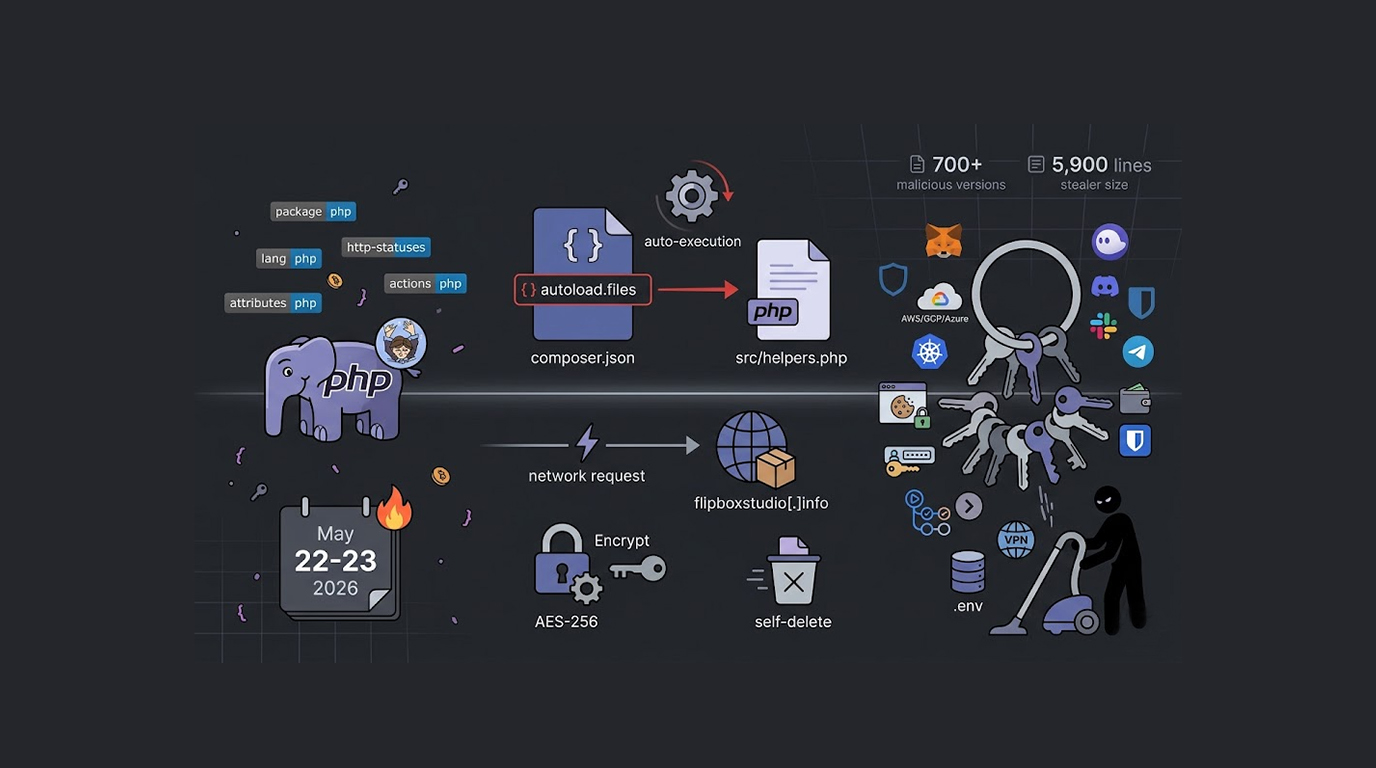
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
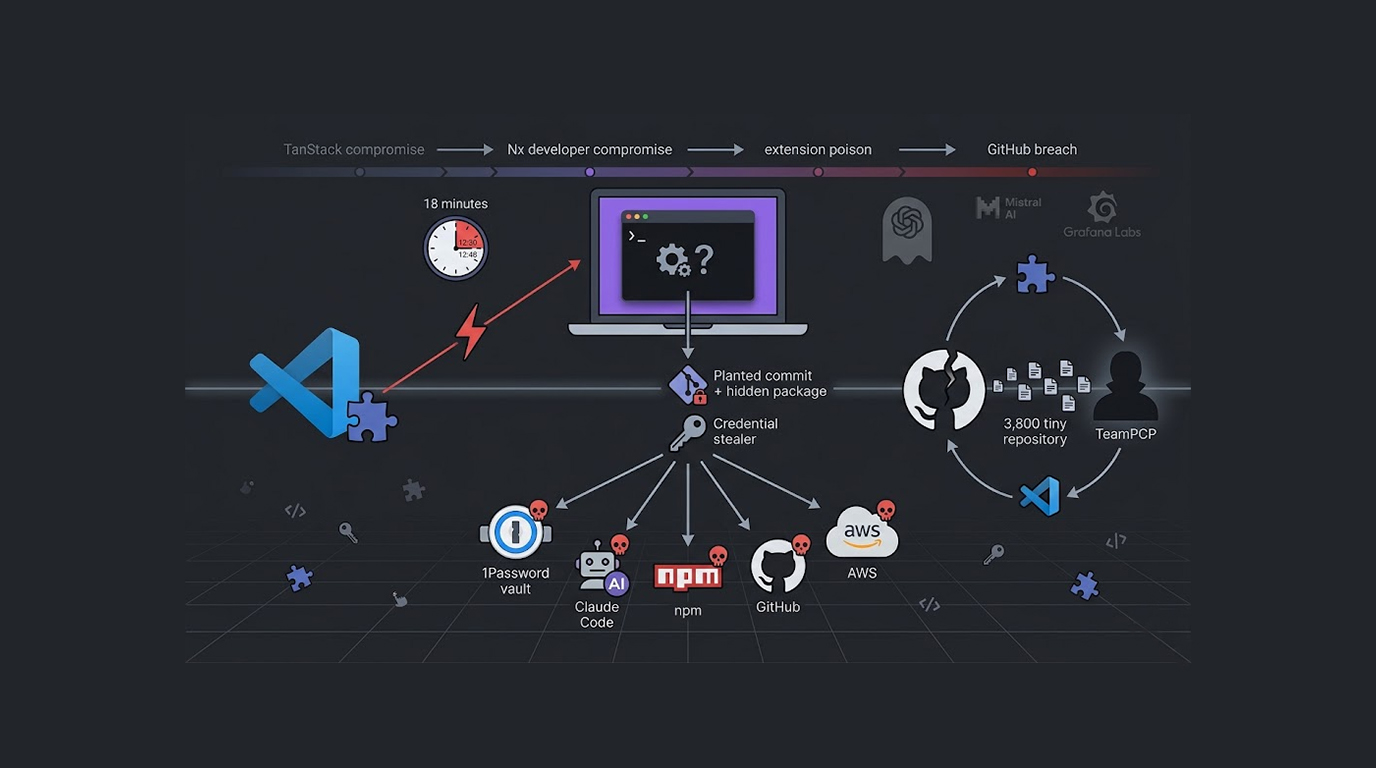
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
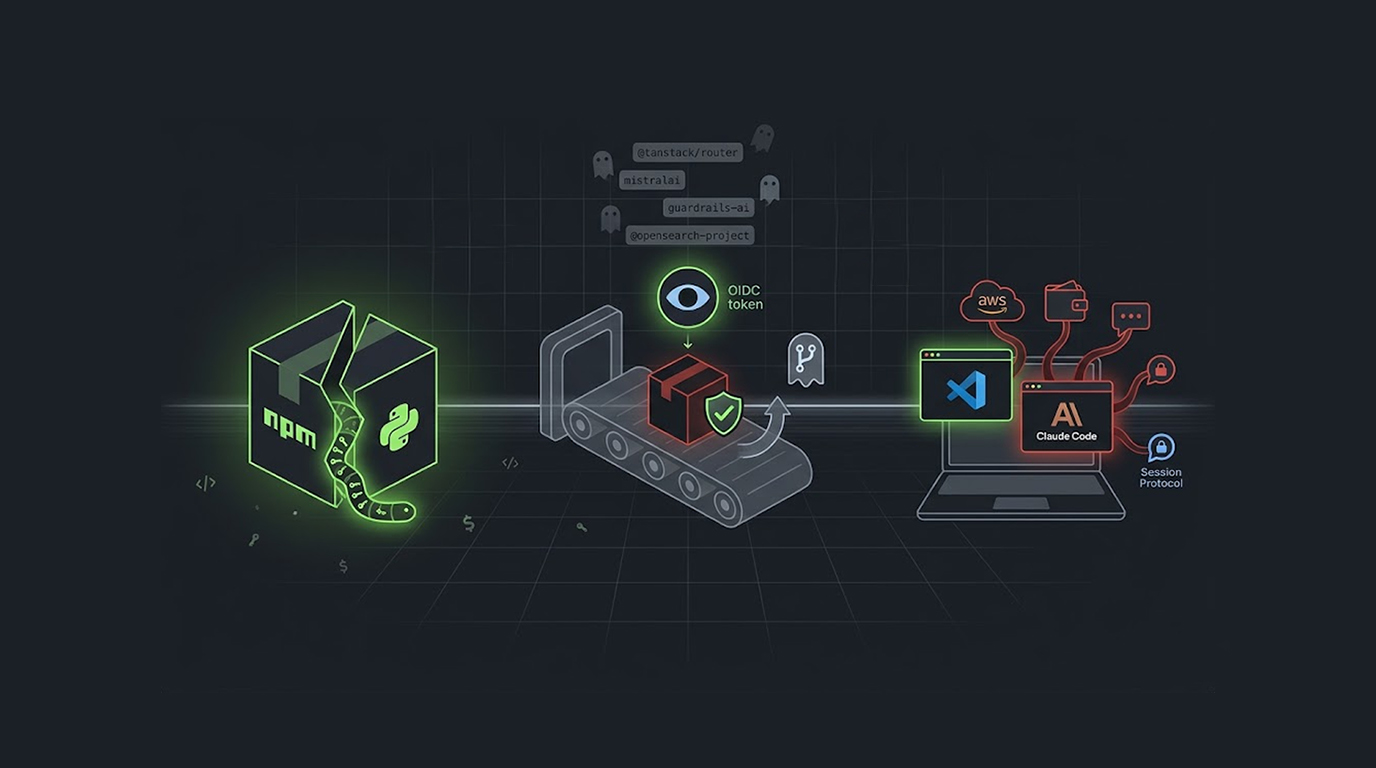
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067