Miasma Supply Chain Attack Hits 73 Microsoft GitHub Repos
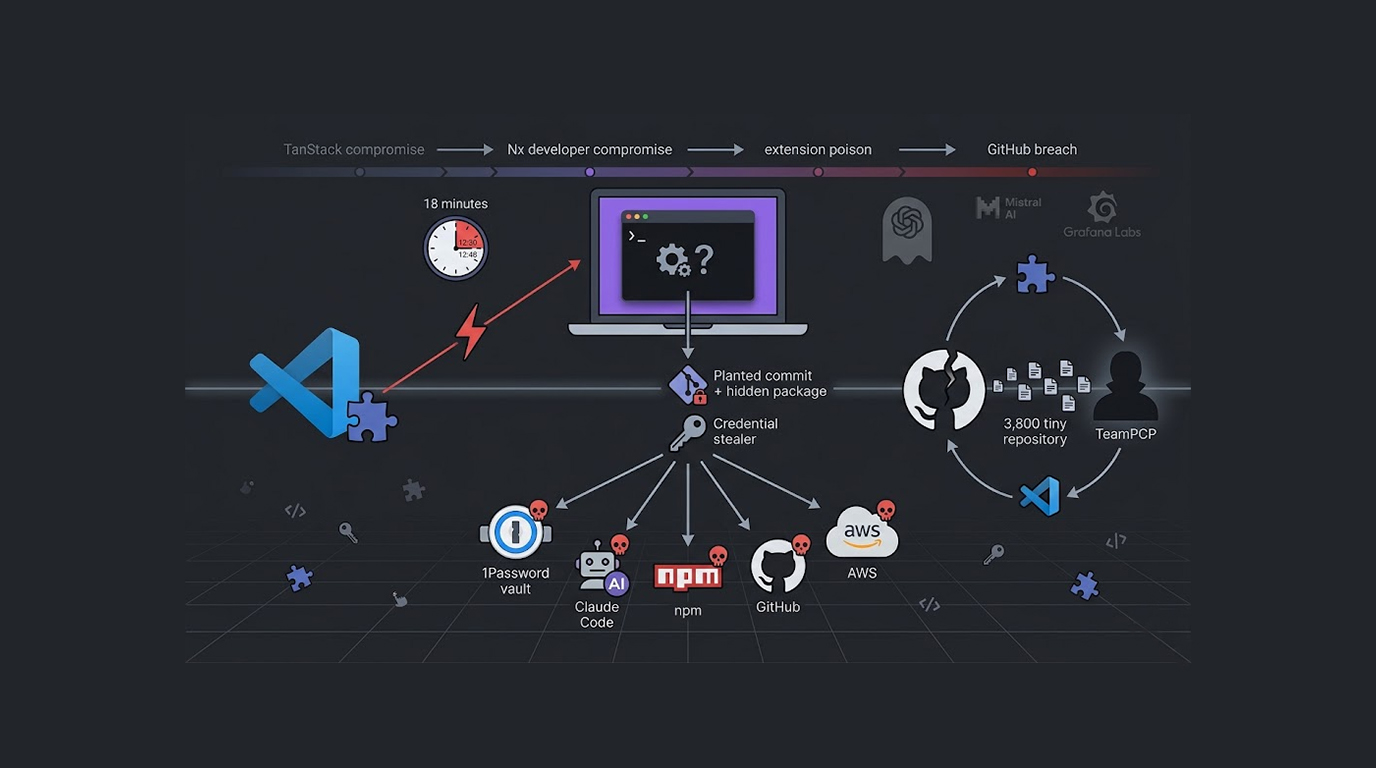
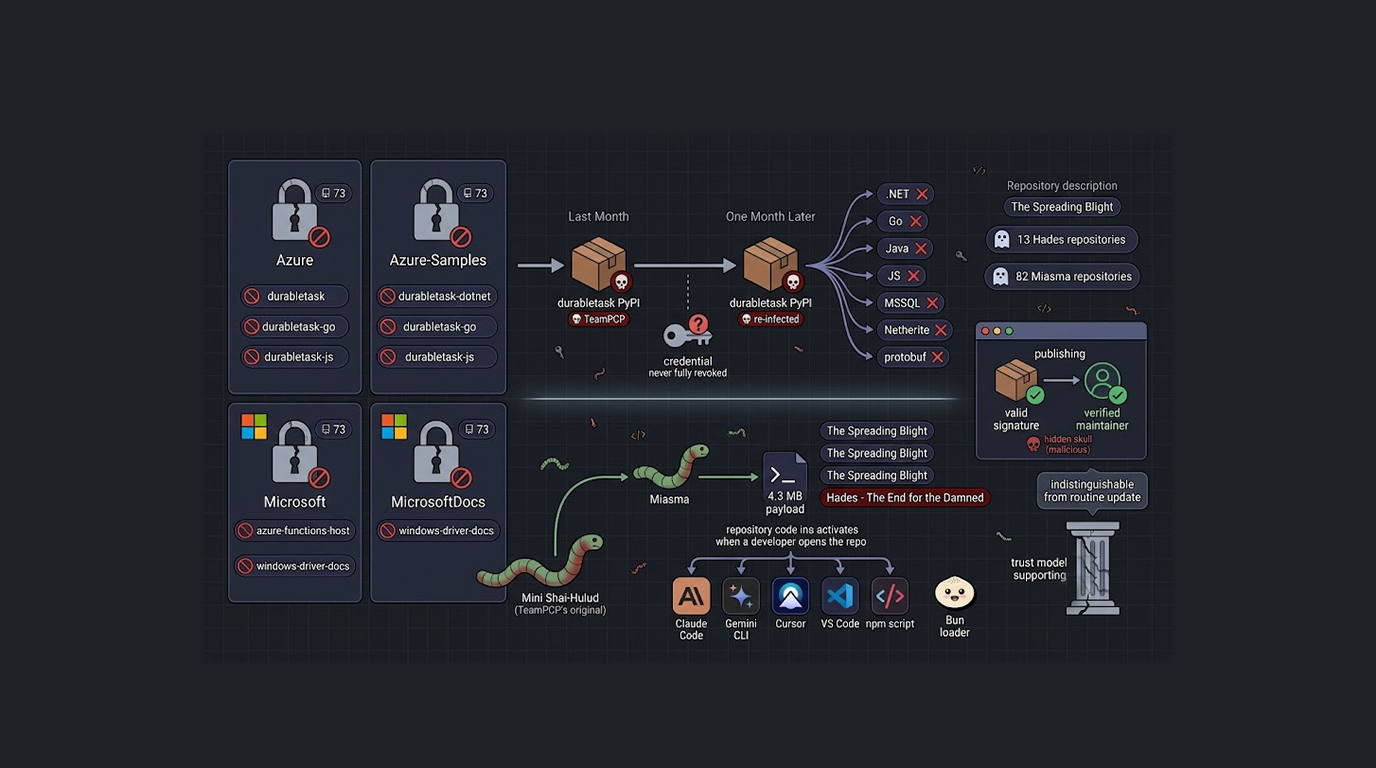
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
Found 61 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
A newly discovered denial-of-service exploit affects major web servers including NGINX, Apache HTTPD, Microsoft IIS, Envoy, and Cloudflare Pingora, and the...
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
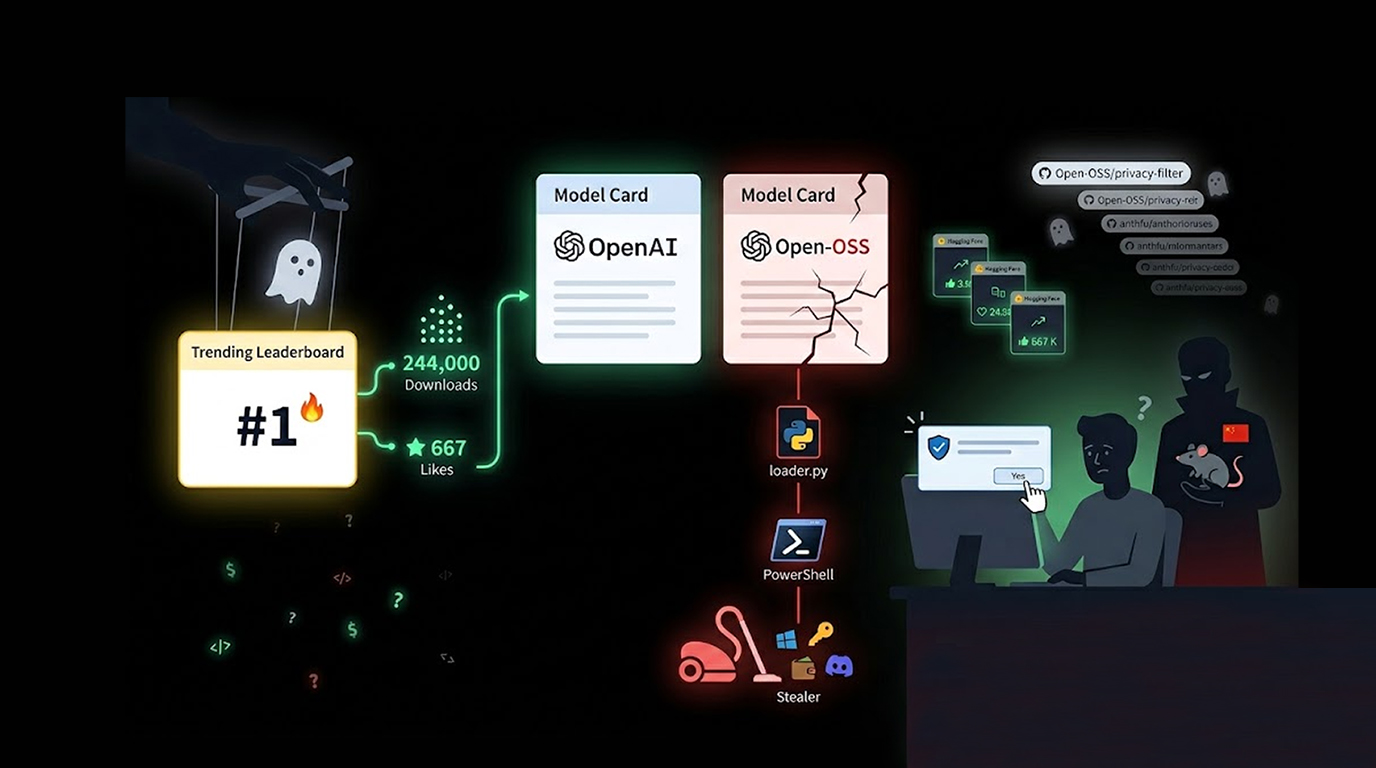
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
In the first half of 2026 a new class of malware started appearing in underground forums and private Telegram channels under names like “PromptReaper”, “LL...
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Anthropic just dropped Claude Opus 4.6, its latest frontier model, and it's already making waves, not just for sharper coding and longer agentic runs, but...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067