The Blurring Line Between Cybercrime, Espionage & Warfare
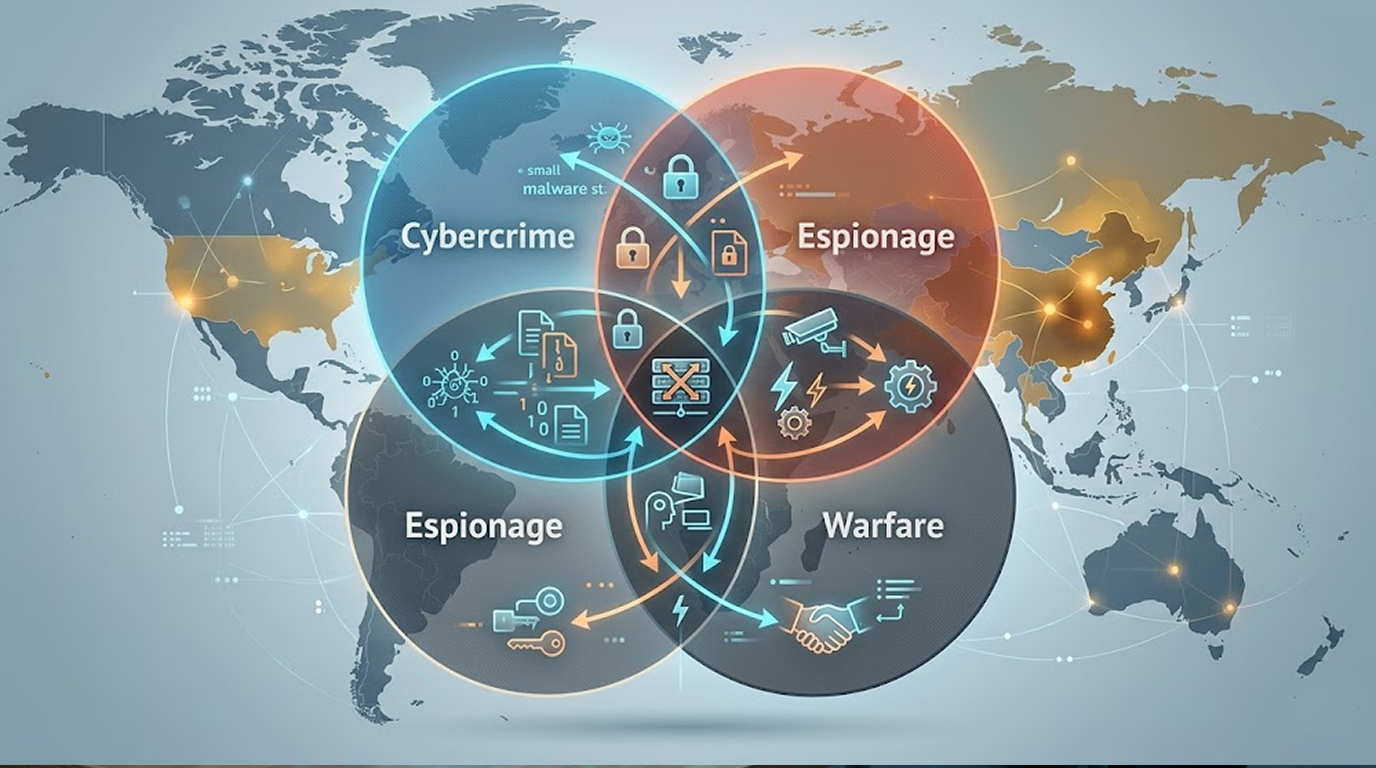
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
Found 76 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
Poisoning of mail logs is an obscure variation of log poisoning that is no less effective than web access log poisoning. However, in this case, the malicio...
Banner grabbing is one of the oldest tricks in reconnaissance, and in 2026 it remains ridiculously effective, especially on internet-facing servers. You li...
According to a joint report by the Google Mandiant and Google Threat Intelligence Group, a suspected China-related threat cluster identified as "UNC6201" h...
Today, attackers have transitioned from using traditional fixed payloads in cyber campaigns (ransomware attacks, espionage, infostealer operations, and phi...
Ivanti disclosed and patched two high-severity (CVSS 9.8) code injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) affecting Ivanti Endpoint Manage...
File upload vulnerabilities (CWE-434) let attackers drop webshells, small scripts that provide remote command execution, file management, and persistence o...
Google Dorking (also called Google Hacking) is the technique of using advanced search operators in Google (and sometimes Bing or other engines) to find pub...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067