Linux Kernel OVSwrap Vulnerability Gives Local Users Root
A memory corruption flaw in the Linux kernel's Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured distrib...
Found 141 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A memory corruption flaw in the Linux kernel's Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured distrib...
cPanel has released a targeted security update addressing a vulnerability that could let an authenticated hosting customer execute SQL in the database's ro...
Adobe has released security updates for a maximum-severity vulnerability in Campaign Classic, its enterprise marketing automation platform. The flaw could...
You have spent months training an AI model. Thousands of GPU hours. Hundreds of thousands of pounds in compute costs. Your team has fine-tuned it, validate...
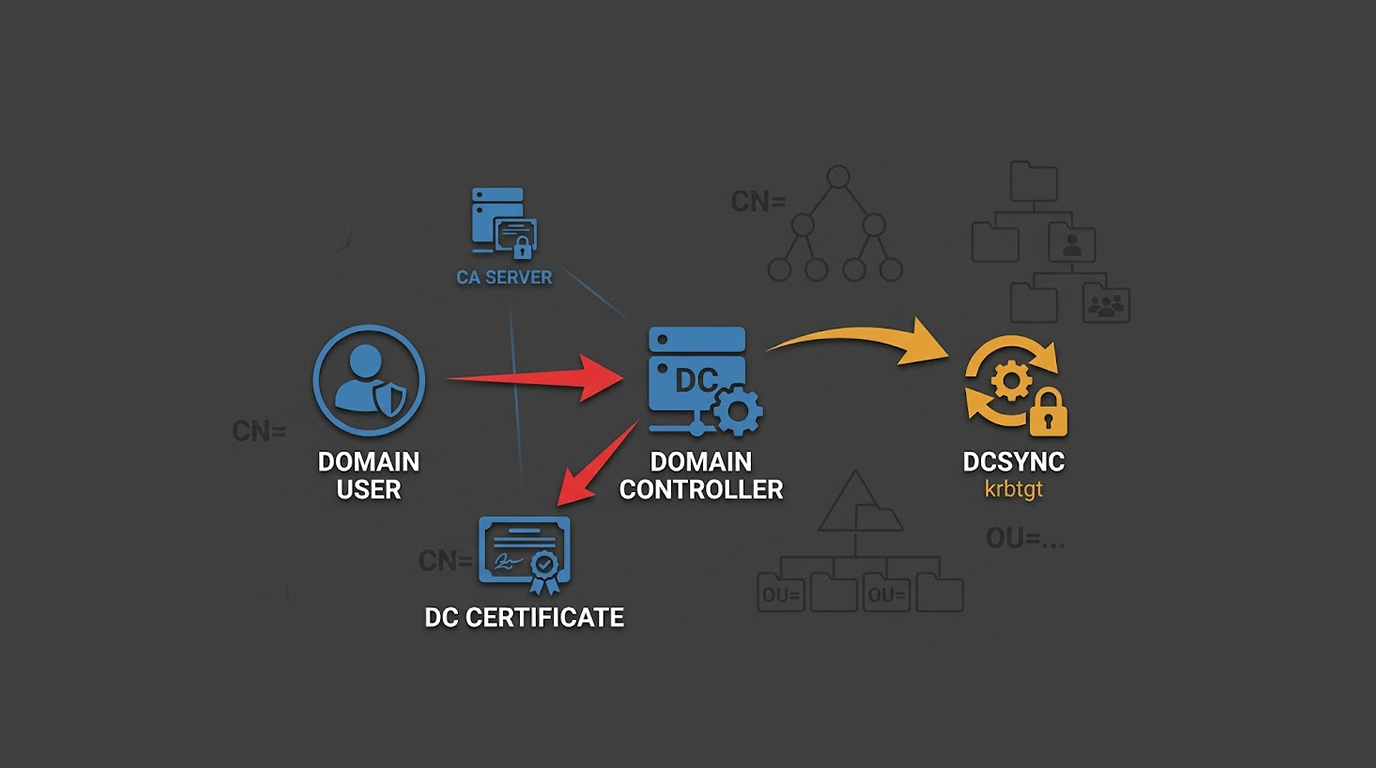
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
Traditional antivirus looks for known signatures. It has a list of bad files and checks every file against that list. If the malware is new, the antivirus...
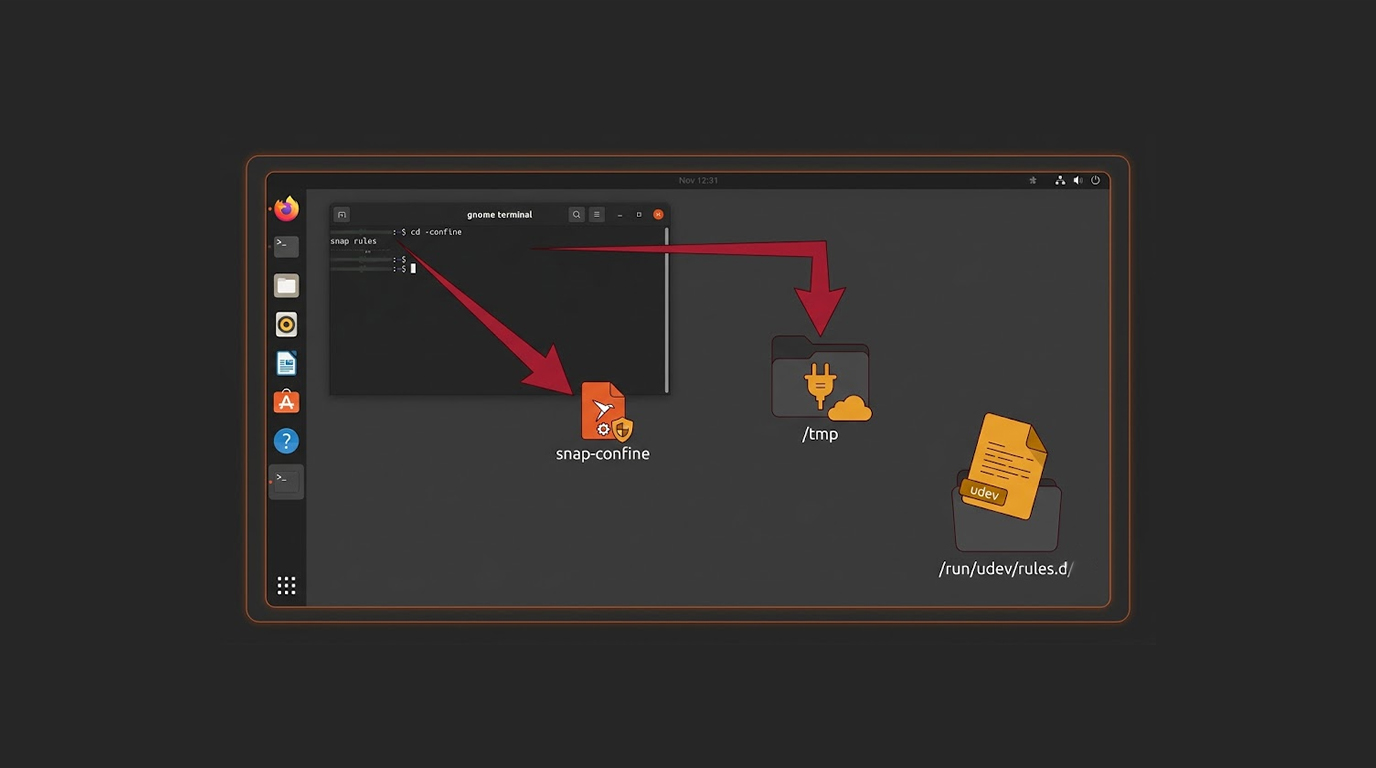
There is a local privilege escalation vulnerability in the snap-confine which lets an unprivileged user gain root permissions and full control over a targe...
You have a network. You have firewalls, intrusion detection, and endpoint protection. You have done everything right. But the attackers are still probing....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067