BlackByte Ransomware Group Exploits VMware ESXi Flaw and Vulnerable Drivers
The BlackByte ransomware group has been observed exploiting a recently patched authentication bypass vulnerability in VMware ESXi, tracked as CVE-2024-3708...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The BlackByte ransomware group has been observed exploiting a recently patched authentication bypass vulnerability in VMware ESXi, tracked as CVE-2024-3708...
In an era where digital technology evolves at lightning speed, deepfake technology stands out as both a marvel and a menace. Deepfakes are sophisticated di...
Cybersecurity researchers have discovered a new type of dropper that acts as a conduit for launching next-stage malware, with the primary aim of infecting...
In what's a case of an operational security (OPSEC) lapse, the operator behind a new information stealer called Styx Stealer leaked data from their own com...
Cybersecurity researchers have shed light on a sophisticated information stealer campaign that impersonates legitimate brands to distribute malware like&nb...
Cybersecurity researchers have discovered two security flaws in Microsoft's Azure Health Bot Service that, if exploited, could permit a malicious actor to...
Microsoft on Tuesday shipped fixes to address a total of 90 security flaws, including 10 zero-days, of which six have come under active exploitation i...
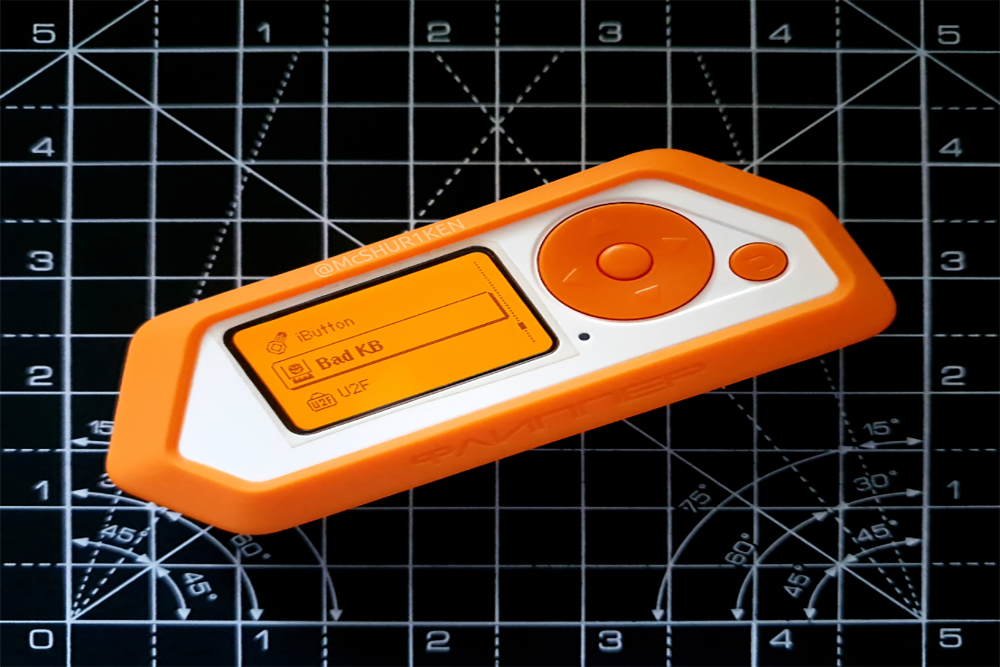
What if we told you… that the Bad “USB” attack could be performed… without the “USB” element of it, purely...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067