Email Spoofing Tools Behind Modern Attacks
Email spoofing is not a new threat.What has changed is how quietly it succeeds.Modern spoofing rarely depends on obvious fake addresses or poor language.It...
Found 529 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Email spoofing is not a new threat.What has changed is how quietly it succeeds.Modern spoofing rarely depends on obvious fake addresses or poor language.It...
Automation has quietly changed the balanceCyber-attacks are no longer driven only by people sitting behind screens.Much of the activity now comes from syst...
International discussions on cyber issues rarely resemble crisis meetings.They look closer to trade talks or arms control negotiations.The tone is measured...
The cybercriminal group APT36, or Transparent Tribe, has launched a series of cyber-attacks on Indian government, educational, and military organizations....
Most attacks do not work the first time.That is expected.What matters is not the initial failure, but what follows. Attackers observe what stopped them, ad...
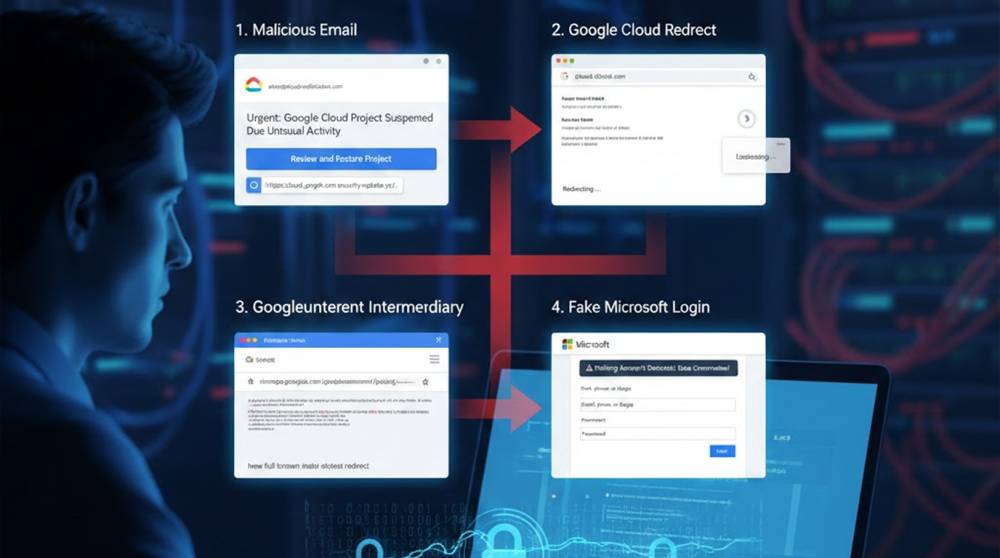
Cybersecurity experts discovered a new type of phishing attack using the Google Cloud's Application Integration service to send email from a legitimate-loo...
Network segmentation limits lateral movement, so if one system is compromised, attackers cannot freely roam.Weak or inconsistent segmentation is common. Ev...
API abuse rarely announces itself.Requests succeed. Responses are valid. No errors are thrown.From a logging perspective, nothing looks broken.From a busin...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067