Data Theft Extortion: How UNC3753 Strikes in Hours
You expect phishing emails. You train your team to spot suspicious links. But what happens when the attacker calls you directly and sounds exactly like you...
Found 60 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You expect phishing emails. You train your team to spot suspicious links. But what happens when the attacker calls you directly and sounds exactly like you...
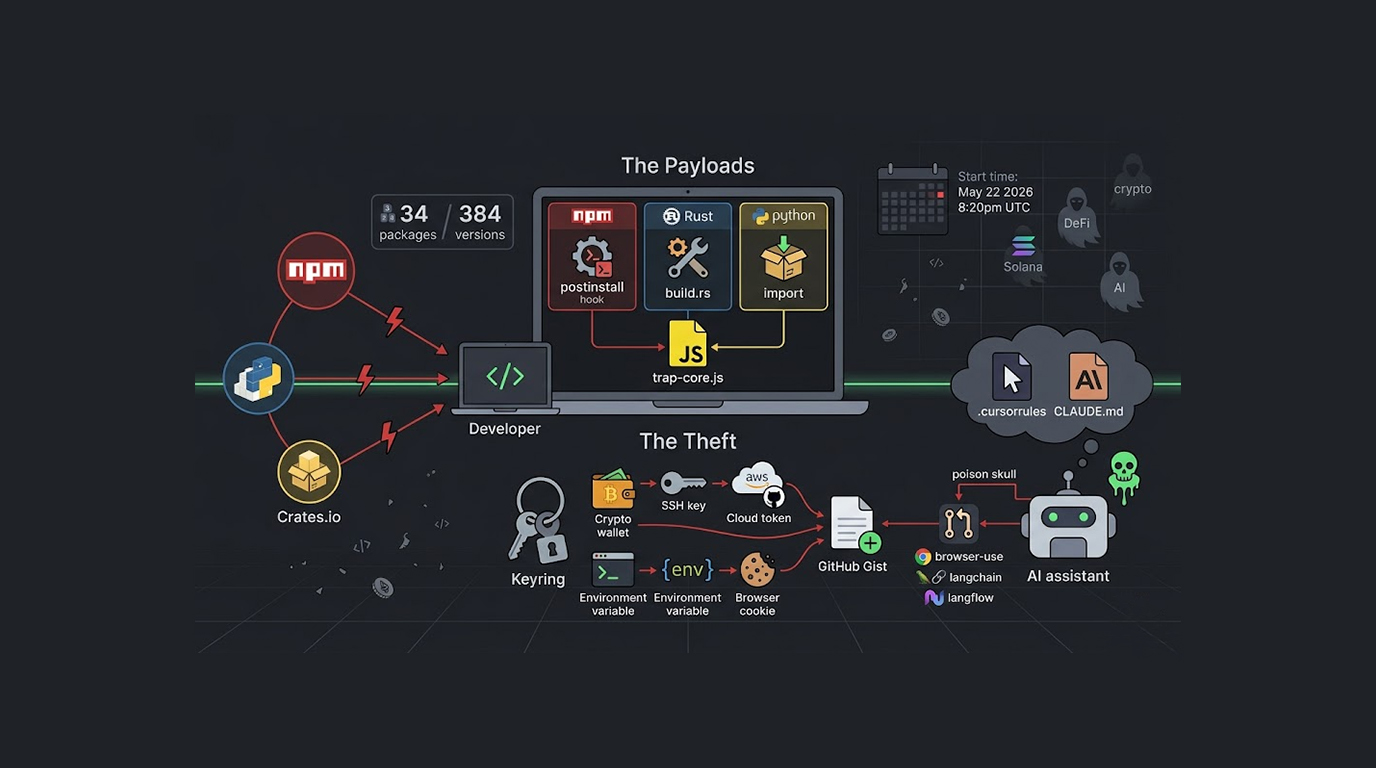
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
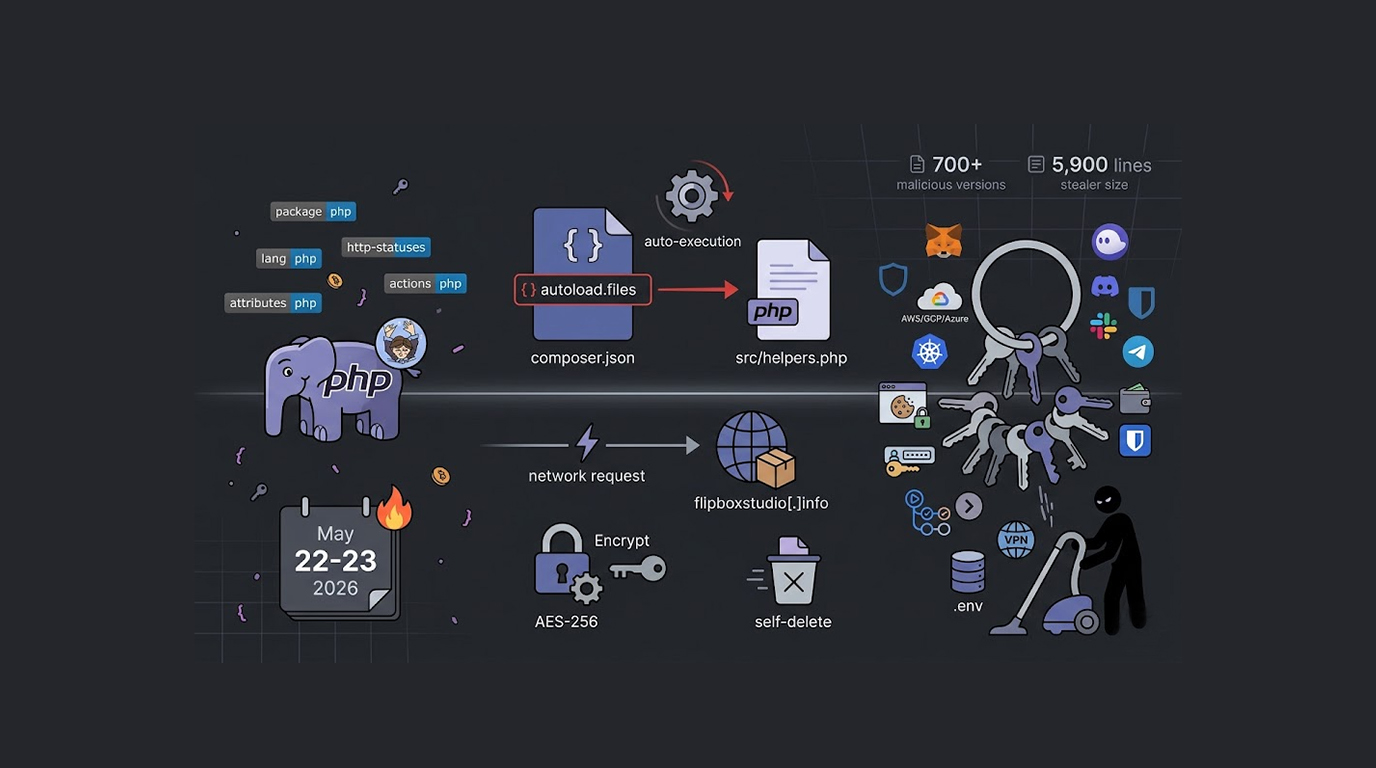
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
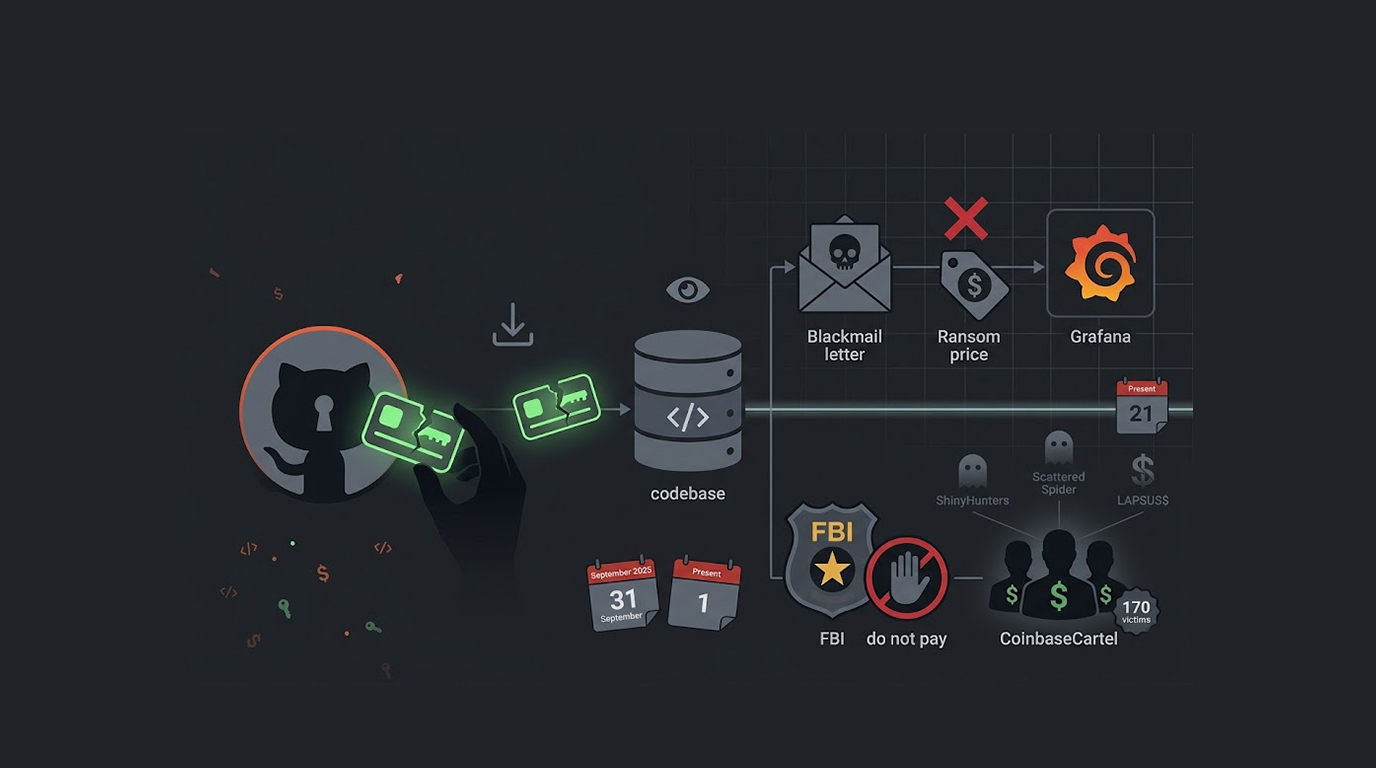
Grafana has disclosed that an unauthorized party obtained a token granting access to the company's GitHub environment, and the attacker used this access to...
You send a text message, you make a phone call, you go about your daySomeone else reads that message, someone else sees who you called, someone else knows...
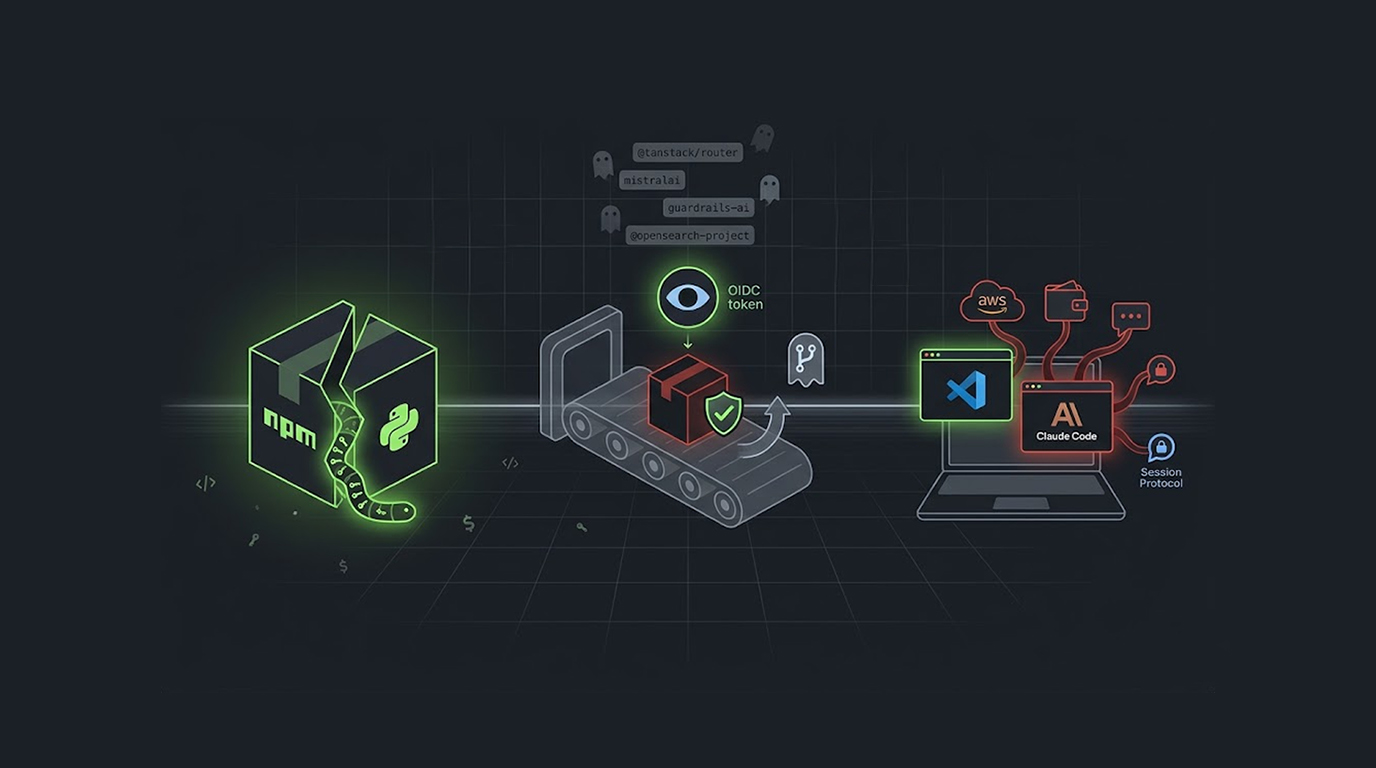
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
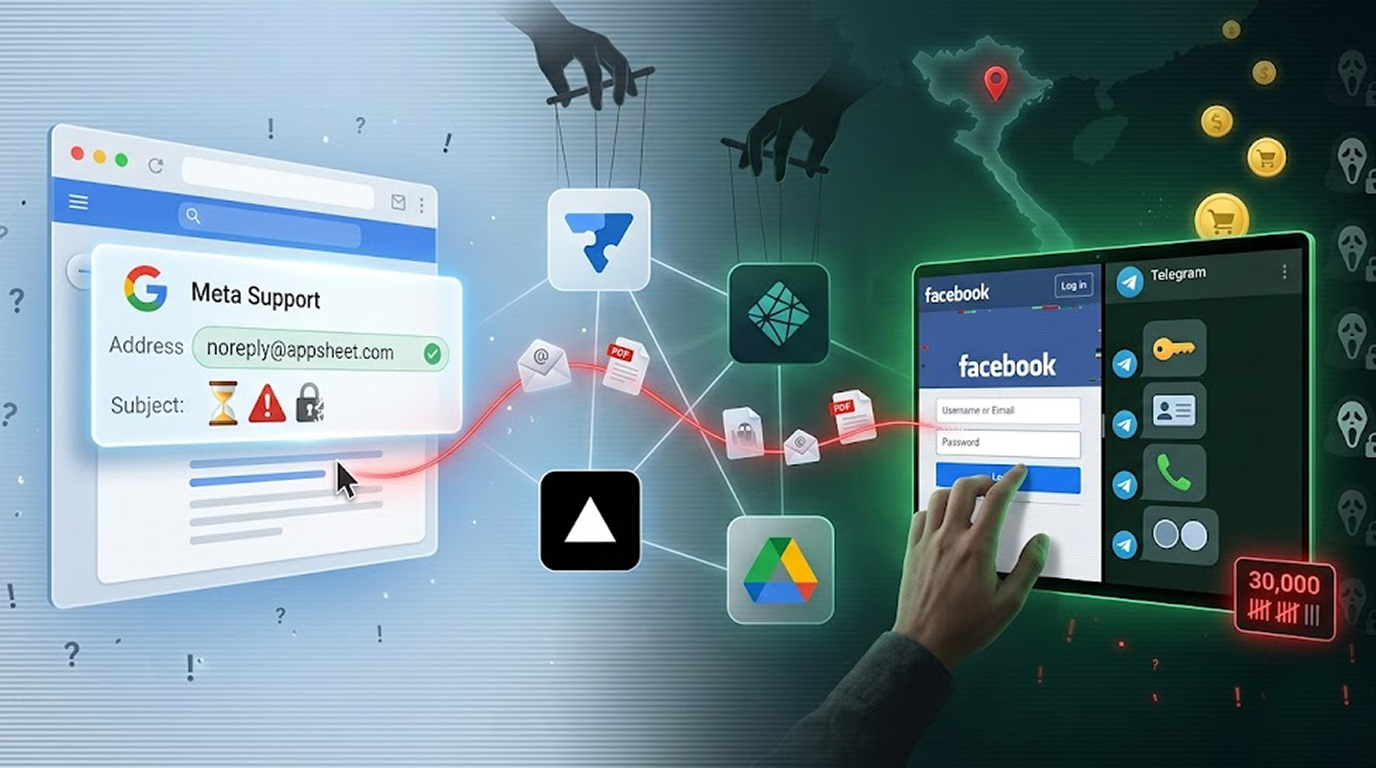
You receive a fake email from Meta Support that looks legitimate, as it was sent from a Gmail address using the @appsheet.com domain (which is operated by...
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067