Xen Flaws: Guest VMs Can Read Dom0 Memory
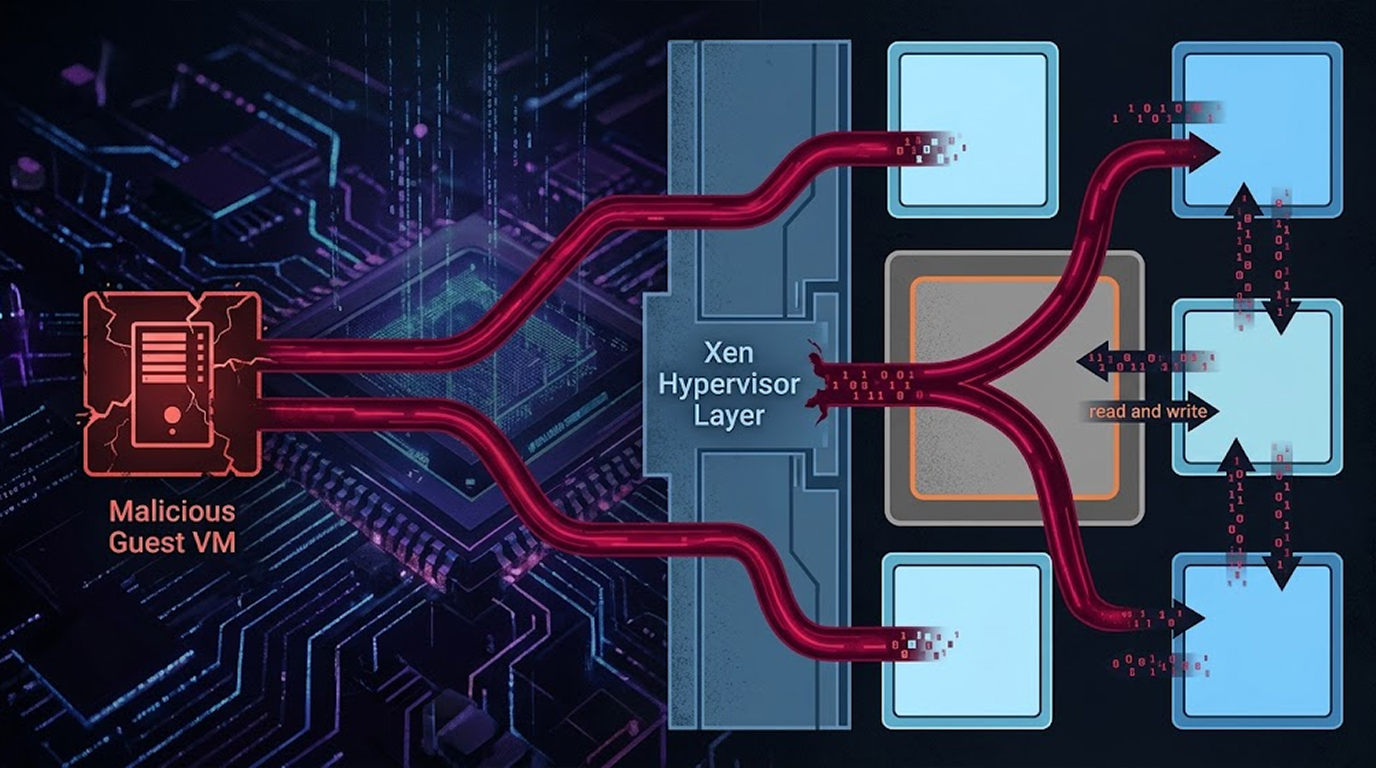
Two flaws in the Xen hypervisor allow a malicious guest virtual machine to read and write the memory of other VMs on the same host. That includes dom0, the...
Found 598 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two flaws in the Xen hypervisor allow a malicious guest virtual machine to read and write the memory of other VMs on the same host. That includes dom0, the...
If you run a BTCPay Server instance on an older version, your hot wallet funds may already be at risk. The project issued an urgent warning this week after...
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
Password reset flows are supposed to be the safest part of an authentication system. You enter an email, you get a link, you click it, you change your pass...
Most Active Directory attacks require credentials, which means the attacker has to steal something first, and that theft is the hard part that gets them ca...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067