Double Extortion Ransomware Explained
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
Found 53 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
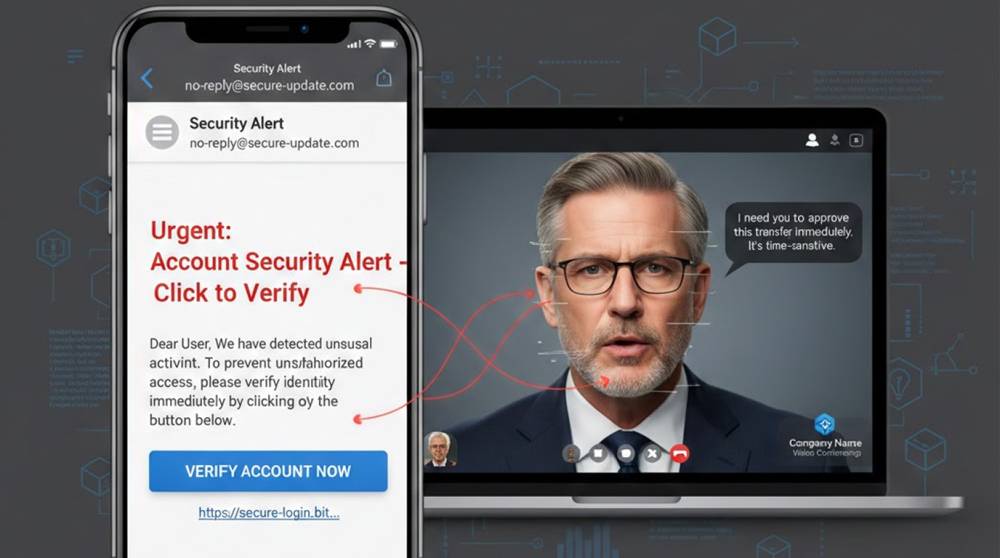
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
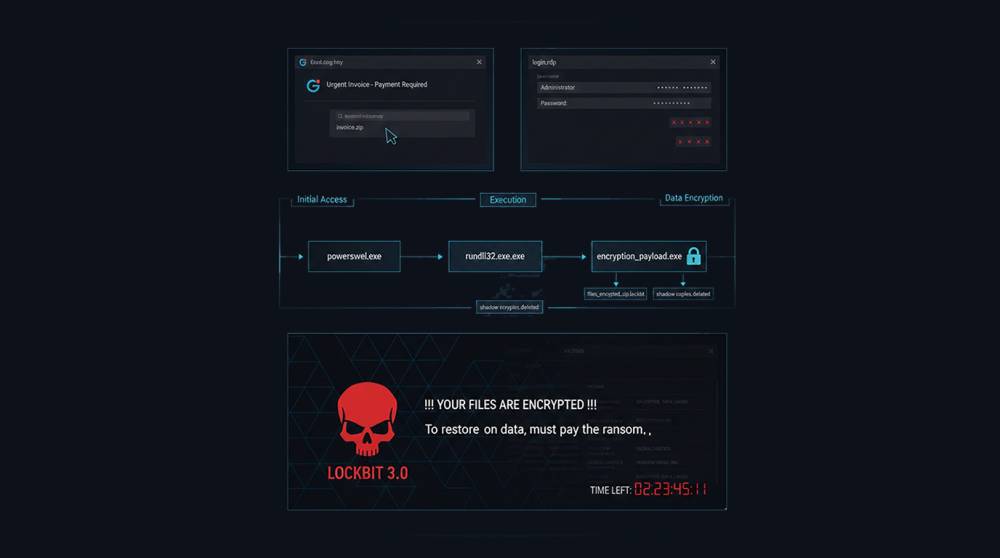
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
Modern software applications continue to fuel a significant increase in zero-day vulnerabilities and their associated exploitation. Zero-day vulnerabilitie...
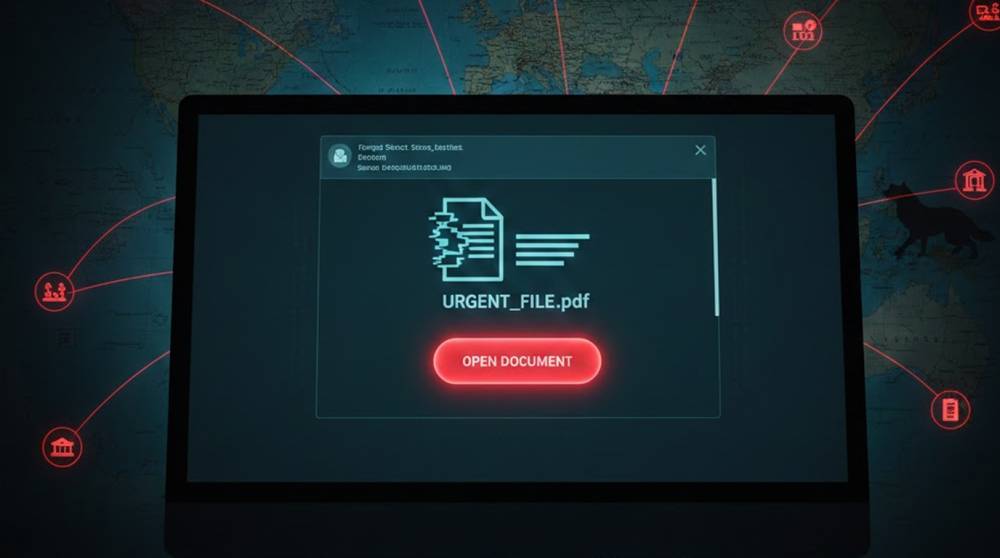
Kaspersky has shed light on a persistent phishing campaign tied to the threat actor Bloody Wolf (tracked by Kaspersky as Stan Ghouls), which has been quiet...
For executives and board members, credentials of a company are not only an IT issue; credential security is also a governance and risk management priority....
Google Dorking (also called Google Hacking) is the technique of using advanced search operators in Google (and sometimes Bing or other engines) to find pub...
The term "Garage APTs" (Advanced Persistent Threats/small teams) in cyber security defines entities that are small, but now can implement APT level operati...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067