Third-Party Risk Red Teaming: Attacking Through Vendors and Partners
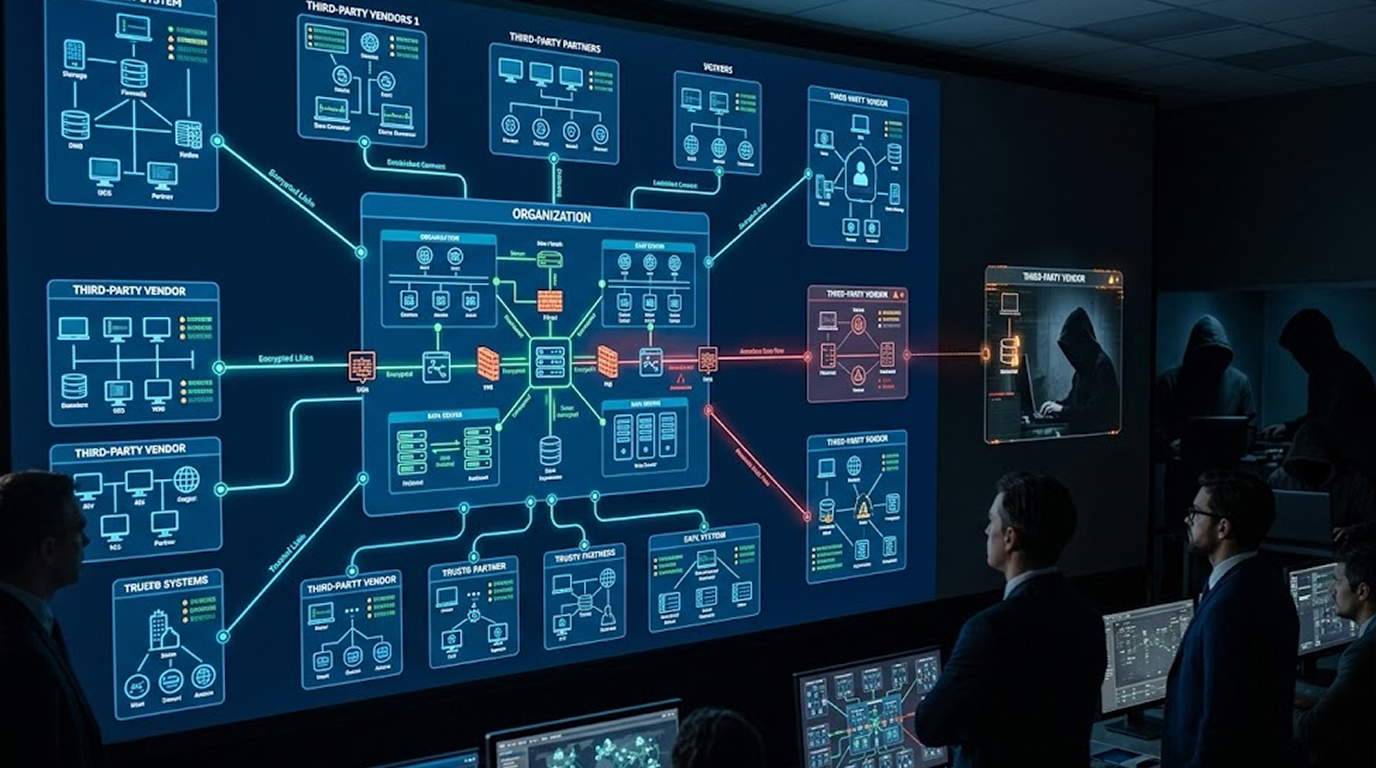
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
Found 55 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
A China-aligned threat actor has resumed targeting European government and diplomatic organizations after a two-year period of relative inactivity in the r...
When you receive a “login from an unusual location” alert, whether from Google, Microsoft, Apple, your bank, or a crypto exchange, it’s e...
Palo Alto Networks Unit 42 discovered a major vulnerability in Google Cloud's Vertex AI that could concern legitimacy of artificial intelligence (AI) agent...
The modern reality is that geopolitical tensions are increasingly being played out through cyber-attacks, which can impact everyday citizens. The year 2026...
In the last couple of years, the cybersecurity community has started seeing a new family of threats nicknamed “Sponge” malware. These aren&rsqu...
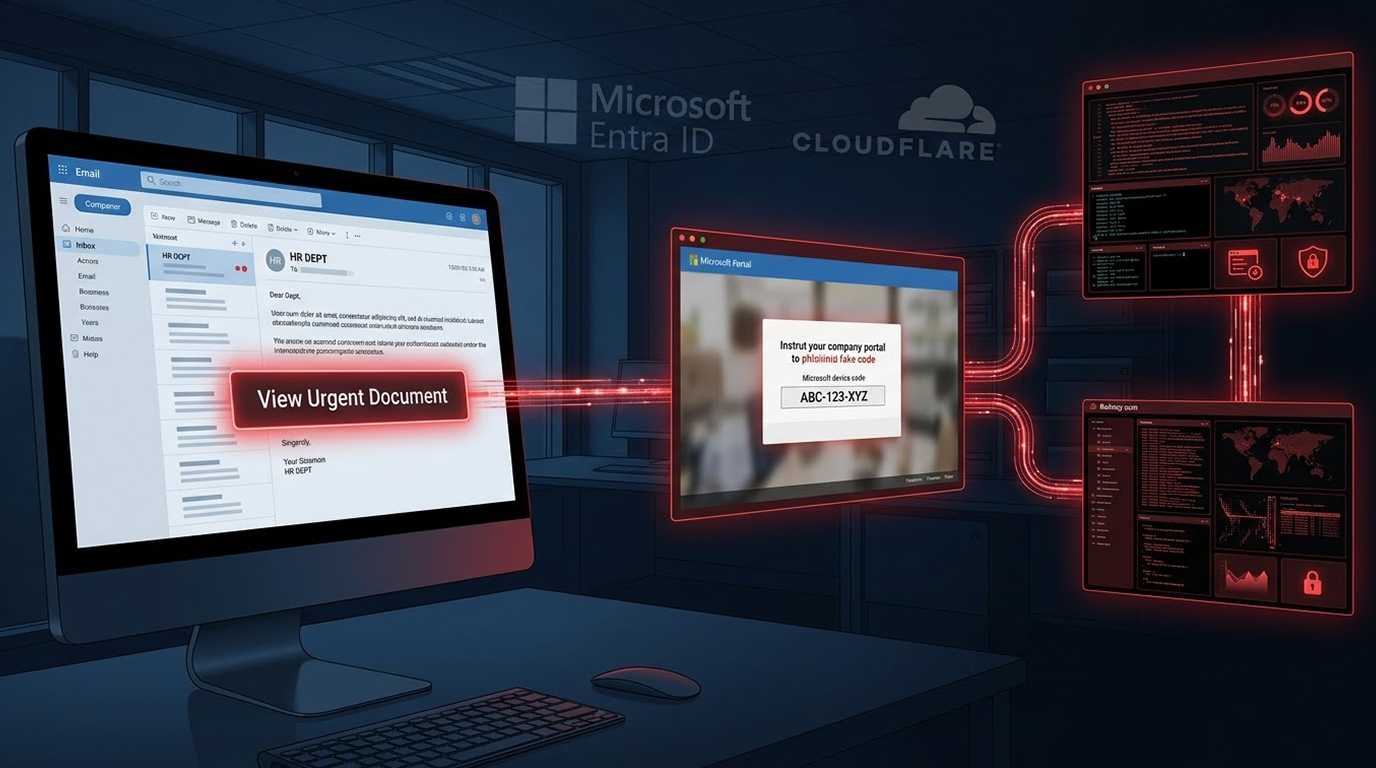
EvilTokens (also called token stealers or OAuth token hijackers) have become one of the fastest-growing threats in 2026. Instead of stealing your password,...
Cybersecurity researchers at Huntress have raised the alarm about a fast-moving device code phishing campaign that is actively targeting Microsoft 365 acco...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067