Top 10 Exposed Ports for Bug Bounty $5k–$50k
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
Found 643 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
CISA has updated its Known Exploited Vulnerabilities (KEV) catalogue, which now contains two vulnerabilities in Section Four of the Roundcube webmail softw...
Cybersecurity researchers at OX Security have disclosed four serious vulnerabilities across hugely popular Visual Studio Code extensions, collectively inst...
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
We’ve entered the phase where the most interesting (and dangerous) cyber conflicts are no longer human hacker vs. human defender. They’re incre...
There is an urgent update from Google for their browser due to a zero-day vulnerability that is currently being used by attackers in the wild. CVE-2026-24...
These three vulnerabilities are among the most common ways attackers break into web applications. They all happen through normal-looking HTTP GET or POST r...
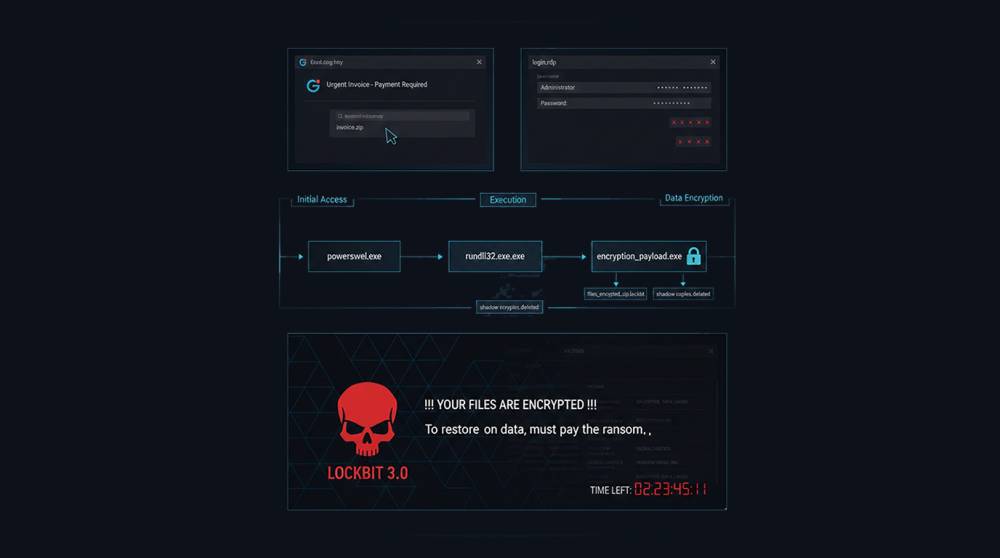
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067