Joomla JCE CVE-2026-48907: Critical RCE Under Attack
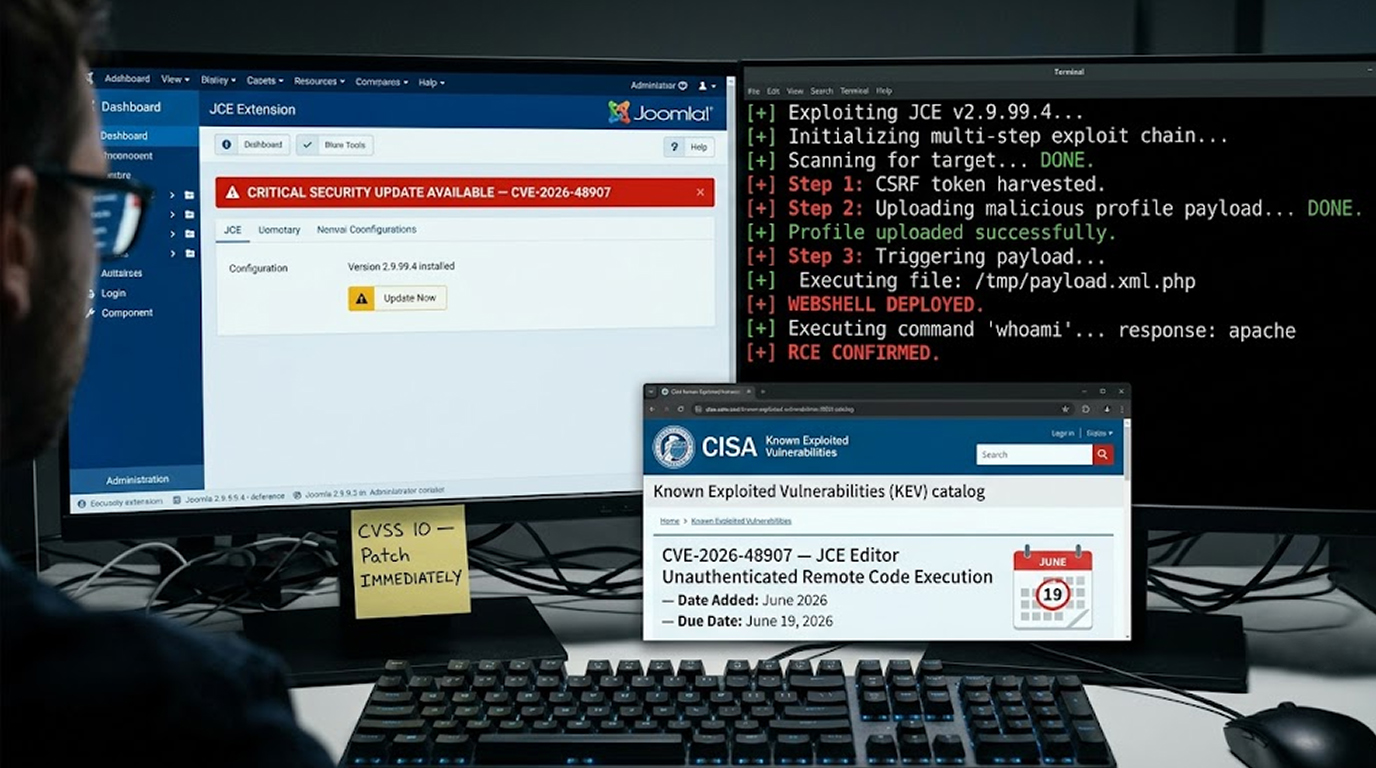
The U.S. Cybersecurity and Infrastructure Security Agency just added a maximum-severity flaw to its Known Exploited Vulnerabilities catalog. Federal agenci...
Found 582 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The U.S. Cybersecurity and Infrastructure Security Agency just added a maximum-severity flaw to its Known Exploited Vulnerabilities catalog. Federal agenci...
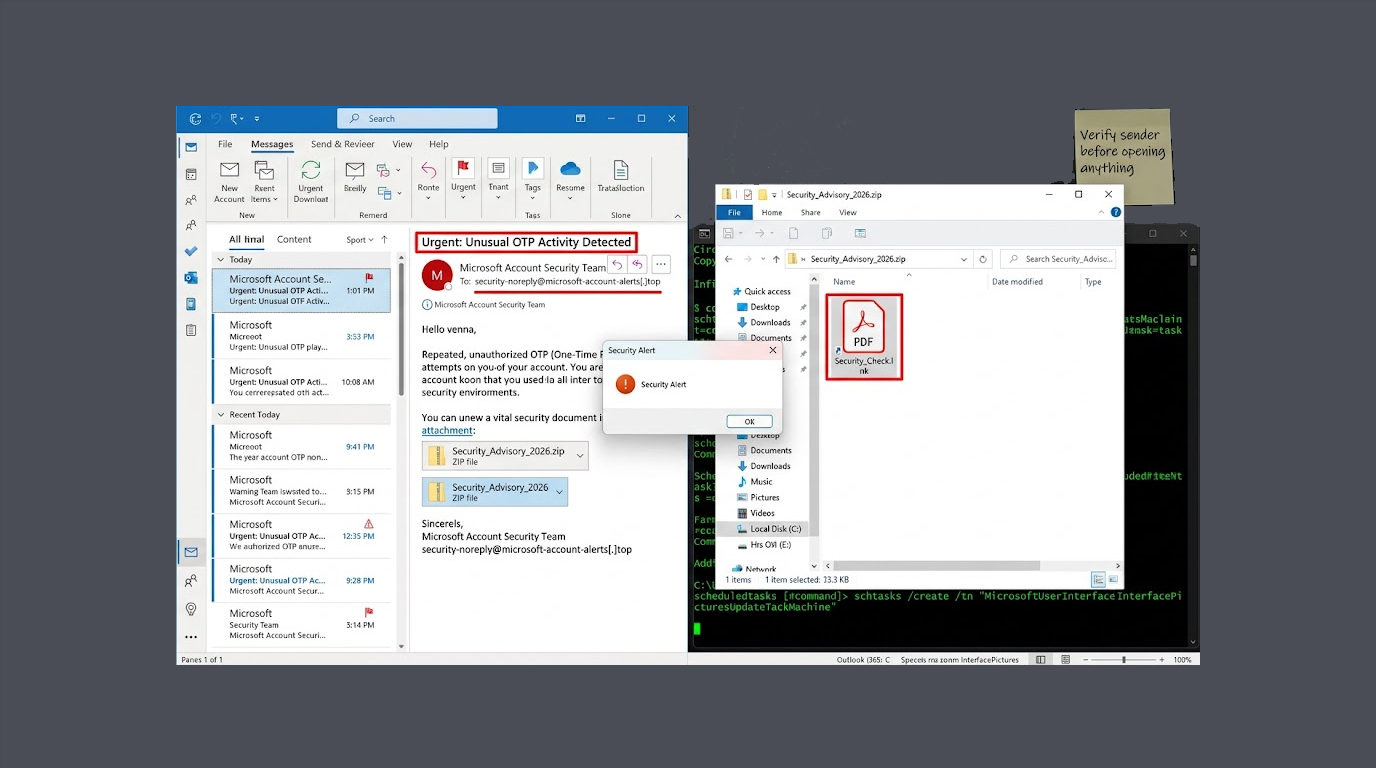
You receive an email. It looks like it is from Microsoft. It warns about suspicious activity on your Microsoft Account. Someone is generating one-time pass...
The U.S. Cybersecurity and Infrastructure Security Agency just added a new vulnerability to its Known Exploited Vulnerabilities catalog. Federal agencies n...
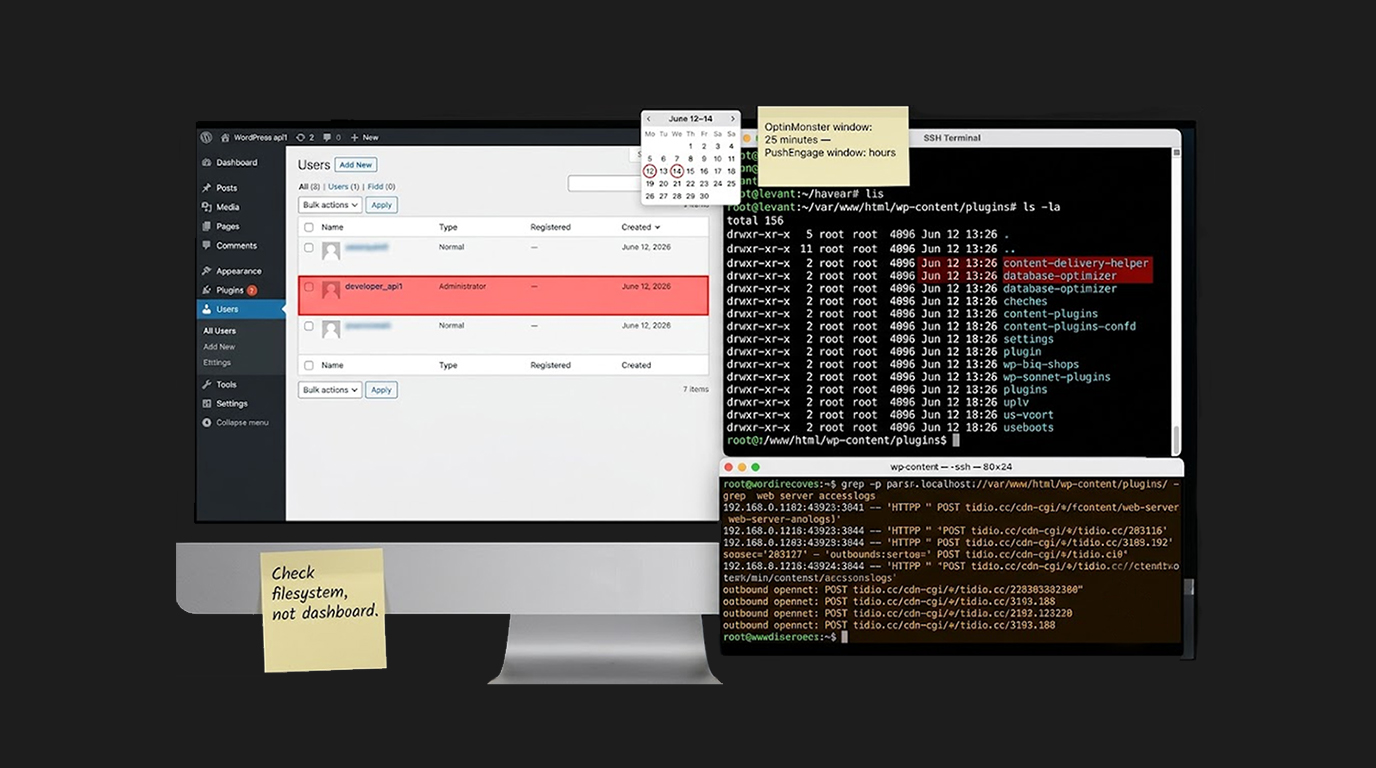
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
Imagine scrolling through Facebook and seeing a post from what looks like your national telecom provider. Free mobile internet package. Click here to claim...
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
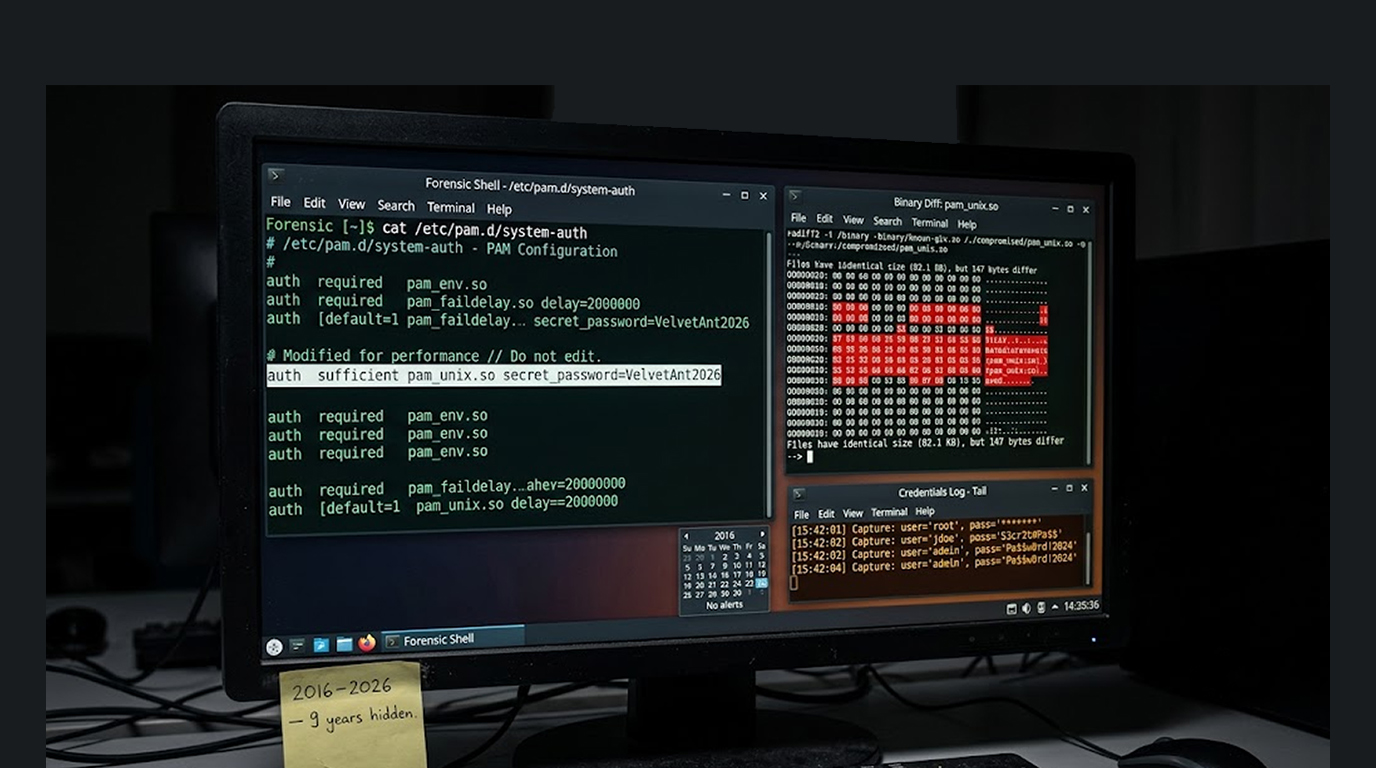
For nearly a decade, a China-nexus threat group avoided every tool defenders use to catch intruders. They didn't drop suspicious files on laptops or server...
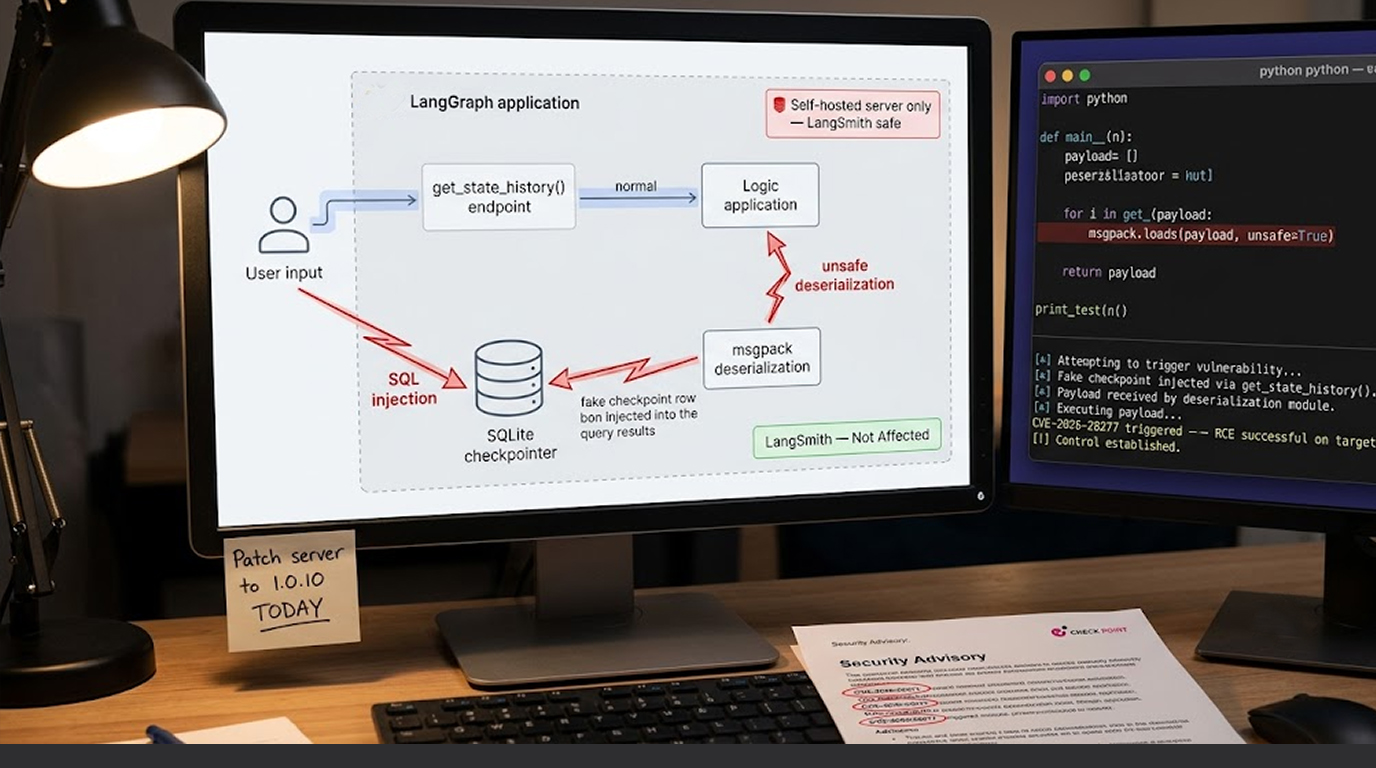
LangGraph is helping you build complex, stateful, multi-agent AI applications. It's open-source, built by LangChain, and widely used by developers who want...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067