VVS Stealer: Python Malware Steals Discord Tokens
In August 2016, a new type of malware called VVS Stealer emerged. VVS Stealer (also known as VVS $\textdll$) is a Python-based information thief that speci...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In August 2016, a new type of malware called VVS Stealer emerged. VVS Stealer (also known as VVS $\textdll$) is a Python-based information thief that speci...
Automation has quietly changed the balanceCyber-attacks are no longer driven only by people sitting behind screens.Much of the activity now comes from syst...
Ransomware is often treated as a sudden technical failure.In practice, encryption is usually the final move in a longer campaign.By the time systems are lo...
The cybercriminal group APT36, or Transparent Tribe, has launched a series of cyber-attacks on Indian government, educational, and military organizations....
Network segmentation limits lateral movement, so if one system is compromised, attackers cannot freely roam.Weak or inconsistent segmentation is common. Ev...
It Usually Starts SmallNo one wakes up and shuts down a city.It usually starts with something.A forgotten VPN account.An exposed remote desktop service.A c...
Cyber warfare isn’t just about networks anymore, it’s in the cloud.Critical infrastructure, enterprises, and governments rely on cloud services...
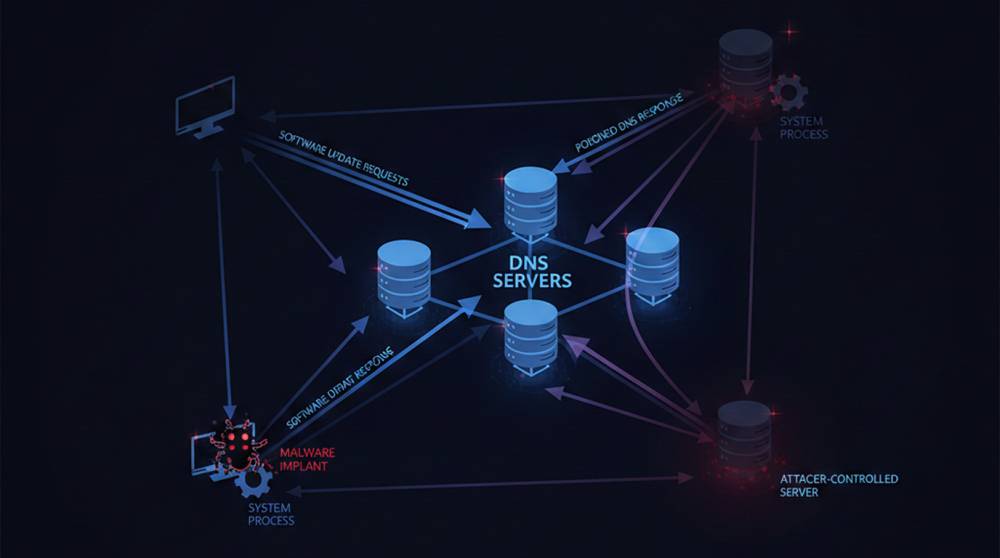
A China-linked advanced persistent threat group has been linked to a sophisticated cyber espionage campaign that weaponized poisoned Domain Name System (DN...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067