Malware Honeypots: Capture Samples Guide
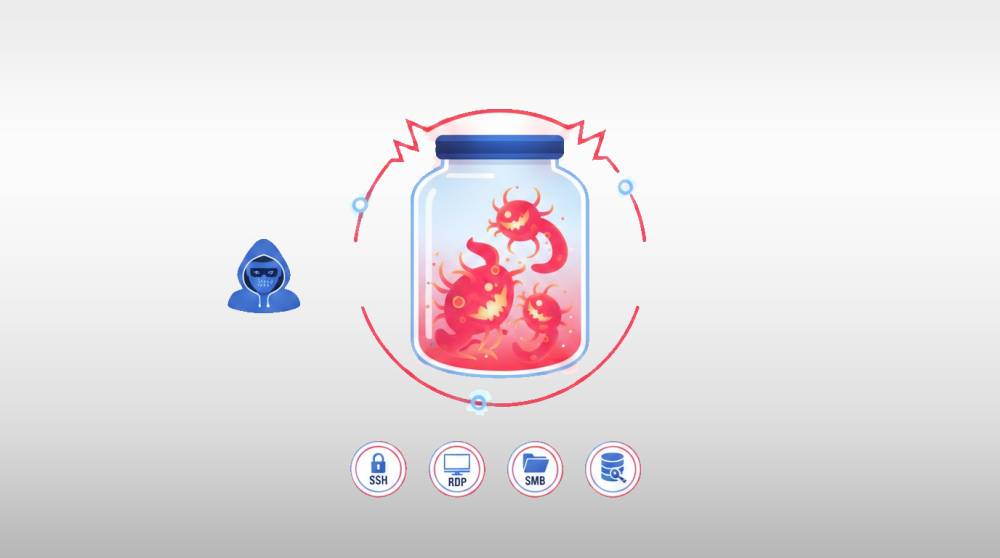
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
Found 427 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
A malicious Google Chrome extension known as CL Suite (by @CLMasters) was caught stealing the confidential information of users of both the Meta Business S...
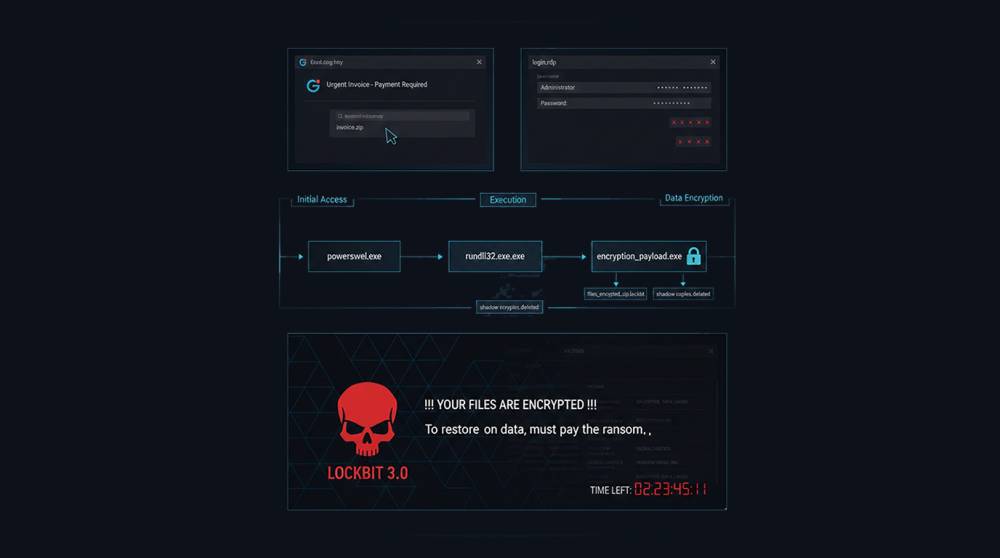
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
CVE-2025-58180 is a critical remote code execution vulnerability (CVSS 7.5) in OctoPrint versions ≤ 1.11.2 (patched in 1.11.3, released September 2025)....
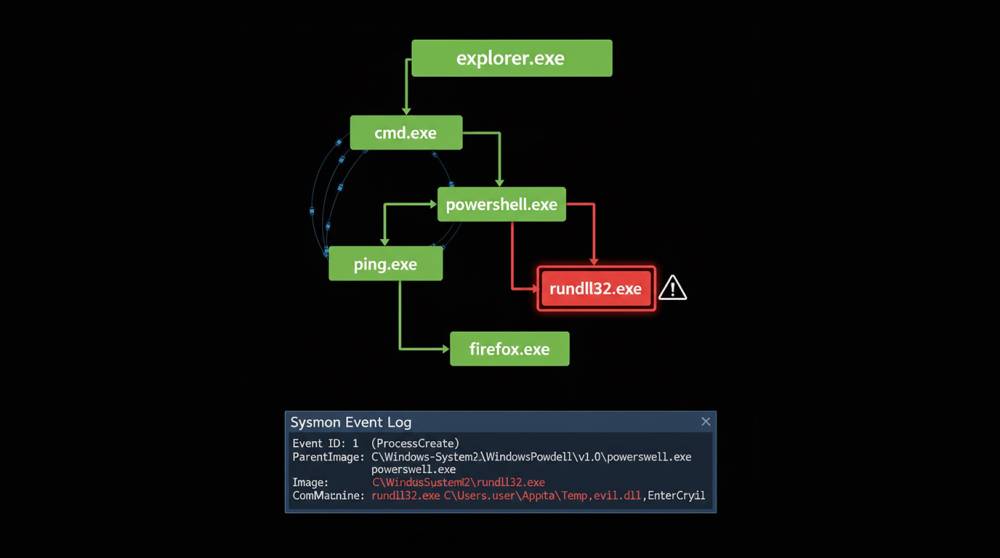
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
Today, attackers have transitioned from using traditional fixed payloads in cyber campaigns (ransomware attacks, espionage, infostealer operations, and phi...
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
Atomic Red Team is an open-source library of small, focused tests mapped to the MITRE ATT&CK framework. These tests simulate real adversary behaviors t...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067