Email Spam Traps: How They Catch Spammers
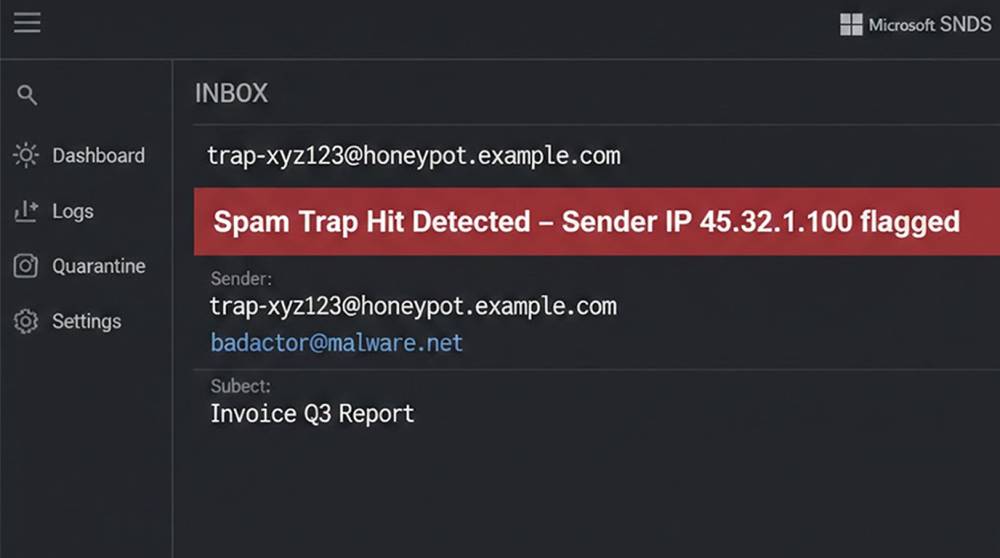
Spam traps (sometimes called honeypot emails or spamtrap addresses) are email addresses that no real person ever owns, uses, or signs up with. They exist o...
Found 82 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Spam traps (sometimes called honeypot emails or spamtrap addresses) are email addresses that no real person ever owns, uses, or signs up with. They exist o...
When hospitals or medical schools get hit by ransomware or other cyber attacks, it’s not just an IT headache , it becomes a direct threat to patient...
Espionage today is no longer primarily about stealing laptops in hotel rooms or planting bugs in conference rooms. The most effective and lowest-risk vecto...
File sharing may seem commonplace and trivial, such as dropping a document into a folder on a team's shared storage area or emailing someone a URL to acces...
Many times input validation failures are not treated properly by applications validation or sanitizing the data provided by users. Attackers use these fail...
Cybersecurity incidents go beyond simply being technical issues; they also have significant adverse effects on a business's overall success, and can affect...
Many people only discover a problem when someone else tells them.A friend asks, “Did you really send this?”A customer replies to a message you...
Ransomware is often treated as a sudden technical failure.In practice, encryption is usually the final move in a longer campaign.By the time systems are lo...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067