Ransomware Lateral Movement via SMB Errors
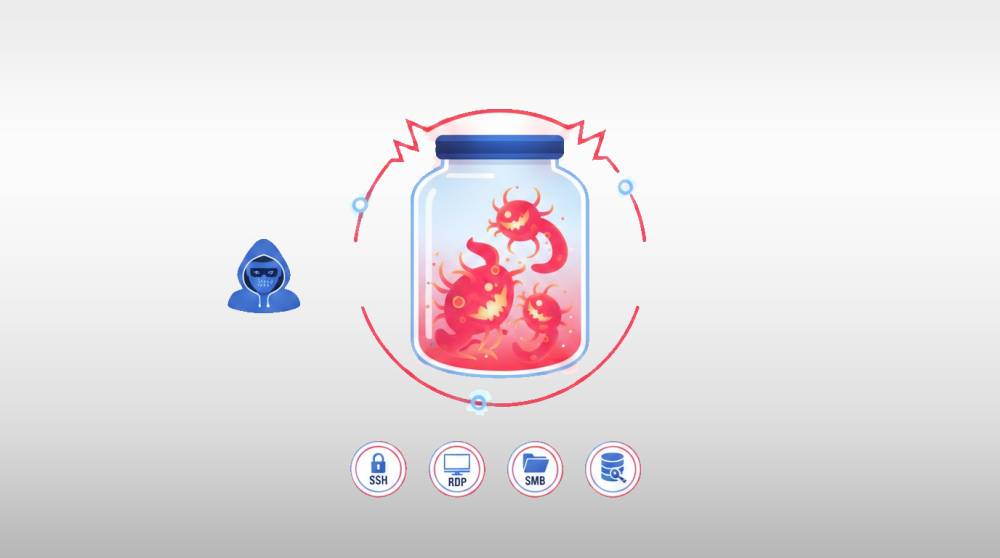
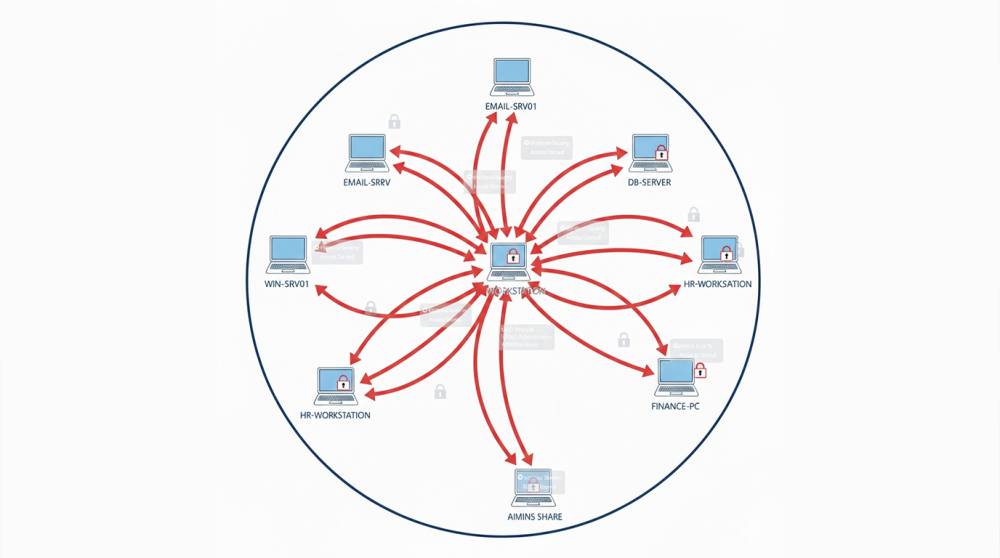
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
Found 44 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
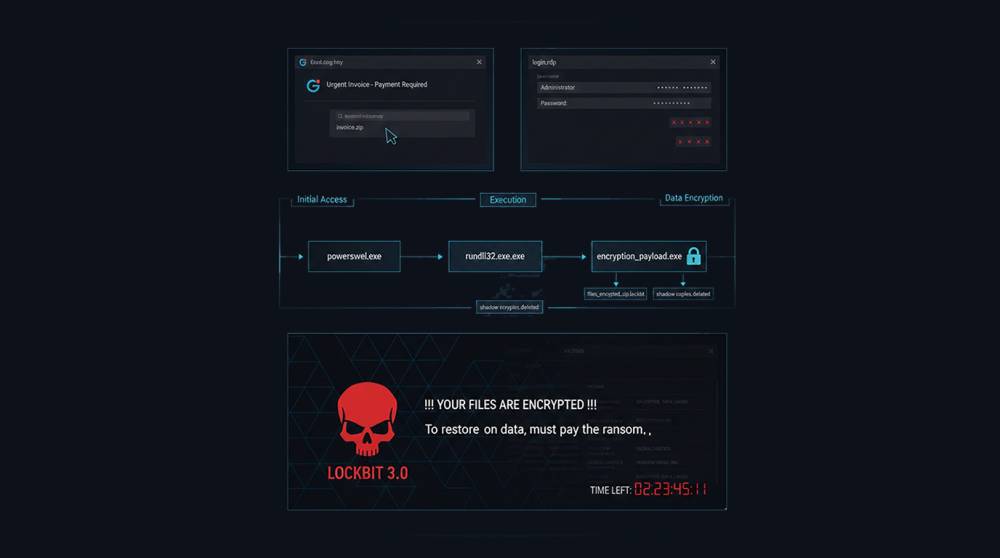
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
The Apache logs (access.log) are an incredibly useful resource for detecting attacks, reconnaissance, brute-force attempts, exploits, and data exfiltration...
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
An example of unauthorized network authentication is when an attacker logs into your Wi-Fi, VPN, Active Directory, RDP, SSH, cloud console or any other ser...
Event logs are one of the most reliable sources of truth during a security incident.Attackers may hide, but their actions leave traces. Why Event Logs Mat...
Companies today rely heavily on web applications for conducting their business. From online banking sites to ecommerce stores, web applications serve three...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067