Build a $0 Ethical Hacking Lab in 2026
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Found 31 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Many times input validation failures are not treated properly by applications validation or sanitizing the data provided by users. Attackers use these fail...
The WordPress Quiz Maker plugin has been found to have a severe SQL injection vulnerability that could allow an unauthenticated attacker to retrieve sensit...
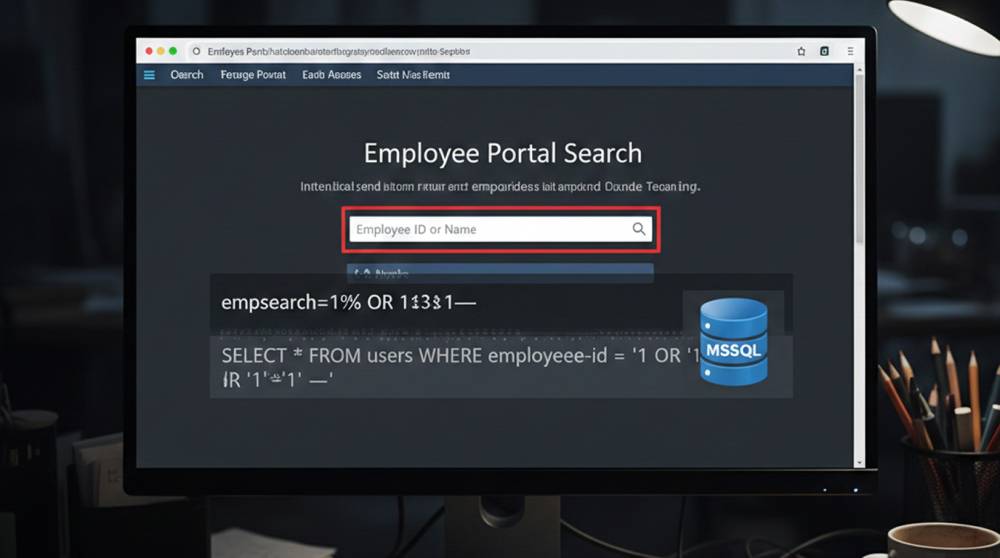
Summar Employee Portal versions before 3.98.0 had a SQL injection vulnerability. This affects the Employee Directories feature of the software under the au...
phpIPAM is often perceived as a hidden benefit for companies and their employees as many administrators see it as a resource they use throughout their day-...
The SQL Injection vulnerability in phpMyAdmin has been identified to be present in version 5.0.0 of the software, affecting the server privileges feature o...
Attackers don’t waste time on fancy zero days unless they really need to. Most of the active exploitation you see today comes from old, unpatched, ea...
When testing web applications, one of the most revealing steps for a penetration tester or a malicious actor is database file enumeration. It’s that...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067