How to Check Social Media Login History for Suspicious Activity
Your social media accounts contain both your personal and professional information, you must be aware of when someone has accessed your account and who the...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your social media accounts contain both your personal and professional information, you must be aware of when someone has accessed your account and who the...
A vulnerability discovered in the telnet daemon (telnetd) included in the GNU InetUtils package has been present on production systems for almost 11 years....
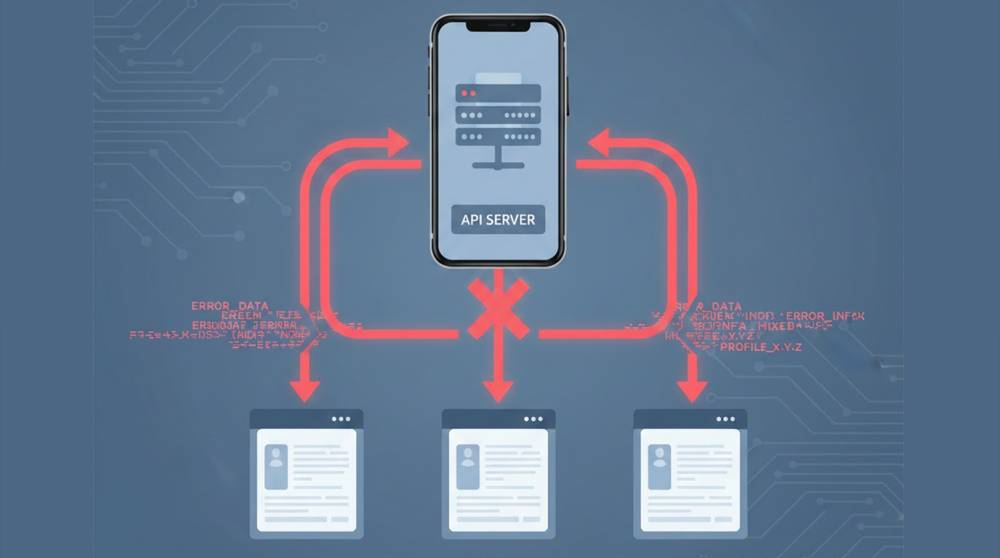
The mobile app wasn’t hacked.The API was trusted too much.That trust exposed user data—quietly, consistently, and at scale.This is one of the m...
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
Cybersecurity research teams have uncovered a cross-site scripting (XSS) vulnerability in StealC' web-based administration panel, which is used by those wh...
A blacklisted domain doesn't just fail quietly; its real-life effects include: 1. Emails being sent directly to the spam folder 2. Visitors seein...
Event logs are one of the most reliable sources of truth during a security incident.Attackers may hide, but their actions leave traces. Why Event Logs Mat...
In 2026, most work still happens in a browser.Email, cloud apps, admin panels, dashboards, internal tools all run there.Attackers know this.Instead of brea...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067