TrapDoor Supply Chain Attack Hits npm PyPI Cratesio
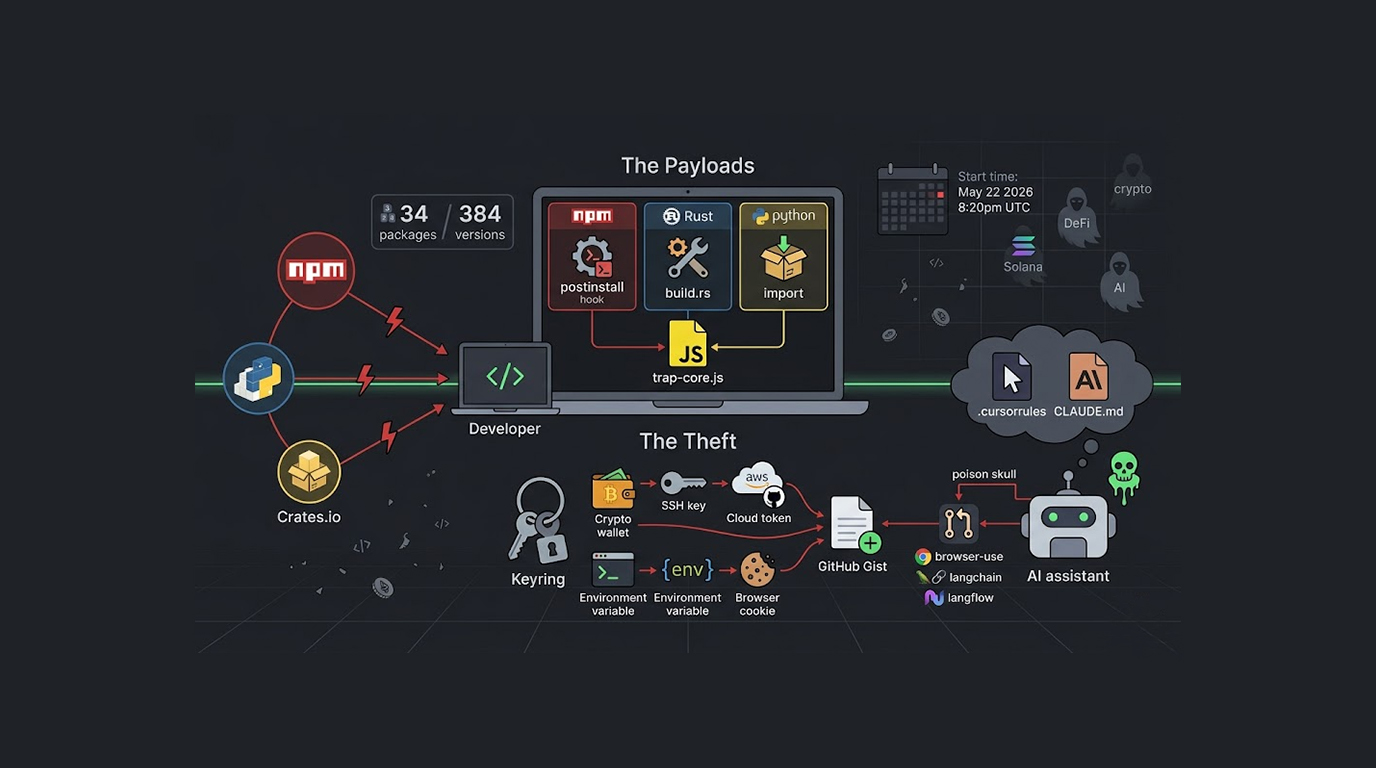
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
Found 792 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
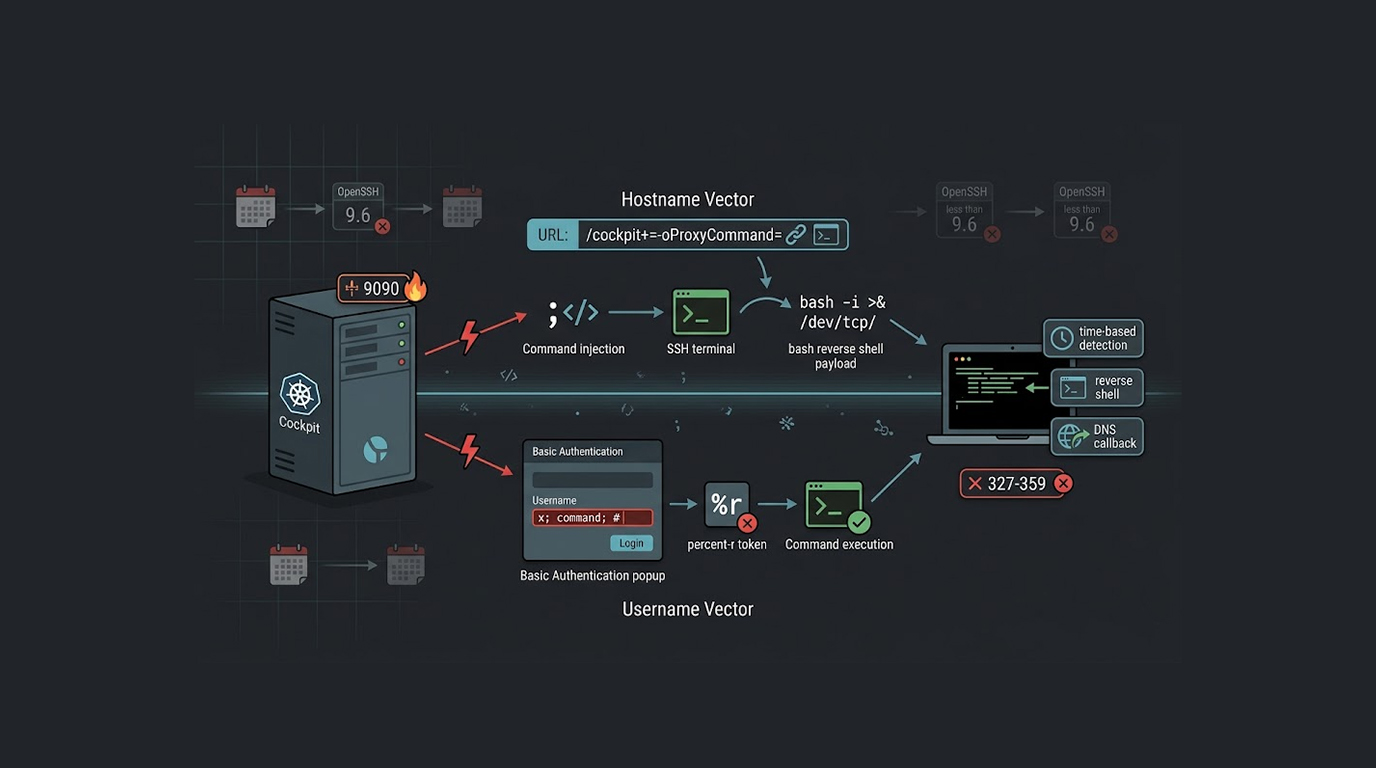
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
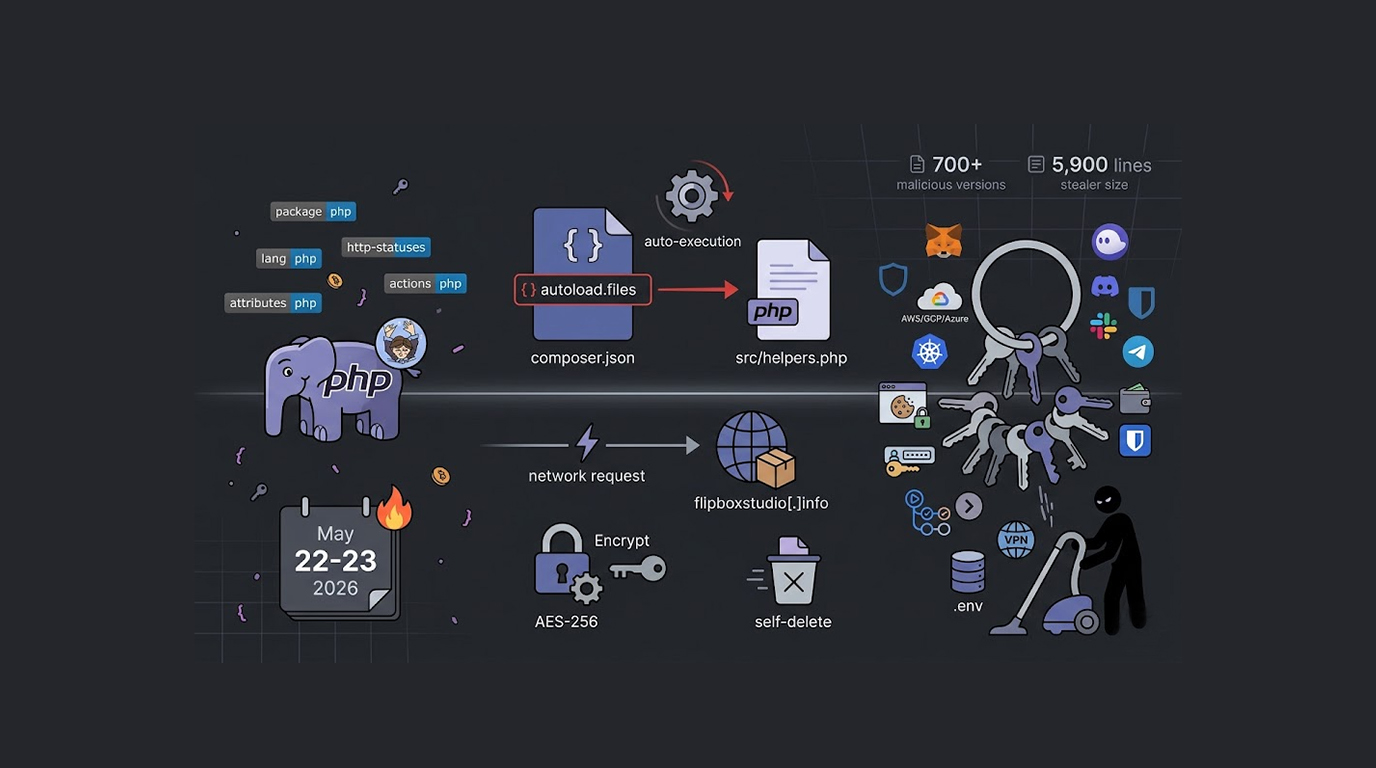
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
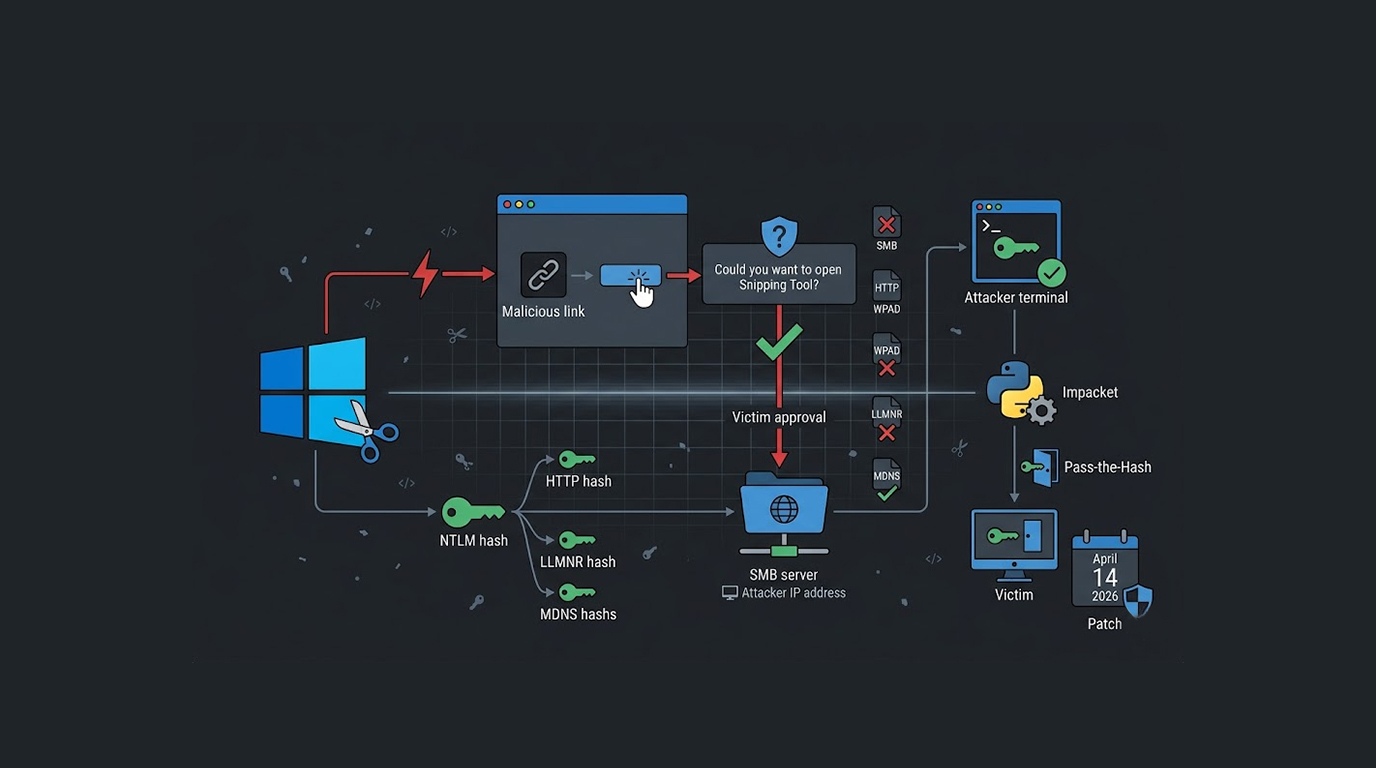
A single click on a malicious link, a quick approval of the "Open Snipping Tool" prompt, and your Windows password hash is on its way to an attacker. The...
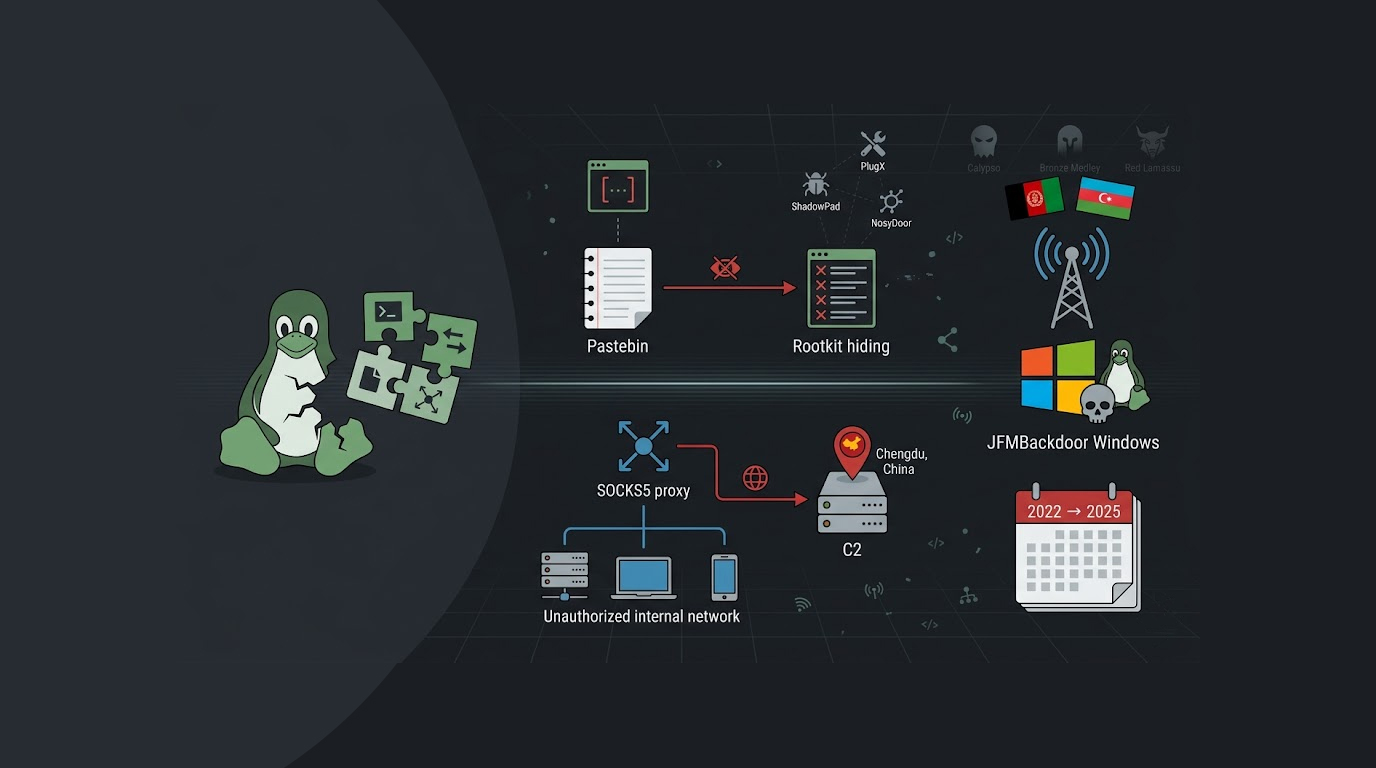
Showboat malware targets MT companies in the Middle East. It looks like was created by someone linked to Chinese-sponsored organizations and has been utili...
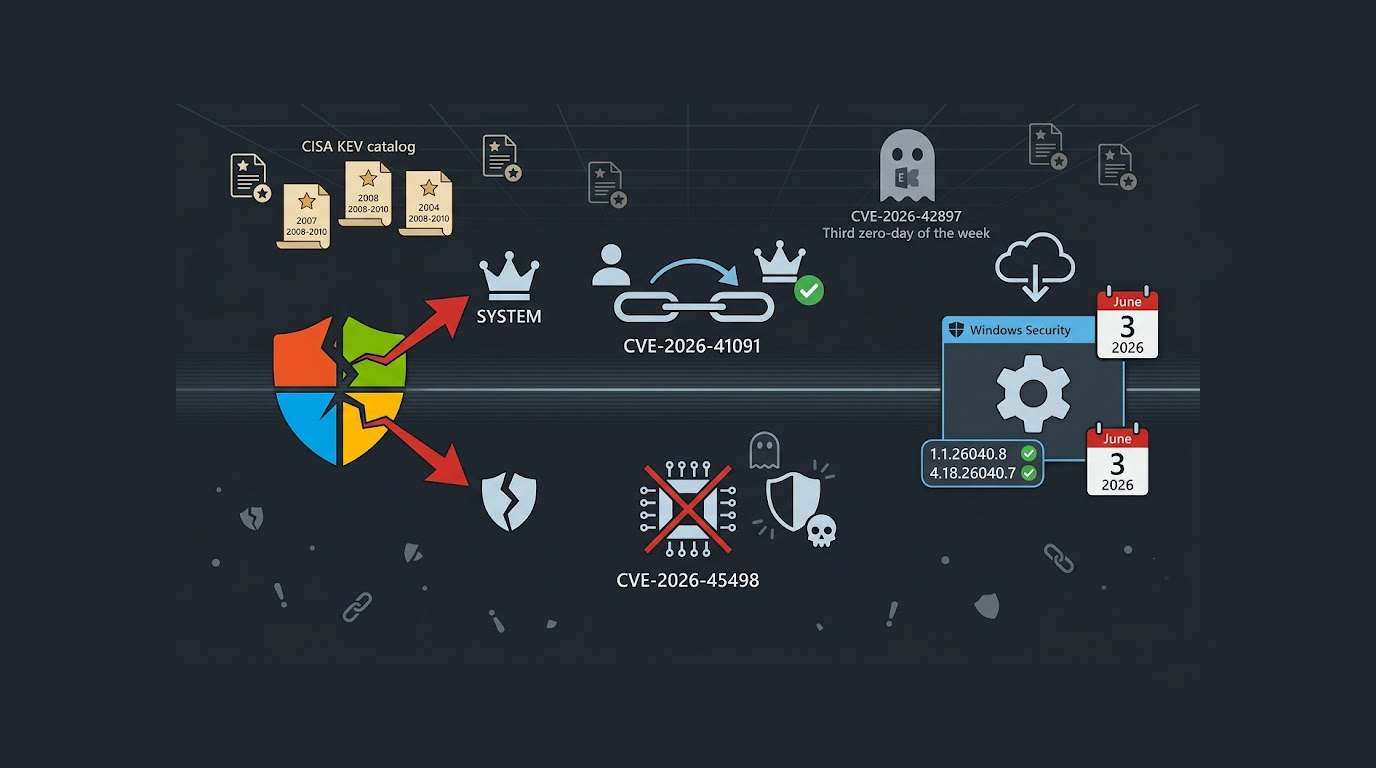
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
You open Instagram, and you see a photo you never posted. It is a strange product you have never heard of, and the caption is full of weird hashtags. You...
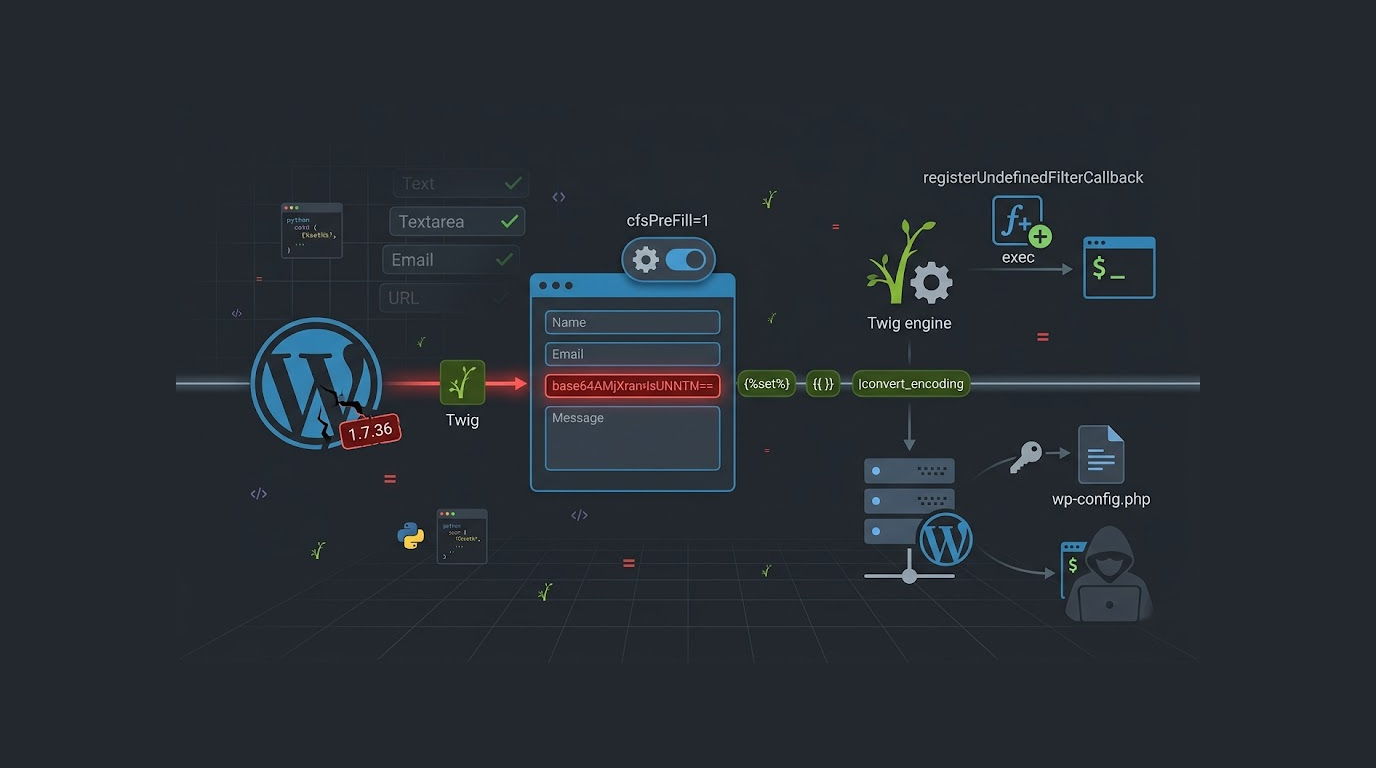
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067