Piranha CMS 12.0 Stored XSS (CVE-2025-57692)
Piranha CMS version 12.0, which was released approximately halfway through 2025, has a stored cross-site scripting (XSS) vulnerability (CVE-2025-57692). An...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Piranha CMS version 12.0, which was released approximately halfway through 2025, has a stored cross-site scripting (XSS) vulnerability (CVE-2025-57692). An...
Olevba is a powerful, free tool specifically designed to analyze Microsoft Office documents (Word, Excel, PowerPoint) for malicious VBA macros and other em...
A common misconception people have about malware is that it has to have a frightening name (like “virus.exe”) and sometimes the malware will ha...
Living off the Land is a modern malware technique that exploits built-in Windows tools, and legitimate programs, as opposed to leaving behind nefarious fil...
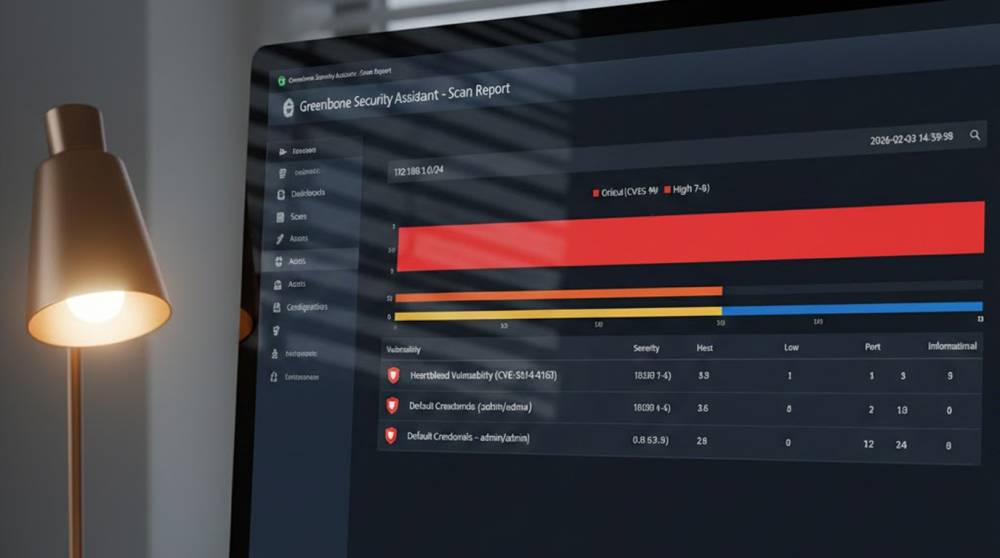
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
OpenVAS (Open Vulnerability Assessment System) is one of the most widely used free and open-source vulnerability scanners available today. It is the commu...
According to Cybersecurity firm Socket, a sneaky supply chain compromise on the Open VSX Registry (the open-source alternative to Microsoft's VS Code exten...
Many employees use personal or unapproved accounts of ChatGPT, Claude, Gemini, Grok, Perplexity, or similar LLMs, often because the official company-...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067