AI-Obfuscated Binaries: LLM Unique Control Flow
In 2025–2026 one of the most powerful (and increasingly common) ways malware authors evade static detection and signature-based AV/EDR is letting a l...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In 2025–2026 one of the most powerful (and increasingly common) ways malware authors evade static detection and signature-based AV/EDR is letting a l...
The fastest way attackers permanently destroy a brand’s entire social media presence isn’t hacking every account individually , it’s comp...
The message “Error 404: Page Not Found” is something we all see daily on websites. But when an entire business or critical parts of it suddenly...
Quiet corporate sabotage seldom presents itself via loud headlines or visible destruction and its movement is one which takes time, remains inconspicuous a...
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
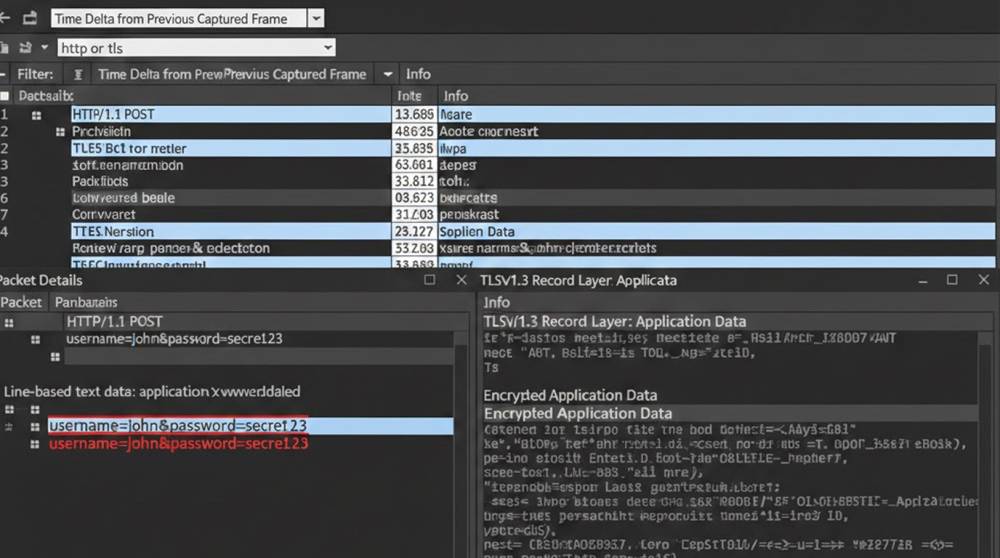
When you capture network traffic with Wireshark, the difference between plaintext (HTTP) and encrypted (HTTPS/TLS) becomes very obvious and very usef...
4xx Status Codes indicate there is an issue with your request; in this case, there is an issue with what the client (Chrome/Safari/etc) is doing, rather th...
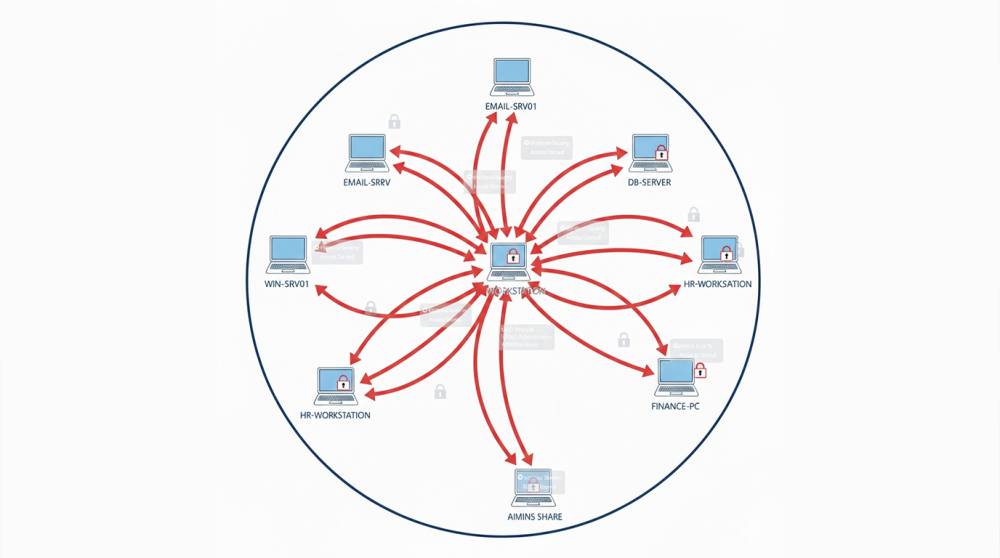
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067