Network Interception for Tokens: When HTTPS Isn't Enough
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
According to recent research, content within the mail could breach its message boundaries and affect the functionality of the webmail platform itself. ...
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Entra ID researcher Dirk-jan Mollema has uncovered a technique that allows malware already running on a compromised Windows machine to silently use a victi...
A phishing kit called Kali365 is turning a legitimate Microsoft login into a gateway to corporate data. The kit targets US organizations with attacker-cont...
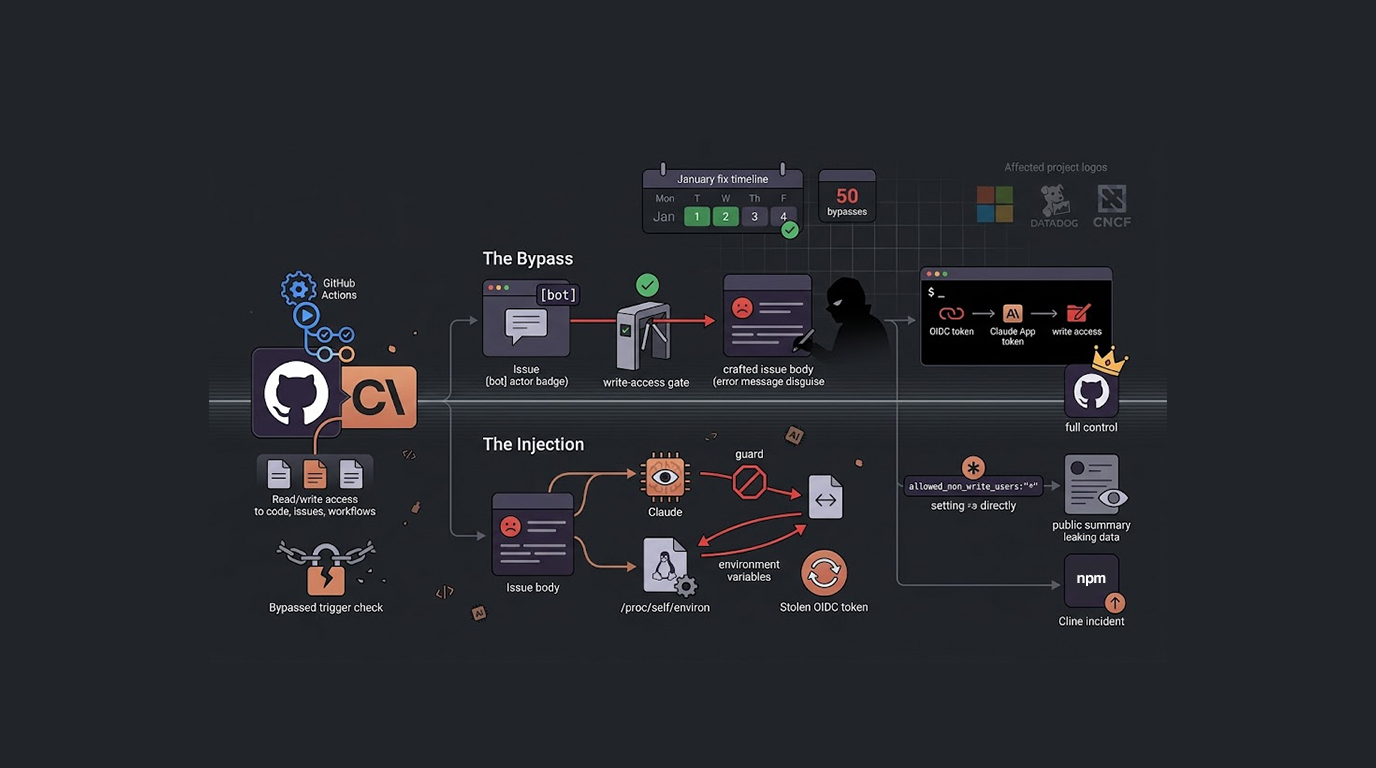
A security researcher found a flaw in Anthropic's Claude Code GitHub Action that let an attacker take over vulnerable public repositories, and all it took...
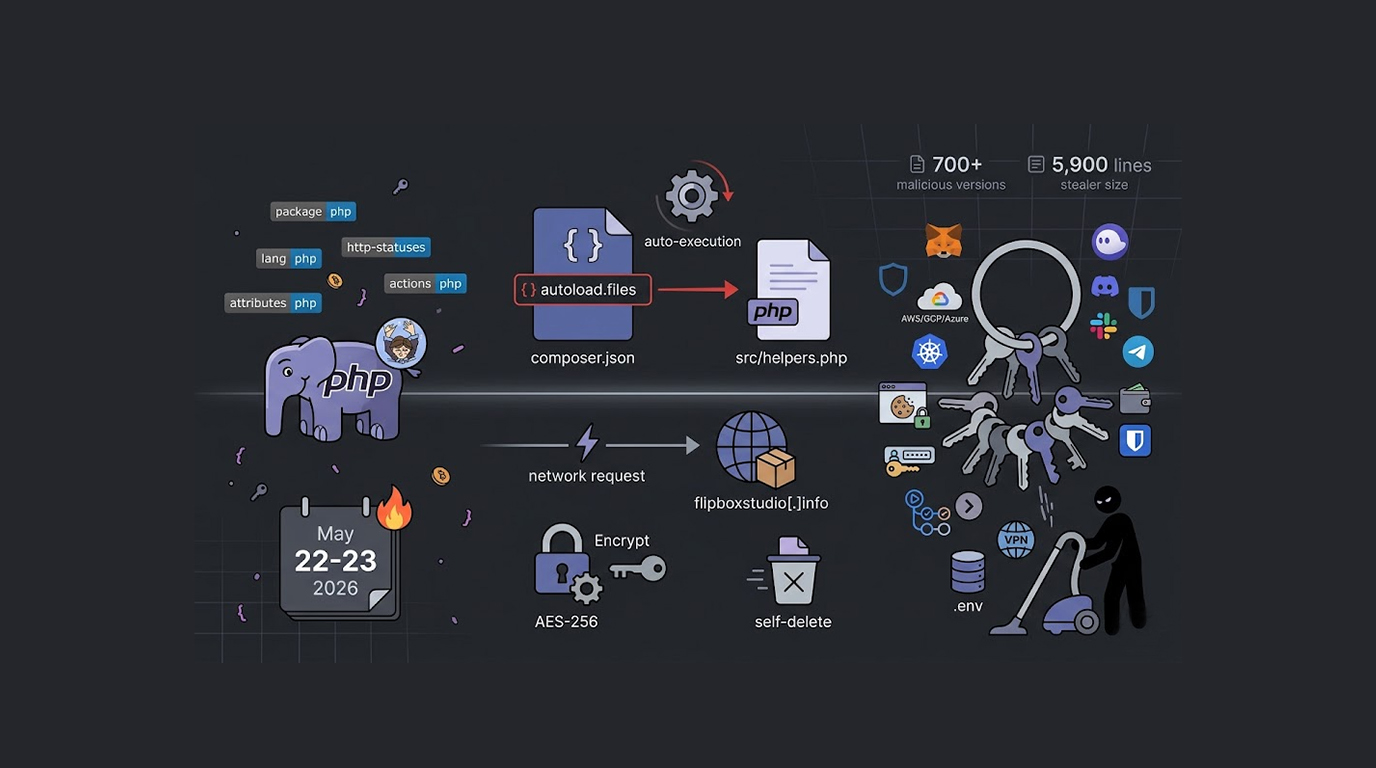
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
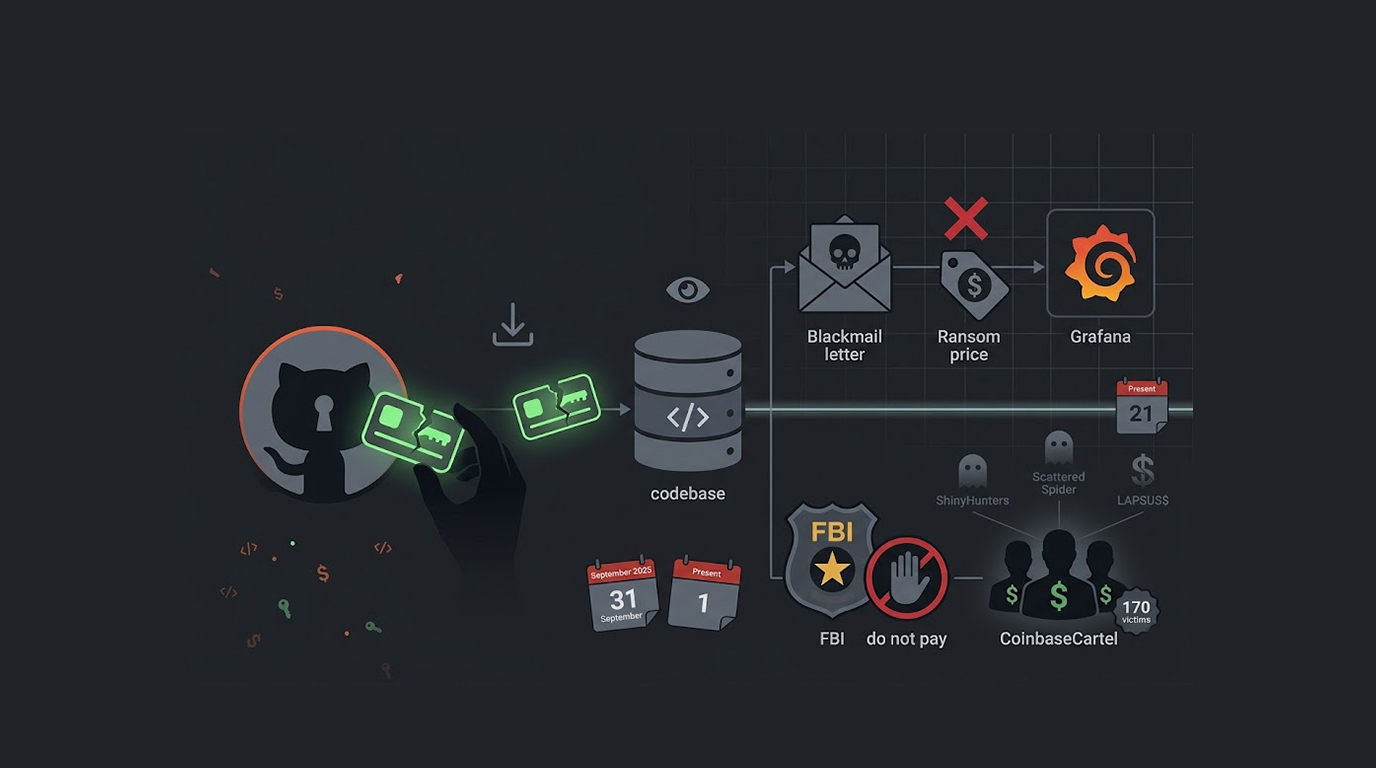
Grafana has disclosed that an unauthorized party obtained a token granting access to the company's GitHub environment, and the attacker used this access to...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067