Miasma Supply Chain Attack Hits 73 Microsoft GitHub Repos
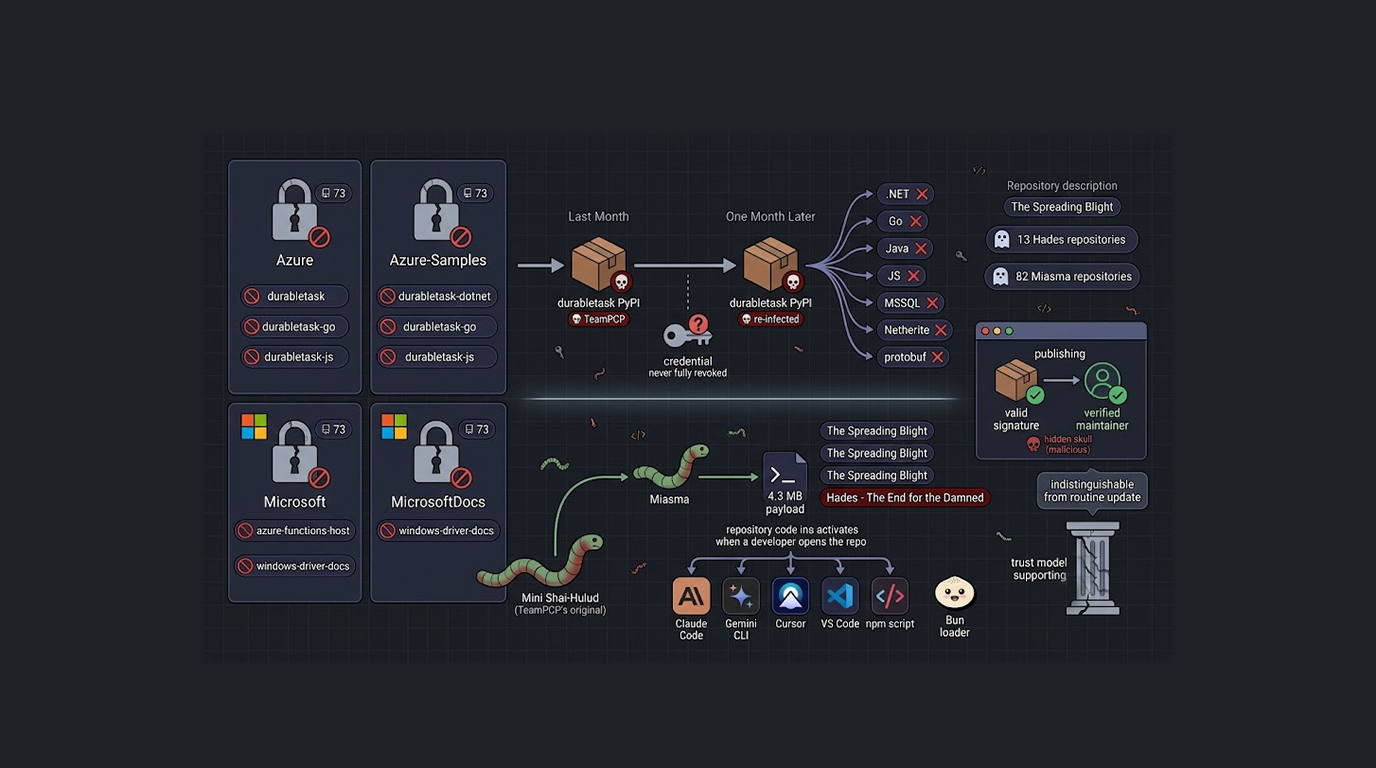
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
Found 36 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
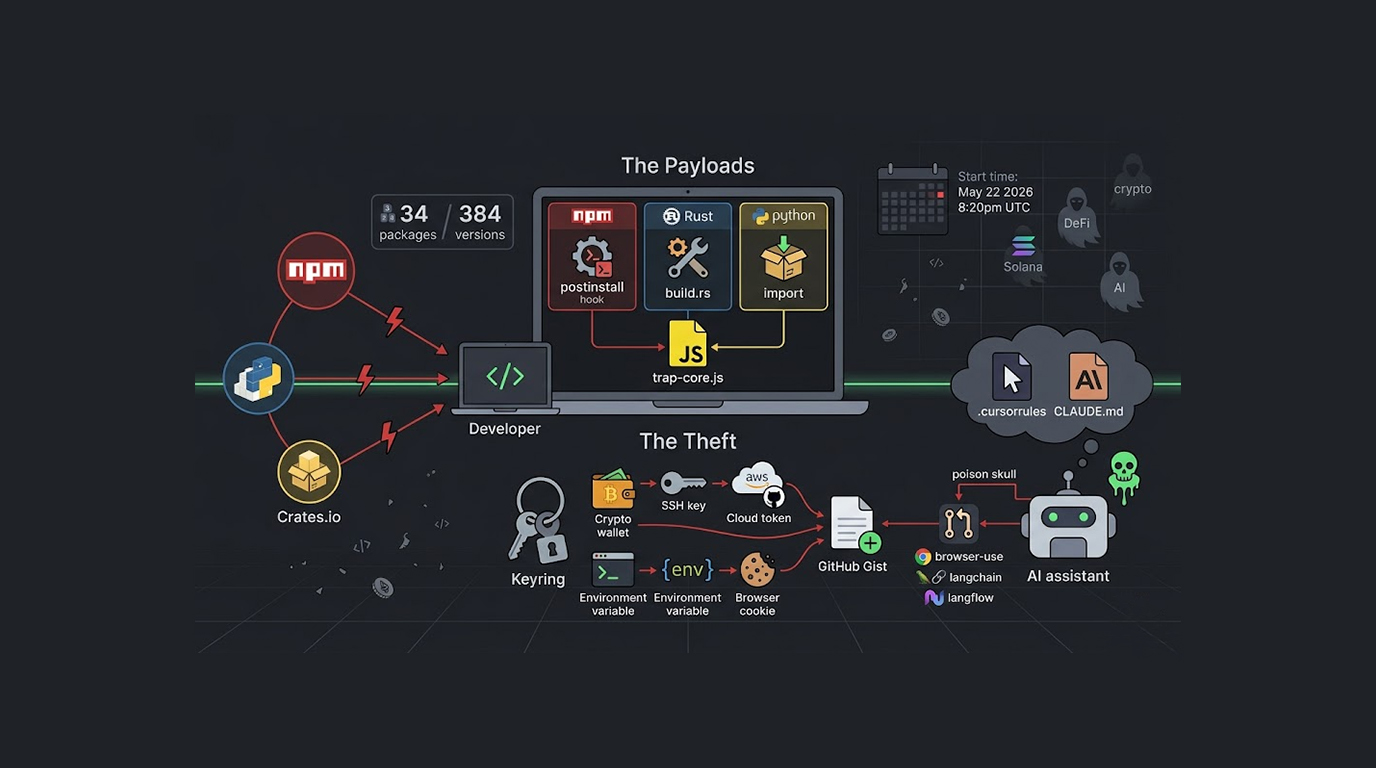
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
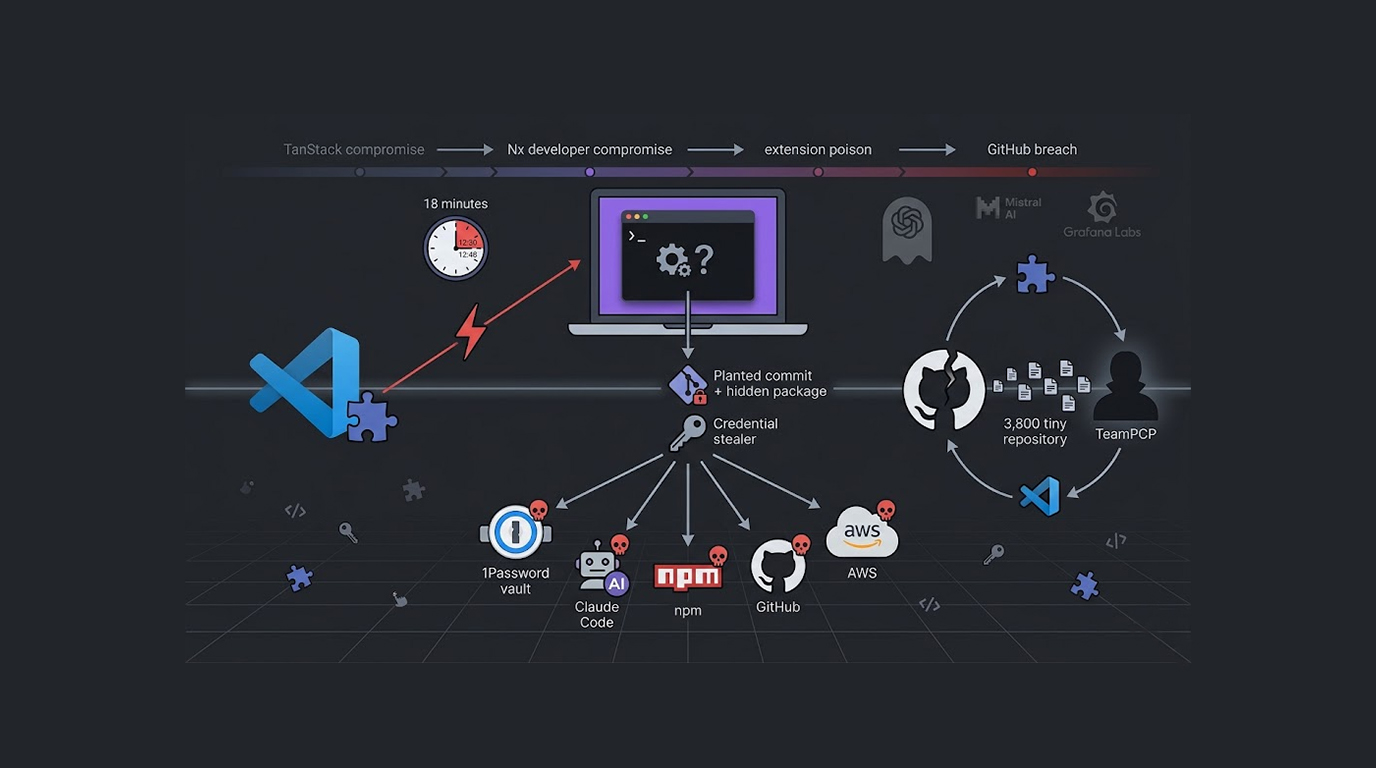
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
There have been large changes to the Internet in the last few decades. Twenty years ago the focus of digital policy was on spam filtering and domain names....
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
The threat of ransomware continues to be one of the most damaging cyber threats. Experts also believe that the evolution of ransomware will continue at an...
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
In 2026, malware developers are becoming interested in Zig due to its use as a modern day replacement for C as a systems programming language. Whereas legi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067