ViteVenom npm Malware Uses Blockchain C2 for RAT Delivery
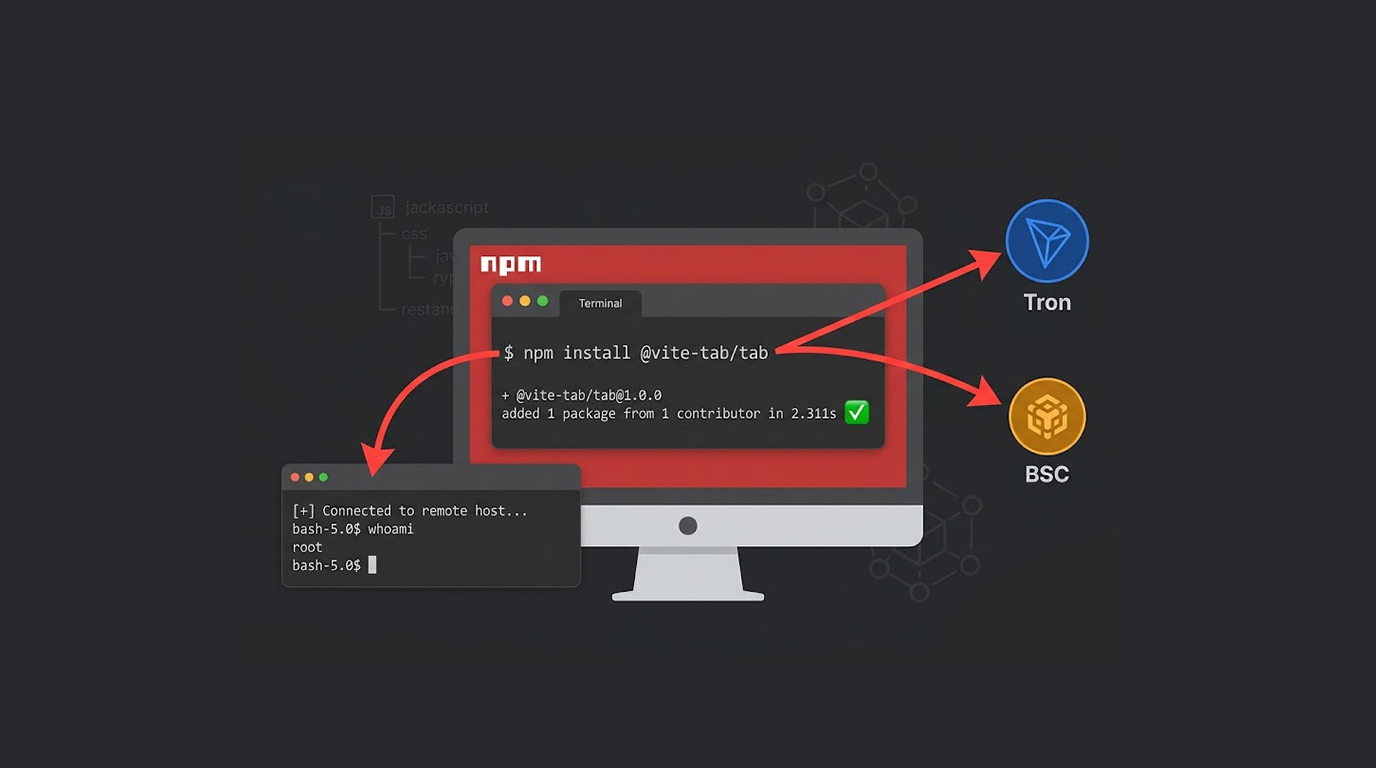
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
Found 41 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
You have Kali Linux installed. You know the basics. But when you are in the middle of a penetration test, you need the right command at the right time. You...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
You are inside the target system. You have a reverse shell. Now you need to get tools onto the target or exfiltrate data from it. Uploading and downloadin...
You are on a penetration test. You find a vulnerability in a web application. You execute a command on the target server. Now you need a way to control tha...
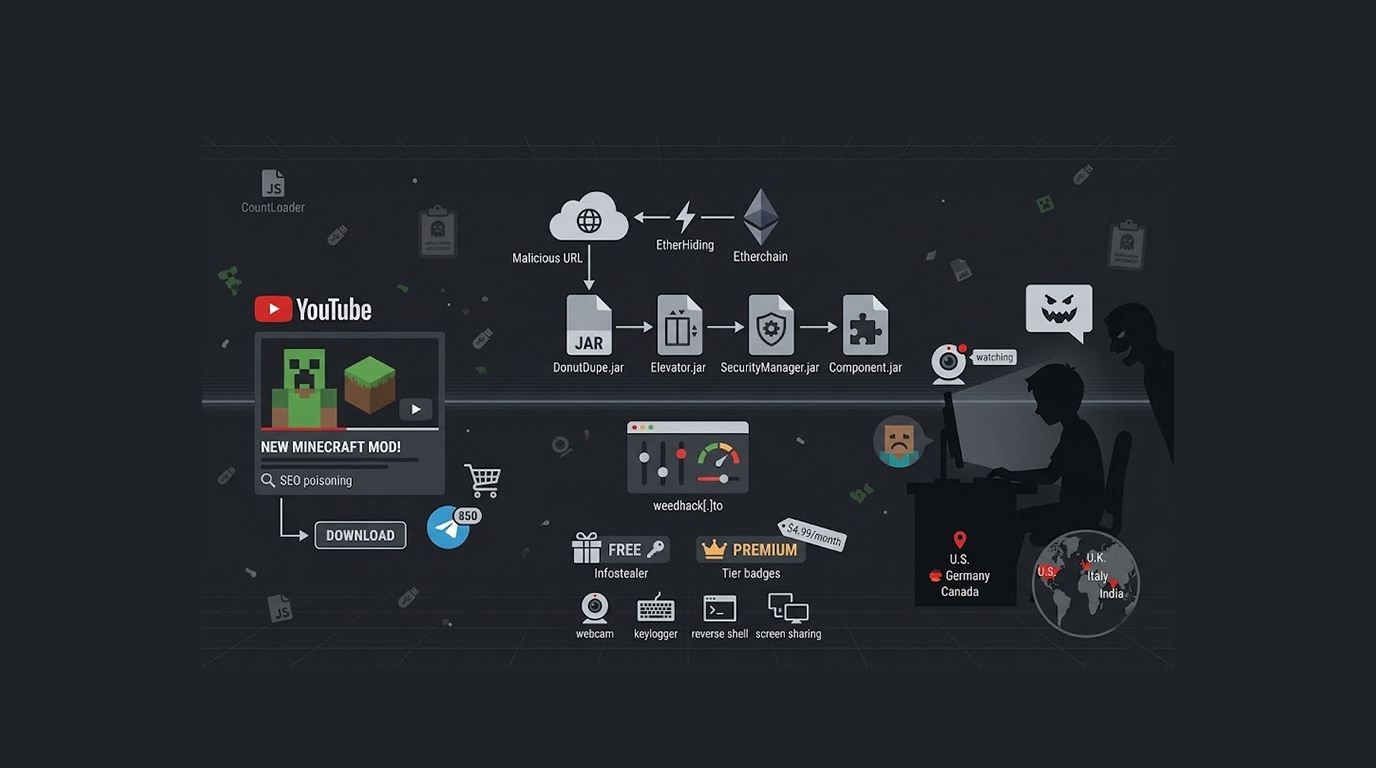
McAfee Labs found a new malware campaign for Minecraft users spread via YouTube videos and SEO poisoning that gives attackers complete control over the vic...
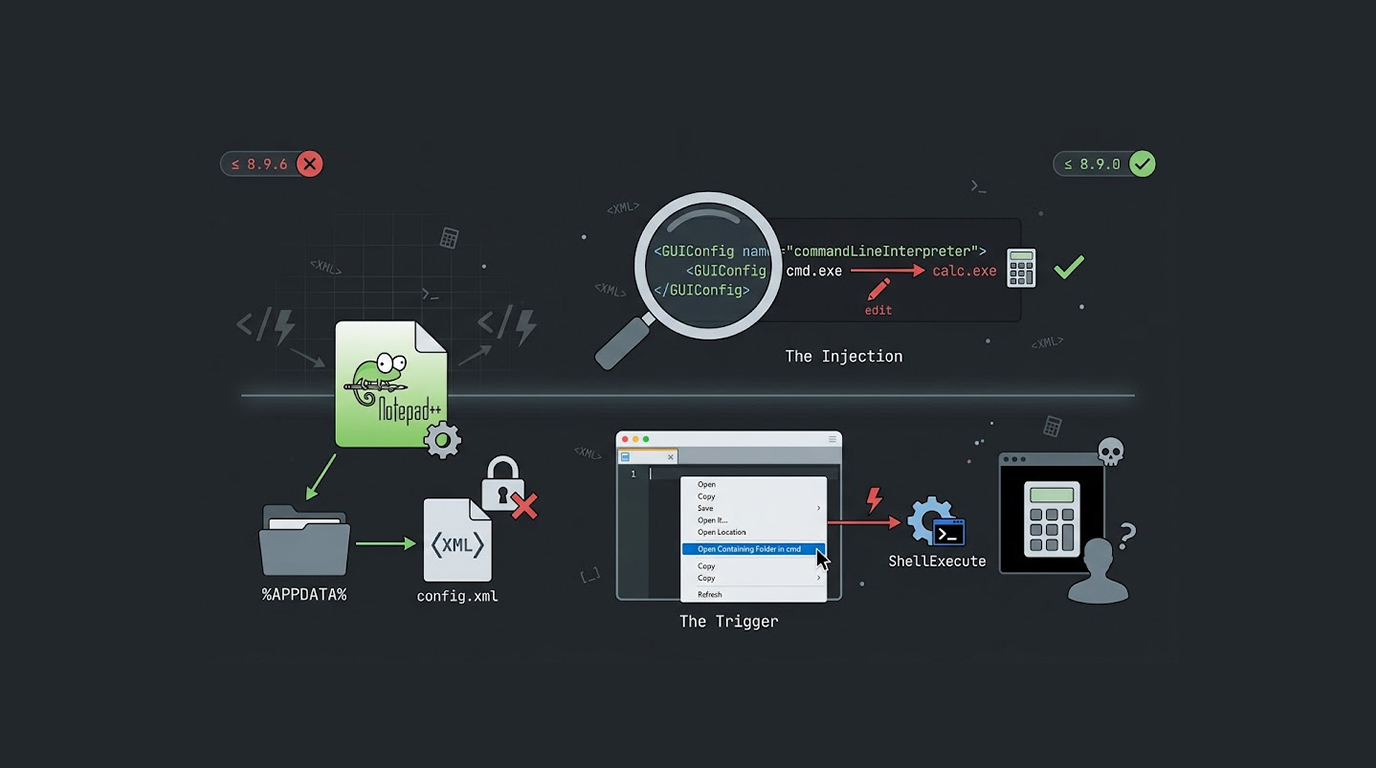
A vulnerability was found in Notepad++ that permits attackers to execute any arbitrary code by modifying a configuration file. The vulnerability affects al...
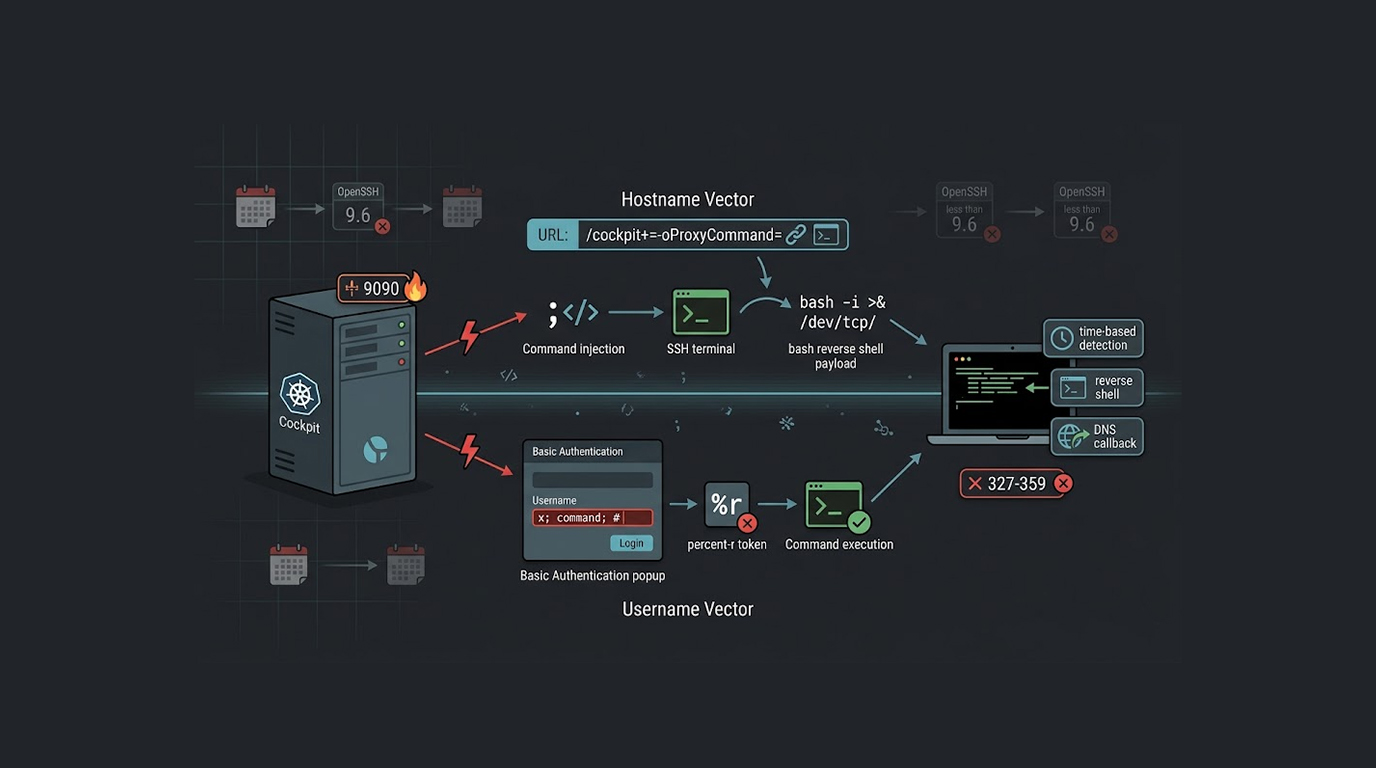
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067